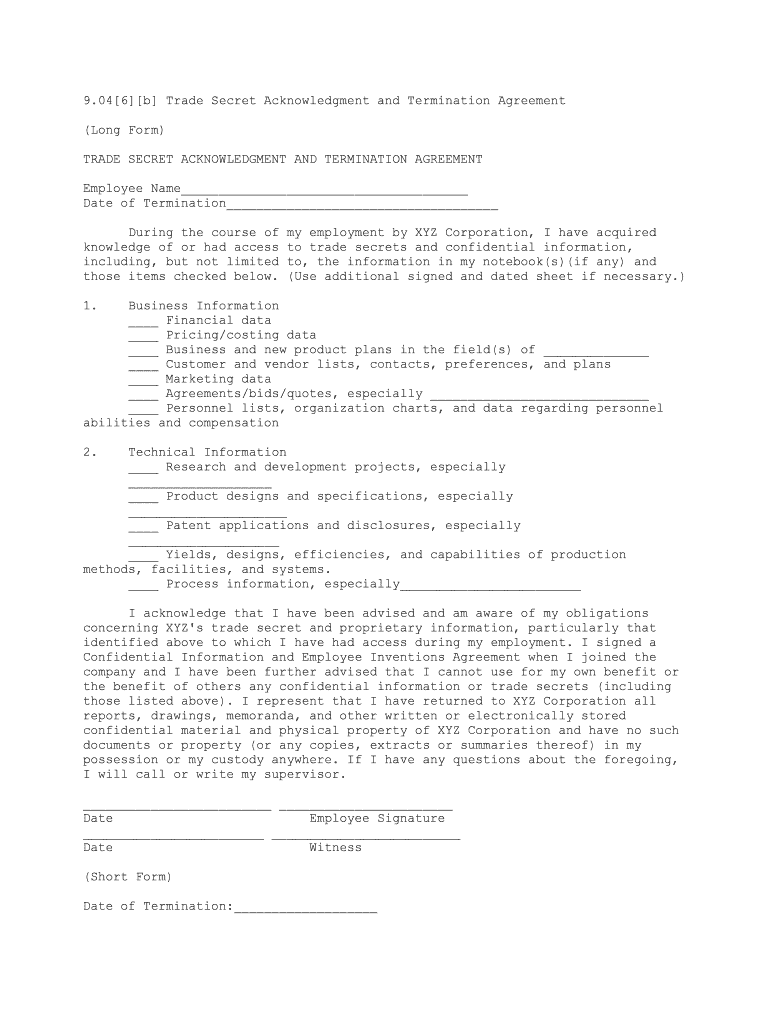
Confidentiality Agreement Shrm Form
Use a Confidentiality Agreement SHRM template to make your document workflow more streamlined.
What this confidentiality agreement does
A Confidentiality Agreement Shrm Form records a promise to protect specified business information from unauthorized use or disclosure. In practice, the agreement identifies the parties, describes confidential information, states permitted uses, sets exclusions and obligations, and records signatures. With signNow, the sender uploads the agreement, reviews or places fillable fields, assigns each field to a signer, sends the document, and stores the completed copy with its audit trail. Electronic execution may be supported by ESIGN and UETA when intent, consent, attribution, and record retention requirements are satisfied.
Who uses this agreement
Human resources
Human resources teams use the agreement before employees, contractors, or candidates receive proprietary policies, compensation data, product plans, or customer information. The sender can assign separate fields, document consent, and preserve the signed record for internal governance without mixing unrelated employment forms.
Business operations
Legal, sales, and operations teams use it before sharing technical, commercial, or transaction information with vendors, advisers, investors, and strategic partners. Role-based sending and an audit trail help identify who received, reviewed, and signed the specific agreement.
Legal standing and evidence
For a U.S. business transaction, an electronically signed confidentiality agreement can be admissible when the parties demonstrate intent, consent, attribution, and reliable record retention under ESIGN, 15 U.S.C. chapter 96, and applicable UETA or New York ESRA rules. Wills, codicils, testamentary trusts, court orders, and specified family-law documents are excluded from ESIGN’s coverage.

How the agreement works
The signNow workflow moves the Confidentiality Agreement Shrm Form from an uploaded document to an assigned, signed, and auditable record.
Upload document: Upload the agreement PDF to signNow. Check fields: Review detected fields and add missing ones. Assign signers: Assign each field to the correct signer. Complete agreement: Send, sign, and retain the completed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail documents the signing evidence surrounding this agreement rather than replacing the agreement’s confidentiality terms or retention policy.
Authenticate signer:
Capture timestamps:
Protect document integrity:
Seal audit record:
Log document events:
Export evidence:
Ways to send and sign the agreement
- Use the signNow web app when preparing a reusable Confidentiality Agreement Shrm Form, assigning fields, reviewing the final layout, and sending it to named recipients.
- Use the signNow mobile app when an authorized employee or business representative must review and sign the agreement from an iOS or Android device.
- Use kiosk mode for supervised, in-person completion when one organization controls the device and needs successive signers to complete agreements without separate email invitations.
- Use a shareable signing link when a controlled distribution channel should let an approved audience open the same agreement, while access and signer instructions remain carefully managed.
Recommended agreement setup
Configure the agreement around signer identity, field ownership, evidence, confidentiality, and the organization’s documented retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification for business signers |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion certificate and action history |
| Document retention | Apply written company retention policy |
| Encryption | Use TLS 1.2/1.3 and AES-256 |
Best practices for this agreement
A careful field map, defined scope, proportionate authentication, and controlled retention make a signed confidentiality agreement easier to use and defend.
Define protected information precisely
Assign every field to its signer
Match authentication to information sensitivity
Preserve the agreement and audit trail
Privacy and disclosure pitfalls
Attaching customer lists, health information, or employee identifiers can expose unnecessary personal data beyond the agreement’s confidentiality purpose. Sending the agreement before confirming each signer’s authority can produce an enforceable-looking record signed by the wrong representative. Failing to capture electronic consent can weaken evidence that a consumer agreed to receive and sign records electronically under ESIGN. Sharing an unrestricted signing link or completed PDF can give unauthorized people access to confidential terms and audit information.
Security for signed agreements
Data in transit:
Stored document data:
Security reporting:
Information security:
Protected health information:
Electronic signatures:
Retention considerations for signed records
A confidentiality agreement does not have one universal federal retention period. Classify the agreement and any attachments before setting a deletion date, then check contract terms, legal holds, industry rules, and state requirements.
Contract term plus policy period
Six years for HIPAA documentation
Three years for tax records
Classify employment records separately
Until legal hold ends
Confidentiality agreement troubleshooting
Resolve field, authentication, plan, and electronic-signature questions before sending a Confidentiality Agreement Shrm Form through signNow.
Can signNow Business handle this agreement? Yes. Business includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, and SOC 2. For healthcare confidentiality agreements involving protected health information, signNow states HIPAA compliance requires a business associate agreement.
The Business plan includes 100 signature invites per user per year when billed annually, with overage fees. Business Premium adds bulk send, while Enterprise adds advanced signer authentication. Choose the plan according to signer volume and authentication requirements.
A confidentiality agreement can generally be electronically signed when the parties show intent, consent to electronic records, signer attribution, and retain a reproducible record. ESIGN, 15 U.S.C. chapter 96, and applicable state law provide the legal framework.
Upload the agreement to signNow, review its detected fields, and place signature, date, and initials fields manually where needed. Confirm every party has the correct role before sending, because field assignment controls who completes each obligation.
For a consumer-facing transaction, ESIGN requires disclosure of the right to paper records, electronic-access capability, and withdrawal procedures under 15 U.S.C. §7001(c). Obtain the required consent before relying on electronic delivery for consumer records.
The completed agreement and audit trail should be retained according to the organization’s written policy and any applicable industry rule. signNow provides audit trails, while the business must determine the legally appropriate retention period for its records.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.