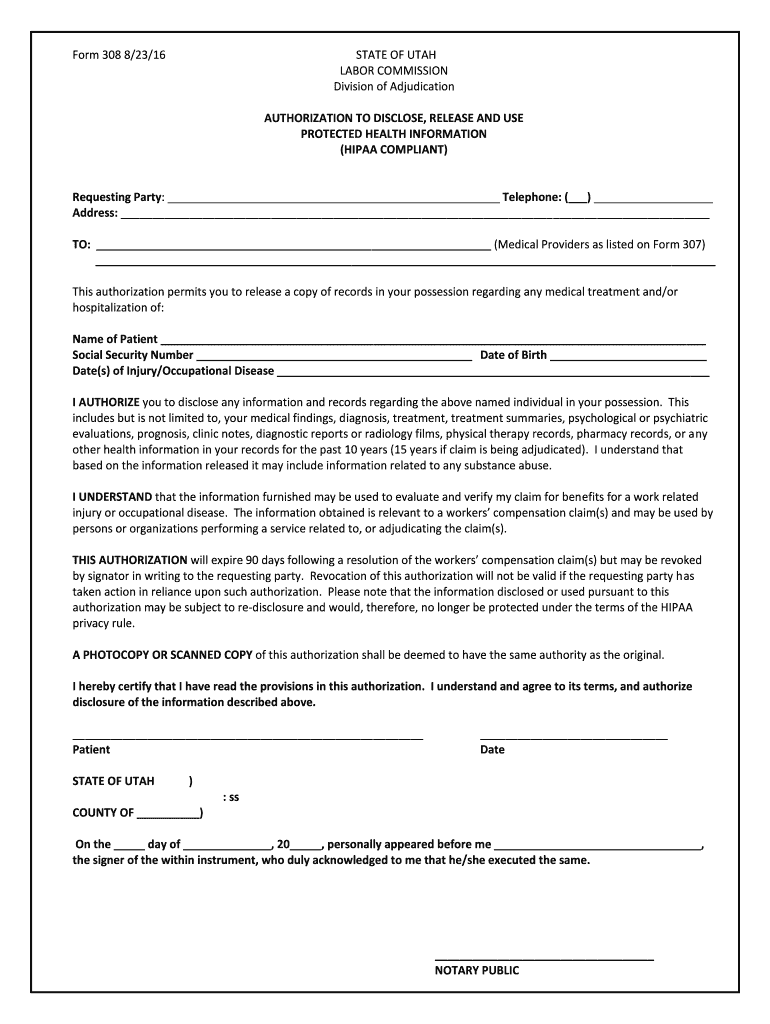
Authorization To Disclose, Release And Use Protected Form
Use a AUTHORIZATION TO DISCLOSE, RELEASE AND USE PROTECTED template to make your document workflow more streamlined.
What this authorization form does
An Authorization To Disclose, Release And Use Protected Form lets an individual specify which protected information may be released, who may receive it, and how it may be used. The signer should identify the person or organization authorized to disclose information, the recipient, the information covered, the purpose, and any expiration or revocation terms stated on the form. In healthcare settings, a HIPAA authorization should describe the information and required notices clearly. signNow can route the completed form for signature and preserve the signed record with an Audit Trail.
Features for protected disclosures
signNow combines field preparation, signer routing, authentication, Audit Trails, and protected storage for Authorization To Disclose, Release And Use Protected Form workflows.
Field detection
Upload the authorization PDF and review automatically detected fields before assigning the signer, recipient, purpose, and expiration information required by the form.
Remote signing
Send the form by email or signing link, allowing the authorized signer to complete it without exchanging editable attachments.
Audit evidence
Capture signer actions, timestamps, and completion details in an Audit Trail connected to the final authorization record.
Reusable templates
Use templates for repeated authorization requests while preserving the specific information scope and recipient for each completed form.
Signer verification
Apply SMS verification or stronger authentication when the sensitivity of the disclosed information requires additional signer assurance.
Protected storage
Keep completed authorizations available through signNow’s encrypted platform controls, with HIPAA workflows requiring a business associate agreement.
Complete the authorization in signNow
Use this sequence to prepare the Authorization To Disclose, Release And Use Protected Form, obtain the required signature, and preserve evidence.
Upload form:
Upload the authorization PDF. Review fields:
Let signNow detect fields. Assign roles:
Add the signer and recipient. Send form:
Send for secure signature. Archive evidence:
Store the signed record and Audit Trail.
Recommended authorization workflow setup
Configure the workflow around signer identity, documented consent, protected records, and the retention rule applicable to the information disclosed.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS verification for sensitive disclosures |
| Signature type | Electronic signature with signer intent |
| Audit trail | Export with the completed authorization |
| Document retention | Six years when HIPAA applies |
| Encryption | TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the Audit Trail records
The signNow Audit Trail provides a chronological evidence record for the authorization’s signer, actions, completion, and final document.
Signer authentication:
Timestamp capture:
Document history:
Completion seal:
Access events:
Evidence export:
Security for protected authorizations
Encryption controls:
Health data protection:
Independent assurance:
Security management:
Privacy framework:
Electronic signature law:



Privacy and disclosure pitfalls
An authorization that does not identify the information, recipient, purpose, or expiration can fail to establish clear permission for disclosure. Sending protected information to an unintended recipient creates an access-control problem even when the authorization itself was signed. Editing a completed authorization outside the signing workflow can weaken the connection between the signer’s consent and the final document. Using a template without reviewing each patient’s or client’s scope can disclose more information than the signer approved.
Limits and exclusions to check
Unclear authorization
Unauthorized disclosure
Weak attribution
Invalid release
Legal standing and scope
For U.S. business transactions, an electronic authorization can be admissible when the signer shows intent, consents to electronic records, can be attributed to the signature, and the record remains reproducible under ESIGN and applicable UETA law. Wills, court orders, and certain family-law documents remain outside those frameworks.

Retention and record-keeping practices
Keep the signed authorization, its audit evidence, and disclosure history together while applying the rule that fits the information released.
Retain the authorization six years
Export the Audit Trail with the form
Restrict access to named recipients
Track scope and revocation status
Troubleshooting authorization workflows
These answers address field detection, signer evidence, plan selection, HIPAA handling, and retention for this authorization workflow.
Upload the exact authorization PDF again, then review signNow’s detected fields before sending. Add or correct signature, date, initials, recipient, and expiration fields manually when the source PDF lacks recognizable field markers.
The signNow Business plan includes templates, audit trails, and mobile apps. If the workflow requires bulk send, Business Premium adds that feature; do not assume bulk distribution is included in every plan.
Use signNow’s audit trail to preserve the signer’s email, timestamps, actions, and completion record. For HIPAA workflows, signNow states that a BAA is required for HIPAA compliance.
Require the signer to review the authorization’s information scope, recipient, purpose, and expiration before signing. ESIGN and UETA support electronic signatures when intent, consent, attribution, and record retention are established.
A recipient should not rely on a signed form that omits the information category, disclosure recipient, purpose, or required expiration language. Correct the authorization and obtain a new signature rather than editing the completed record.
signNow provides audit trails and encrypted storage controls, but the organization must apply its own HIPAA access policy and retention schedule. HIPAA requires six-year retention for specified documentation under 45 CFR §164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.