The Common Pain Application Pain Management Center Paincenter Stanford Form
Create a custom The Common Pain Application Pain Management Center Paincenter Stanford 0 that meets your industry’s specifications.
What this pain application does
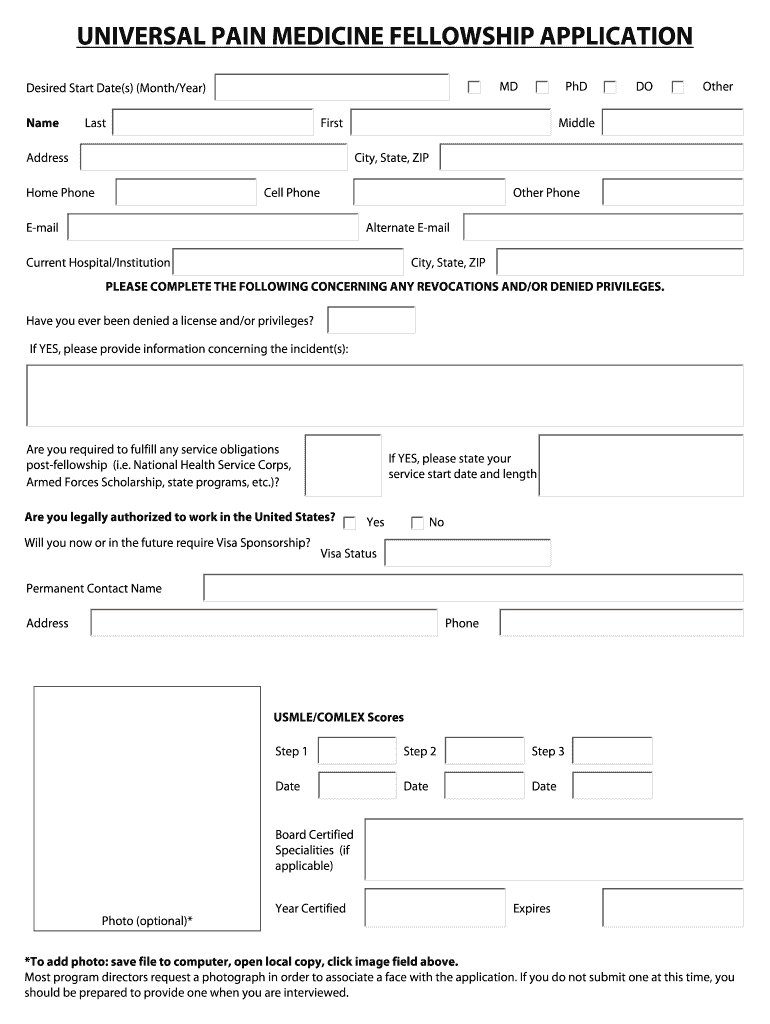
The Common Pain Application Pain Management Center Paincenter Stanford Form is a patient intake and evaluation document for pain-management services. It gathers the patient’s identifying information, pain history, symptoms, treatment history, medication information, and relevant consent details for clinical review. With signNow, a clinic can upload the form, detect or place fillable fields, assign patient and staff roles, send the application for completion and signature, and retain the completed record with its audit trail. Clinical teams should confirm required fields and privacy procedures with their compliance program before use.
Who benefits from this pain application
This Stanford pain application is most useful where patient details, clinical review, and signed consent must move together securely.
Solo pain practitioners can use the form to collect patient history, pain descriptions, medication details, and consent information before an appointment. Pain management clinics can route completed applications from patients to clinicians, preserving signatures, timestamps, and supporting records in one auditable workflow. Hospital pain programs can standardize applications across locations, assign controlled access, and connect completed forms with approved healthcare storage and review processes.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses this pain application
Pain centers
Pain management clinics use the application to collect patient history, symptoms, medication information, treatment details, and consent before clinician review.
Patients and clinicians
Patients complete the Stanford application while clinicians and authorized administrative staff review, sign, route, and preserve the resulting clinical record.
Features for this pain application
signNow organizes the Stanford pain application from field preparation through patient signature, clinical review, audit evidence, and protected retention.
Verified fields
Upload the Stanford pain application and place or verify fields for patient identifiers, pain history, medications, treatment history, consent, and signatures before distribution.
Role-based routing
Send the same approved pain application to patients and clinical reviewers with assigned roles, reducing manual handoffs between registration and assessment.
Signed intake
Collect patient signatures electronically while preserving consent evidence, timestamps, and the completed application for authorized clinical review.
Audit evidence
Keep the completed application and audit trail together so staff can reconstruct who accessed, reviewed, and signed the record.
Flexible completion
Use mobile apps or kiosk mode for patient completion when intake occurs away from a staff workstation or during an in-person clinic visit.
Privacy controls
Apply HIPAA safeguards, encryption, and controlled access to patient information when the clinic configures the required agreement and internal procedures.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the pain application moves
The workflow follows the application from field preparation through clinical review, signature, and controlled record storage.
Upload the form: Upload the Stanford pain application and inspect its patient, clinical-history, consent, and signature fields. Check fields: Use auto-detection where available, then verify every detected field against the original application. Assign recipients: Assign patient, clinician, and administrative recipients with the correct signing or review order. Store the record: Send the completed application and retain the signed PDF with its audit trail.
What the audit trail records
The audit trail connects the patient’s signed Stanford pain application with identity, timing, document history, and authorized retrieval.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Export evidence:
Archive securely:
Ways to complete the pain application
- Use the signNow web app when staff prepare the Stanford pain application, check clinical fields, assign recipients, and monitor completion from a clinic workstation.
- Use the signNow mobile app when authorized staff or patients need to review and sign the pain application from a supported mobile device.
- Use kiosk mode for supervised in-clinic completion when a patient fills out and signs the application at a designated registration station.
- Use a shareable signing link when a clinic needs to distribute the same approved pain application through an established patient communication channel.
Recommended workflow configuration
Configure the Stanford pain application around patient identity, clinical privacy, signature evidence, and documented retention responsibilities.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with consent |
| Audit trail | Enabled with completion certificate |
| Document retention | 6 years for HIPAA records |
| Encryption | AES-256 at rest and TLS 1.2/1.3 |
Security for patient applications
HIPAA protection:
Stored data:
Data transmission:
Security controls:
Information security:
Regulated records:



Record-keeping practices for this form
Retain the completed application as a clinical record, with a documented privacy and access process.
Apply the correct retention period
Export the audit trail
Restrict application access
Validate every clinical field
Troubleshooting the Stanford pain application
Resolve field, routing, privacy, legal, plan, and record-preservation questions before the completed application enters clinical review.
Upload the original Stanford pain application again, then compare each detected field with the source PDF. Auto-detection can miss or misread fields, so verify patient identifiers, pain-history questions, consent language, and signature fields before sending. Correct placement manually when necessary.
Use signNow’s recipient roles and routing order to separate patient completion from clinician review. Confirm that the patient receives only fields intended for patient input and that clinical reviewers receive their assigned fields before sending the application.
For HIPAA-covered patient information, confirm that the clinic has the required signNow BAA and has configured access, disclosure, and retention procedures. HIPAA compliance also depends on the clinic’s people, policies, and safeguards, not the platform alone.
An electronic signature can support the application when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains reproducible. ESIGN, 15 U.S.C. ch. 96, and applicable state law provide the legal framework.
The Business plan includes templates, audit trails, and mobile apps at $8/user/month when billed annually. If the clinic needs bulk sending, Business Premium is listed at $15/user/month annually; confirm plan limits before distributing applications at scale.
Export the completed Stanford pain application together with its audit trail and completion evidence. Store both under the clinic’s approved record policy, restrict access, and apply HIPAA’s six-year retention rule when the record falls within 45 CFR §164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.