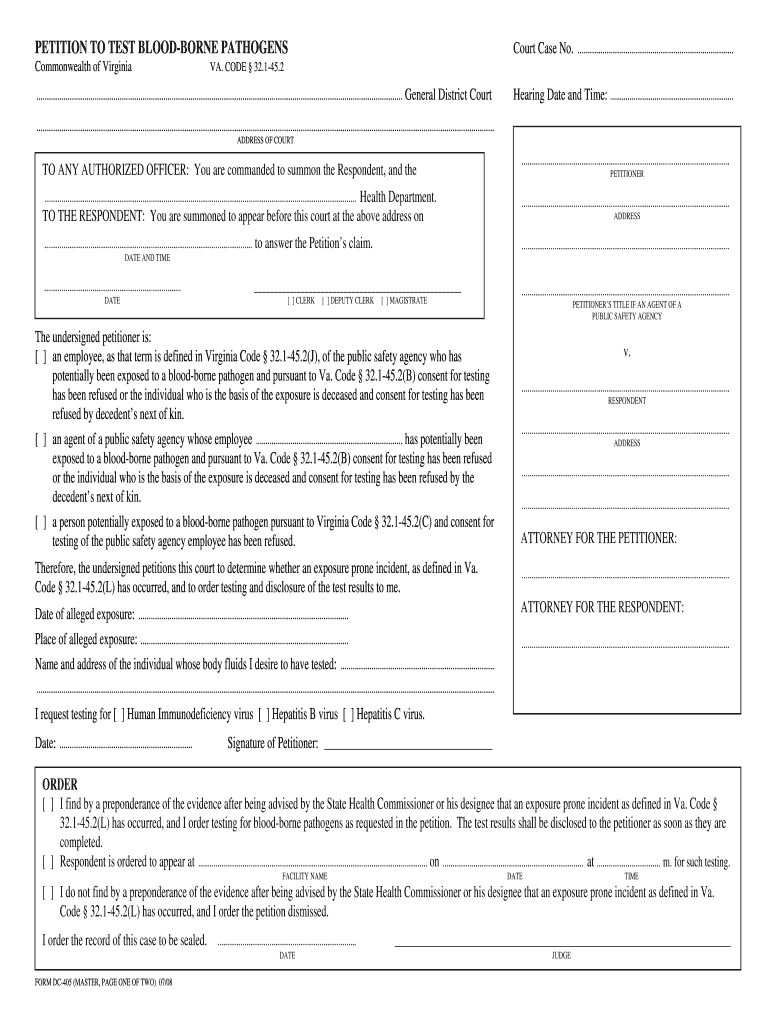
DC 405 Petition To Test For Blood Borne Pathogens Master, Pgs 1 2 Final 7 08 Form
Use a DC 405 Petition To Test For Blood Borne Pathogens MASTER, Pgs 1 2 FINAL 7 08 doc template to make your document workflow more streamlined.
What the DC 405 petition does
The DC 405 Petition To Test For Blood Borne Pathogens Master, Pgs 1 2 Final 7 08 Form is a two-page document used to request and document testing related to a potential blood-borne-pathogen exposure. It identifies the testing request and captures the required participant information, acknowledgments, dates, and signatures shown on the form. In signNow, a sender uploads the petition, reviews detected fields, assigns fields to authorized signers, sends it for completion, and retains the signed PDF with its audit trail. Health organizations should verify current District of Columbia requirements before use.
Who uses this testing petition
Healthcare providers
Healthcare providers and occupational-health teams use this petition to document a blood-borne-pathogen testing request after an exposure incident, keeping the patient, source individual, and authorized reviewers aligned on consent and follow-up.
Legal and risk teams
Legal and risk teams coordinate the petition, testing authorization, and supporting records while limiting access to people handling the exposure investigation.
Organizations that use this petition
The DC 405 petition is most relevant to healthcare and risk-management organizations responding to possible occupational exposure to blood-borne pathogens.
Healthcare clinics can use the petition to collect authorized signatures after an occupational exposure, then preserve the request and completion evidence with the incident record. Hospital risk departments can coordinate source-patient and exposed-worker workflows while restricting petition access to designated clinical, legal, and compliance personnel. Regional health systems can standardize the two-page petition through controlled templates, delegated sending, and centralized retention policies across participating facilities.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Key features for this petition
The workflow keeps the DC 405 petition’s fields, signatures, authentication events, and completed-record evidence together for controlled review.
Field preparation
Upload the DC 405 petition and review detected fields before assigning each signature, date, consent, or acknowledgment field to the correct participant.
Role assignment
Assign the exposed person, source individual, clinician, or authorized representative to only the fields required for that person’s role.
Electronic signing
Capture signer intent through signNow’s electronic-signature workflow while preserving the completed petition and certificate of completion.
Audit trail
Use an audit trail recording signing activity, timestamps, and document events so reviewers can reconstruct how the petition was completed.
Controlled access
Apply access controls and signer authentication appropriate to sensitive health information handled during an exposure investigation.
Record storage
Store the final petition with its completion evidence so authorized healthcare, legal, and risk personnel can retrieve one consistent record.
How to complete the DC 405 petition
Prepare the two-page petition in signNow, verify its assigned participants, and preserve the completed document with its signing evidence.
Upload form:
Upload the two-page DC 405 petition into signNow. Check fields:
Review detected fields and add missing signature or date fields. Assign roles:
Assign each field to the authorized participant or reviewer. Send petition:
Send the petition through signNow’s signing workflow. Store record:
Review the signed PDF and audit trail before storage.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended petition workflow setup
Configure the DC 405 petition around verified signer identity, protected health information controls, audit evidence, and documented retention obligations.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with intent |
| Audit trail | Enabled with completion certificate |
| Document retention | Six years for HIPAA records |
| Encryption | TLS 1.2/1.3 and AES-256 |



Security for sensitive petition data
HIPAA safeguards:
SOC 2 Type II:
ISO 27001:
Data at rest:
Data in transit:
Privacy frameworks:
Privacy and disclosure pitfalls
Including diagnosis, exposure, or contact details in unrestricted copies can disclose sensitive health information beyond the authorized review group. A missing signer consent or incomplete acknowledgment can leave the testing request unsupported during later medical or legal review. Sending the petition to an unintended recipient can expose personally identifiable information and compromise the incident-response record. Retaining the completed petition without its audit trail can weaken evidence showing who signed, when, and whether the record changed.
Record-keeping practices for the petition
Protect the petition as a sensitive exposure-response record by controlling access, preserving signing evidence, and applying the retention rule that governs the underlying health documentation.
Export the petition and audit trail
Limit access before sending
Apply the correct retention period
Review every assigned field
What the petition audit trail records
The audit trail links the DC 405 petition’s signing actions to the final document, helping authorized reviewers evaluate completion and record integrity.
Authenticate signer:
Capture timestamp:
Seal record:
Verify document:
Export evidence:
Archive securely:
Rollout and retention for this petition
Use a controlled rollout sequence, then align completed petition retention with HIPAA requirements and the organization’s documented records policy.
Prepare petition:
First send:
Team onboarding:
Seven-day trial:
Complete signing:
Audit export:
HIPAA retention:
Policy review:
Troubleshooting the testing petition
Use these answers to resolve field, authentication, privacy, and record-preservation questions while preparing the DC 405 petition.
Which signNow plan supports this petition workflow?
Can signNow protect health information in this petition?
Why are petition fields not detected after upload?
How can I require stronger signer authentication?
Does Business Premium support multiple testing requests?
How do I preserve the completed petition as evidence?
Legal standing and record value
An electronically signed DC 405 petition may support a U.S. record when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains reproducible. ESIGN, 15 U.S.C. ch. 96, and applicable state law support electronic signatures, but they do not replace requirements for wills, court filings, family-law decrees, or other excluded documents.

Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.