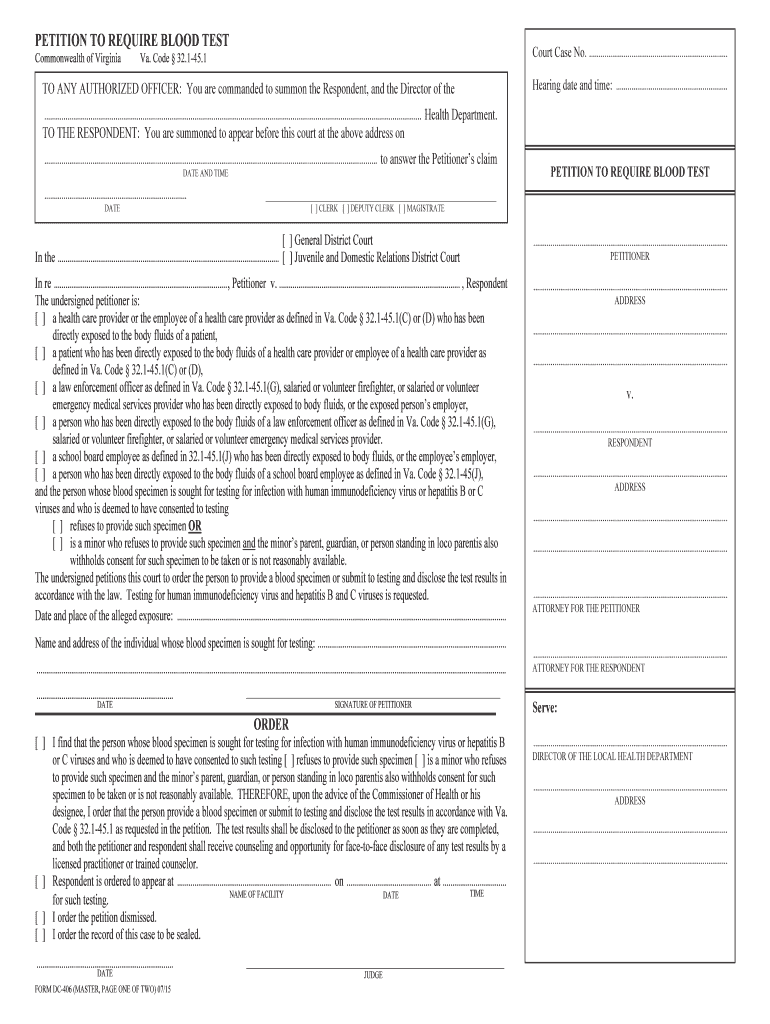
DC 405 Petition To Test For Blood Borne Pathogens Master Form
Use a DC 405 Petition To Test For Blood Borne Pathogens MASTER template to make your document workflow more streamlined.
What the DC 405 petition is
The DC 405 Petition To Test For Blood Borne Pathogens Master Form is a petition used to request testing after an exposure involving potential blood-borne pathogen transmission. The petitioner provides the incident and identifying information requested by the form, completes any required attestations, and signs the finished record. With signNow, the official file can be uploaded, fillable fields reviewed, signature fields placed, and the petition sent to the designated signer. The completed form and audit trail can then be retained for review, subject to the receiving authority’s instructions.
Who uses the DC 405 petition
Public health offices
Public health offices, healthcare organizations, and authorized legal representatives can use the petition workflow to collect required identifying information, exposure details, signatures, and supporting records while limiting access to sensitive health information.
Exposed individuals
Individuals seeking testing after a documented exposure can prepare the DC 405 petition electronically, review every field, sign where required, and share the completed record with the designated receiving authority.
Teams that manage DC 405 petitions
A public-health coordinator can prepare a reusable DC 405 template, assign fields to the petitioner, and monitor whether the testing petition has been completed. Role-based access helps separate template administration from handling sensitive exposure information. A healthcare compliance lead can route signed petitions through an auditable workflow, verify completion evidence, and preserve the final document with its audit trail. HIPAA-covered organizations should configure access and retention around their obligations under 45 CFR §164.530.
How to complete the DC 405 petition
Use this workflow to prepare the petition, route it to the appropriate signer, and preserve the completed record.
Upload the form:
Upload the official DC 405 file to signNow. Check the fields:
Review detected fields and add missing signature or date fields. Add the recipient:
Enter the authorized recipient’s email address and sending order. Complete and store:
Send the petition, monitor completion, and preserve the signed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Ways to send and sign the DC 405 petition
- Use the signNow web app when a coordinator needs to upload the DC 405 file, review fields, assign recipients, and monitor completion from a desktop workflow.
- Use the signNow mobile app when an authorized petitioner or coordinator must review and sign the DC 405 petition from an iOS or Android device.
- Use kiosk mode when staff supervise repeated in-person completion on an organization-controlled device and need each petitioner to finish a separate signing session.
- Use a shareable signing link when the same approved DC 405 template must reach petitioners through a controlled channel without creating an individual email invitation first.
Challenges when completing the DC 405 petition
Petitioners may omit exposure details, making it difficult to identify the incident, affected parties, and requested blood-borne pathogen testing. Incorrect names, dates, or contact information can delay review and require the petitioner to correct and resubmit the DC 405 form. A missing signature or unclear consent language may prevent the receiving authority from treating the petition as complete. Sensitive health and exposure information requires controlled access, careful sharing, and secure retention throughout the petition process.
Recommended DC 405 workflow setup
Use a controlled signing workflow that protects sensitive petition information and preserves evidence of completion.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with intent evidence |
| Audit trail | Enabled with completion certificate |
| Document retention | Follow the applicable agency policy |
| Encryption | TLS 1.2/1.3 and AES-256 |
What the DC 405 audit trail records
The audit trail documents signing activity separately from form preparation, helping reviewers verify who acted, when, and on which petition.
Signer authentication:
Timestamp capture:
Document history:
Tamper evidence:
Event attribution:
Audit export:
Security for sensitive petition records
TLS 1.2/1.3 and AES-256:
HIPAA compliant with BAA:
SOC 2 Type II certified:
ISO 27001 certified:
ESIGN and UETA compliant:
GDPR compliant protections:
Platform requirements for DC 405 workflows
Prepare and sign the DC 405 petition in Chrome, Edge, Firefox, or Safari on Windows 10, Windows 11, or macOS. The signNow mobile apps support iOS and Android access, while encrypted connections use TLS 1.2 or TLS 1.3.
Browsers Chrome, Edge, Firefox, and Safari support browser-based preparation and signing. Operating systems Windows 10, Windows 11, macOS, iOS, and Android support access. Mobile apps The signNow iOS and Android apps support mobile petition workflows.
Organizations handling exposure information should use managed devices, controlled account provisioning, and role-based access. Enterprise deployments may connect signNow through API or SSO configurations, while HIPAA-covered workflows require a business associate agreement and an appropriate retention policy.



Best practices for the DC 405 petition
Careful field review, controlled access, and complete audit records reduce avoidable corrections when preparing this sensitive testing petition.
Verify every field against supporting records
Lock recurring petition structure before sending
Restrict delivery to authorized recipients
Preserve the petition with its audit trail
DC 405 petition troubleshooting
These answers address field assignment, signer access, electronic-signature evidence, privacy obligations, and plan limits specific to this petition workflow.
Upload the official DC 405 PDF to signNow, then inspect the detected fields before sending. If a field is missing, add it manually and assign it to the correct participant. The Business plan includes templates and audit trails for this preparation workflow.
Confirm that the signer’s email address is correct, resend the invitation, or provide a controlled signing link. The recipient generally does not need a signNow account, but must access the assigned signing request to complete the petition.
Use signNow’s audit trail and completion record to document intent, timestamps, and signing activity. ESIGN and UETA support electronic signatures when intent, consent, attribution, and record reproducibility are established.
A HIPAA-covered organization should use signNow’s HIPAA-compliant configuration and obtain a business associate agreement. HIPAA documentation requirements can include six-year retention under 45 CFR §164.530(j), subject to the record’s classification.
The Business plan is listed at $8 per user per month with annual billing, while Business Premium is $15 and adds bulk send. Paid plans include 100 signature invites per user per year, with overage fees applying.
If a petition requires notarization, in-person identity proofing, or submission through a specific public-health authority, verify that requirement separately. Electronic signing does not replace a mandated notarial act or agency filing procedure.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.