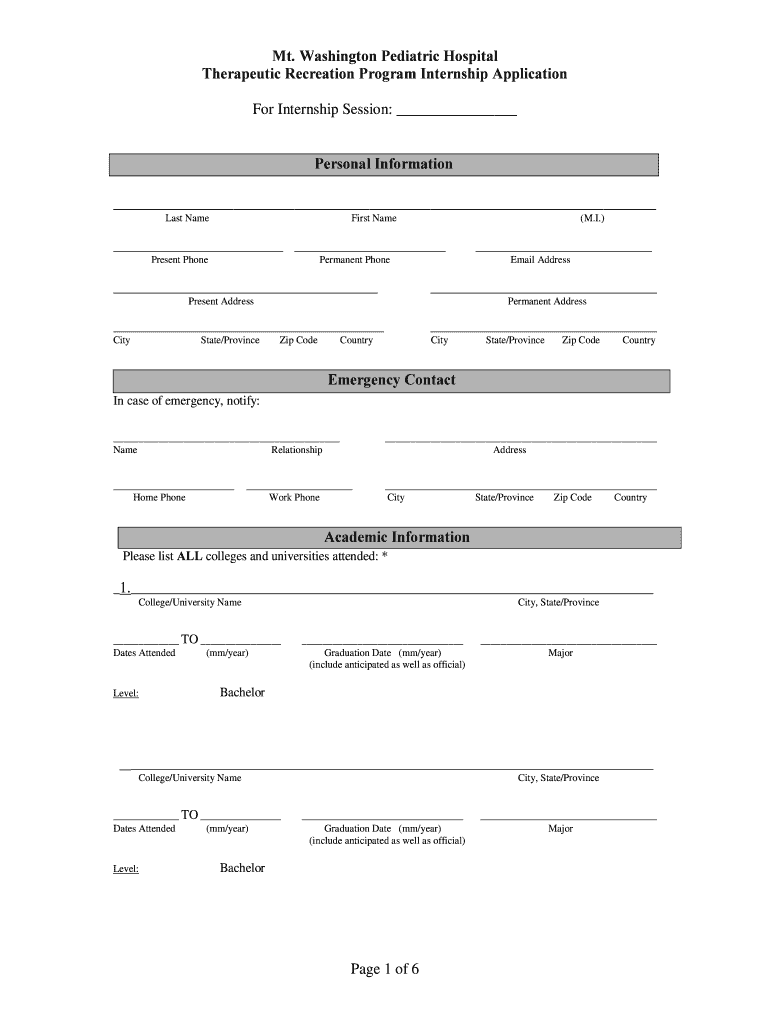
Mwph Therapeutic Recreation Application Form
Create a custom Mwph Therapeutic Recreation Application Pdf Form 0 that meets your industry’s specifications.
About the recreation application form
The Mwph Therapeutic Recreation Application Form is an intake document for collecting information and approvals connected with therapeutic recreation participation. The available source information does not identify a federal issuing agency, statutory filing deadline, official form code, or universal required field list. In signNow, an organization can upload its PDF, review detected fillable fields, add participant or guardian signature fields, send the document for electronic completion, and retain the signed file with an audit trail. If the application contains protected health information, the organization should evaluate HIPAA duties and applicable state requirements before deployment.
Who uses this recreation application
Community recreation programs
Community recreation programs can collect participant details, guardian approvals, emergency contacts, accommodations, and activity consent in one controlled application workflow.
Healthcare recreation providers
Healthcare-connected recreation services can route applications containing protected health information through a signNow workflow after confirming HIPAA responsibilities and a business associate agreement.
How this application workflow works
signNow turns the Mwph Therapeutic Recreation Application Form into a routed electronic workflow from upload through signed-record storage.
Upload document: Upload the recreation application PDF to signNow. Prepare fields: Review detected fields and complete the participant workflow. Request signatures: Send to the participant or guardian for signing. Retain record: Store the signed application with its audit trail.
How to complete the application
Use this sequence to prepare, route, sign, and retain the Mwph Therapeutic Recreation Application Form in signNow.
Upload:
Upload the completed application PDF. Check fields:
Review detected fields and add missing fields. Assign:
Assign participant, guardian, and staff recipients. Send:
Send the application for electronic signatures. Archive:
Store the signed PDF with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended application workflow setup
Configure the application workflow around participant identity, informed electronic consent, limited staff access, and defensible record retention.
| Setting | Recommendation |
|---|---|
| Authentication and provisioning | Two-factor authentication with role-based staff access |
| Signature type | Typed or drawn electronic signature with clear intent |
| Audit trail | Capture signer identity, timestamps, IP, and actions |
| Document retention | Six years when HIPAA 45 CFR 164.530(j) applies |
| Encryption | TLS 1.2 or 1.3 in transit; AES-256 at rest |
Authentication for participant applications
PKI signatures:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Signer attribution:
Privacy risks when handling applications
Including diagnoses, medications, or emergency contacts in every copy can expose more personal information than the recreation program needs. Collecting a signature without recording consent to electronic records may weaken evidence that the applicant intended to sign digitally. Allowing every staff member to open completed applications can expose health information beyond assigned program, intake, or supervisory duties. Sending the application through an unprotected email attachment can create uncontrolled copies of participant information and signed consent records.
Record-keeping practices for applications
Protect the completed application as an operational record, and apply the retention period that matches the information and organization handling it.
Set the retention rule before intake
Export the signed record and audit trail
Restrict archival access by program role
Check state and program requirements
Retention periods for application records
When this application contains protected health information held by a covered entity, apply the HIPAA retention rule to the relevant records.
Six years: application records
Six years: consent records
Six years: authorization records
Six years: guardian records
Six years: audit documentation
What the application audit trail records
The audit trail documents who handled the application, when actions occurred, and how the signed record can be reviewed later.
Authenticate signer:
Capture timestamp:
Hash document:
Seal document:
Log activity:
Retrieve audit trail:
Managing staff access and delegated sending
Program administrators can publish a shared Mwph Therapeutic Recreation Application Form template, control staff permissions, and review completed applications without giving every user unrestricted access to participant information. Intake teams can use delegated sending for participant-specific applications, while supervisors retain administrative control over templates, signer order, audit trails, and completed-record access.
Pricing and features for this form
For a recreation application containing personal information, compare verified signNow details with unavailable competitor data before selecting a workflow.
| Features | signNow | DocuSign | Adobe Sign | PandaDoc | Dropbox Sign |
|---|---|---|---|---|---|
| Starting price | $8/user/month annually | Not verified | Not verified | Not verified | Not verified |
| Free trial | 7 days, no card required | Not verified | Not verified | Not verified | Not verified |
| Bulk sending | Business Premium includes bulk send | Not verified | Not verified | Not verified | Not verified |
| Audit trail | Included with Business plan | Not verified | Not verified | Not verified | Not verified |
| HIPAA compliance | Available with BAA requirement | Not verified | Not verified | Not verified | Not verified |
| Annual invite cap | 100 signature invites per user | Not verified | Not verified | Not verified | Not verified |
Troubleshooting the recreation application workflow
These answers address field detection, signer identity, privacy controls, electronic consent, and retention for this recreation application.
Upload the Mwph Therapeutic Recreation Application Form as a PDF, then review signNow’s detected fields before adding required participant, guardian, emergency-contact, and signature fields. Detection does not determine whether your organization’s intake fields satisfy program or state requirements.
The Business plan includes templates and audit trails, while Business Premium adds bulk send. Choose fields and recipients manually when applications differ by participant, guardian status, accommodation, or program enrollment.
For a covered entity handling protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm the BAA and organization controls before sending this application.
Use two-factor authentication or SMS OTP when the application includes sensitive participant information. Email delivery alone may not provide the identity assurance your program’s access policy requires.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are demonstrated. For consumer-facing records, review the disclosure requirements in 15 U.S.C. §7001(c).
Export the completed application with its audit trail and certificate of completion, then store both under the organization’s retention policy. HIPAA records require six years under 45 CFR 164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.