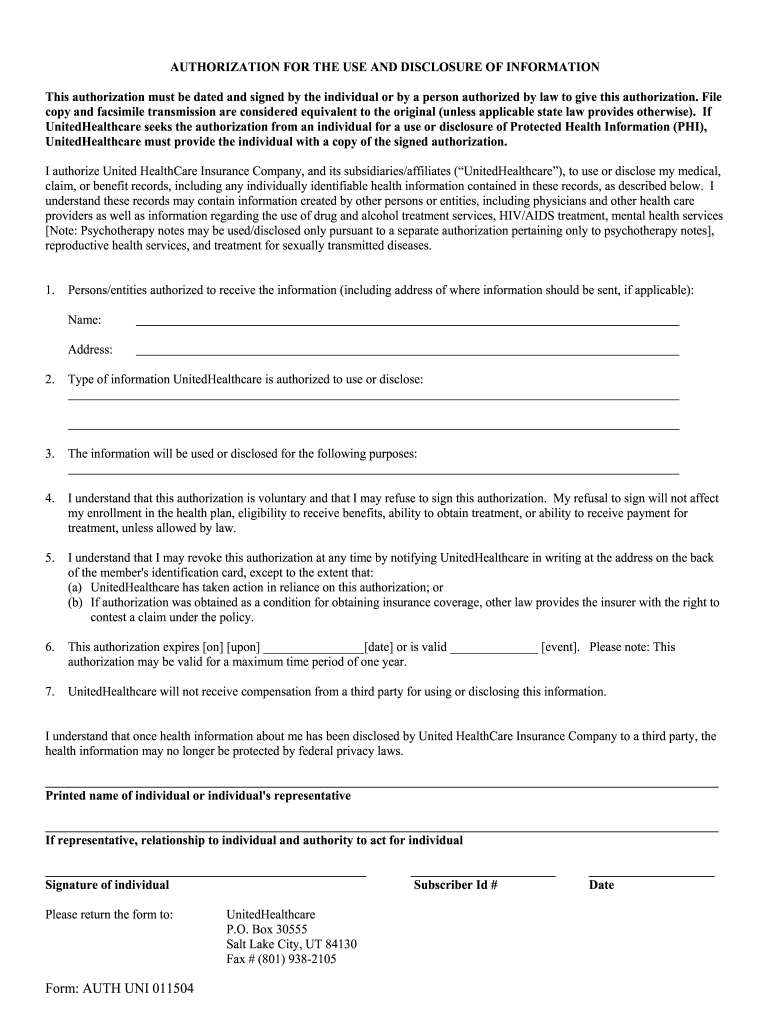
United Healthcare Medical Records Request Form
Create a custom United Healthcare Medical Records Request Form 0 that meets your industry’s specifications.
What the United Healthcare records request form does
The United Healthcare Medical Records Request Form is a patient authorization used to identify requested health information, its recipient, and the permitted purpose of disclosure. The patient or authorized representative completes the relevant fields, selects records and dates, signs the authorization, and submits it to UnitedHealthcare or the designated provider. With signNow, a sender can upload the form, detect fillable fields, route it for an electronic signature, and preserve the completed authorization with an audit trail. HIPAA privacy requirements and the form’s own instructions still control disclosure.
Who uses the form and why
Patients and representatives
Patients and authorized representatives use the form to request specified UnitedHealthcare medical records, identify the receiving party, document the permitted purpose, and provide an auditable authorization before disclosure.
Healthcare organizations
Healthcare providers, insurers, and release-of-information teams use the signed authorization to route records requests, verify scope, protect PHI, and retain evidence of the patient’s consent.
Who works with this authorization form
A patient or authorized representative uses the form to specify the records, dates, recipient, and purpose before authorizing release. In a signNow workflow, the sender can verify required fields, request the signature, and retain the completed authorization for the associated healthcare transaction. A healthcare office or insurance-support team uses the authorization to organize a release request tied to UnitedHealthcare records. Staff can assign signing roles, limit access to the document, and preserve the signed form and audit history for privacy and operational review.
How the form moves through signNow
The signNow workflow mirrors the UnitedHealthcare authorization sequence from document preparation through signed-record retention.
Upload form: Upload the UnitedHealthcare authorization PDF to signNow. Prepare fields: Auto-detect fields and add missing patient or signer fields. Route authorization: Assign the patient or representative as signer and send securely. Archive evidence: Store the signed form with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Steps to prepare and send the form
Follow these steps to turn the UnitedHealthcare authorization into a controlled, signable document without changing its disclosure scope.
Upload form:
Upload the original PDF. Check fields:
Review detected fillable fields. Assign signer:
Assign the patient signer. Send request:
Send the authorization securely. Retain evidence:
Store the signed copy and audit trail.
Recommended authorization workflow setup
Configure the UnitedHealthcare authorization workflow around signer identity, PHI protection, audit evidence, and retention obligations.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Capture timestamps, IP address, and actions |
| Document retention | Six years for HIPAA records under 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 in transit and AES-256 at rest |
Security controls for UnitedHealthcare authorizations
HIPAA protection:
Transit encryption:
Storage encryption:
SOC 2 Type II:
ISO 27001:
Electronic validity:
What the audit trail records
The audit trail supplements the signed UnitedHealthcare authorization with technical evidence about identity, timing, document integrity, and retrieval.
Authenticate signer:
Capture timestamp:
Hash document:
Seal history:
Record consent:
Export audit trail:
Features that support records authorizations
signNow connects the form’s consent fields with controlled routing, electronic signatures, and evidence suitable for healthcare document workflows.
Field detection
Auto-detected fields help the sender convert the UnitedHealthcare authorization into a usable signing template while preserving the form’s patient, recipient, purpose, and records-selection sections.
Required fields
Required fields and signature placement reduce incomplete authorizations, helping staff identify missing patient details or consent information before routing the request.
Remote signing
Email delivery and signing links let authorized parties review the specific records request without coordinating a paper exchange or an in-person appointment.
Audit evidence
A completed authorization can be stored with its certificate of completion and audit history, supporting internal review of consent and document handling.
Access controls
Role-based access helps limit PHI exposure by separating the sender, patient or representative, and records-processing participants within the workflow.
Mobile access
Mobile apps allow a patient or representative to review and sign the authorization from an iOS or Android device when the workflow permits electronic consent.
Privacy and disclosure pitfalls
Including more records or recipients than the patient intended can expand PHI disclosure beyond the authorization’s stated scope. Leaving dates, purpose, or representative details incomplete can delay processing because the authorization may not clearly identify the permitted disclosure. Sending a signed authorization through uncontrolled email or shared folders can expose PHI to people outside the approved workflow. Using an outdated template or altered field labels can create uncertainty about whether the patient authorized the requested records.
Best practices for this authorization
Accurate scope, controlled access, documented consent, and secure retention are the central safeguards for a UnitedHealthcare records authorization.
Preserve the authorization’s original scope
Restrict PHI access by role
Archive the signed record and audit trail
Document electronic consent properly
Retention rules for related records
Retain the completed authorization according to the record category that governs the underlying healthcare transaction and the organization’s state-law policy.
Six years: HIPAA records
Three years: tax records
Three years after hire: I-9
Three years: FLSA payroll
Five years: OSHA injuries
Troubleshooting UnitedHealthcare records requests
These answers address field preparation, signer identity, PHI handling, electronic consent, and plan capabilities for this authorization workflow.
Upload the original UnitedHealthcare Medical Records Request Form as a PDF, then use signNow’s field detection and review every patient, recipient, purpose, and signature field before sending. If detection misses a field, add it manually and test the completed document before production use.
The Business plan includes templates, audit trails, and legally binding eSignatures. For a healthcare workflow involving PHI, confirm that the required HIPAA business associate agreement is in place and configure access, authentication, and retention according to organizational policy.
Use signNow’s SMS OTP or stronger signer-authentication options when the organization requires more than email access. Verify the signer’s identity and preserve the authentication event with the completed authorization and audit trail.
A signing link should identify the intended authorization and recipient, not expose the document broadly. Restrict link distribution, assign the correct signer, and use authentication controls before the patient reviews or signs the form.
If the patient withdraws electronic consent or requests paper records, stop the electronic workflow and follow the organization’s HIPAA procedures. ESIGN consumer disclosures require a paper option, electronic-access capability, and procedures for withdrawing consent.
Business Premium includes bulk send, but a records authorization still requires patient-specific scope and consent. Do not reuse a completed authorization across patients or requests unless the organization’s privacy process expressly permits the template and fields.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.