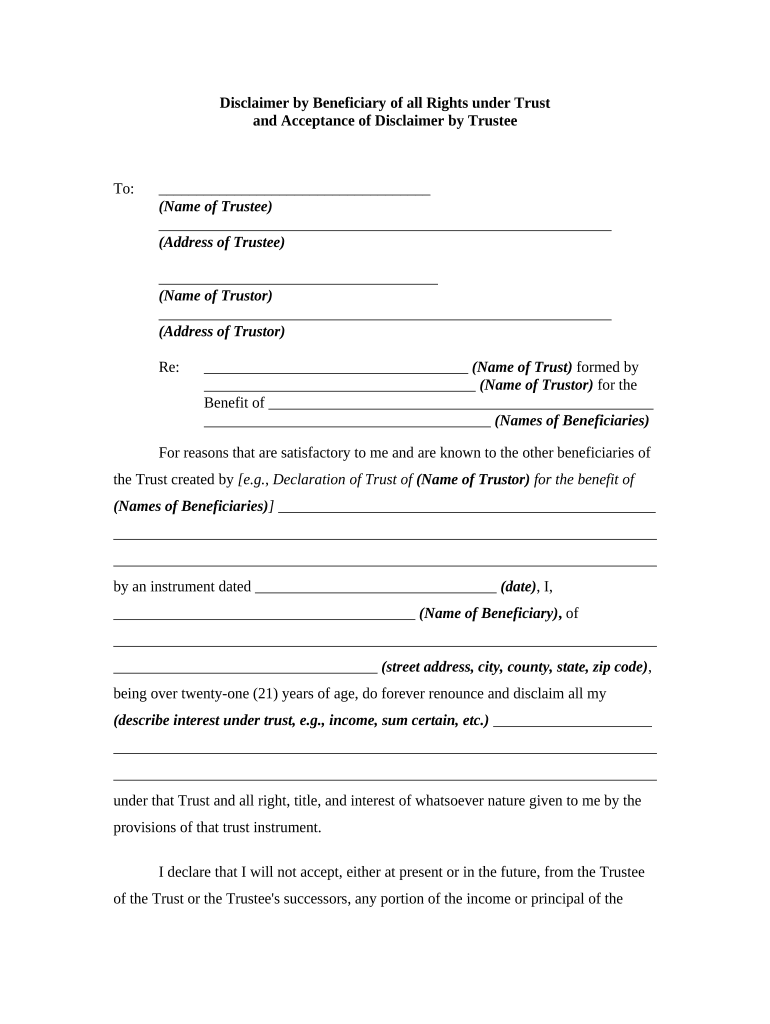
California Disclaimer Form
Use a California Disclaimer template to make your document workflow more streamlined.
What the California Disclaimer Form does
The California Disclaimer Form records a person’s acknowledgment of stated limitations, disclosures, or responsibilities under California-related business circumstances. Its exact legal effect depends on the wording, transaction, signer intent, and applicable state or federal law. In signNow, a sender uploads the form, reviews automatically detected fillable fields, adds signer and date fields, and sends it for electronic signature. The completed PDF is paired with an audit trail showing signing events and document history. A lawyer should review specialized language or exclusions.
Who benefits from this California form
The form is most useful when a California-facing workflow needs consistent acknowledgment, identifiable signers, and a reproducible signed record.
California solo practitioners can use a reusable disclaimer template for client acknowledgments, place signature and date fields once, and send each completed form through an auditable workflow without rebuilding the document for every matter. Real estate and construction businesses can route property, project, or service disclaimers to customers and contractors, while operations administrators control templates, delegate sending, and preserve completed records for later review. Multi-location enterprises can standardize California Disclaimer Form language across departments, assign role-based access, and connect signNow workflows with systems such as Salesforce, NetSuite, or Microsoft 365.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Recommended California disclaimer setup
Use a controlled signing configuration that preserves signer identity, document integrity, and the completed California Disclaimer Form.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enabled with completion certificate |
| Document retention | Organization-approved retention schedule |
| Encryption | TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How to complete this California form
Use this signNow workflow to prepare the exact disclaimer document, collect the intended signature, and preserve evidence of completion.
Upload form:
Upload the approved California Disclaimer Form into signNow. Check fields:
Review automatically detected fields and add missing fields. Add signer:
Add the intended signer and required authentication method. Complete record:
Send the form, collect the electronic signature, and store the completed PDF with its audit trail.
Audit trail for California disclaimers
signNow records the technical evidence surrounding each California Disclaimer Form signing event, from authentication through audit-trail export.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Export evidence:
Privacy challenges with California disclaimers
Personal addresses, identification details, or transaction information may remain visible to every recipient unless access permissions and sharing settings are reviewed. A signer may complete the California Disclaimer Form without receiving a clear electronic-record consent disclosure when the transaction is consumer-facing. Sending the form to the wrong email address can expose disclaimer content and weaken evidence linking the signature to the intended person. Reusing an outdated disclaimer template can preserve obsolete language, missing fields, or permissions that no longer match the organization’s approval process.
Best practices for California disclaimer records
A controlled template, complete signer evidence, and documented retention process reduce disputes over what was presented, accepted, and stored.
Verify approved language before every send
Place fields beside each statement
Preserve the signed record and audit trail
Document consent and regulated access controls
Security for California disclaimer records
Transport encryption:
Storage encryption:
Security certification:
Information security:
California privacy:
Electronic signatures:
Platform requirements for California disclaimers
Complete and sign the California Disclaimer Form through Chrome, Firefox, Safari, or Edge on Windows and macOS, or through signNow mobile apps on iOS and Android.
Browser support Chrome, Firefox, Safari, and Edge on Windows or macOS Mobile devices iOS and Android phones support mobile document signing Connection security TLS 1.2 or newer secures browser connections
Organizations using California Disclaimer Forms should manage access on approved Windows, macOS, iOS, or Android devices. Enterprise teams can pair signNow with SSO provisioning, API access, managed-device policies, and audit-trail retention controls when their workflow requires centralized oversight.
Key performance indicators that demonstrate SignNow's proven track record.
California disclaimer form troubleshooting
Resolve field, consent, signing, plan, and retention questions before distributing a California Disclaimer Form through signNow.
Upload the original California Disclaimer Form as a PDF or supported document, then confirm that signNow’s detected fields align with the form’s actual disclaimer language. If detection misses a field, add it manually before sending and verify the signer order.
The signNow Business plan includes legally binding eSignatures, templates, mobile apps, and audit trails at $8/user/month when billed annually. Business Premium adds bulk send at $15/user/month annually; select the plan based on volume and workflow requirements.
For consumer-facing California Disclaimer Forms, obtain electronic-record consent and show that the signer can access the electronic format, as required by 15 U.S.C. §7001(c). Store the consent evidence with the signed form and audit trail.
A California Disclaimer Form may use an electronic signature when the signer intends to sign and the record remains attributable, accessible, and reproducible under ESIGN and applicable California law. This does not override exclusions for wills, court orders, or family-law decrees.
If a signer cannot open the request, confirm the email address, resend the invitation, or provide a signNow signing link. SMS authentication may add an identity check, but the sender should verify the recipient before sharing sensitive disclaimer information.
Use signNow’s audit trail and completed-document history to preserve timestamps, signer actions, and delivery evidence. For regulated records, apply the organization’s retention policy and any governing rule; signNow’s HIPAA compliance requires a BAA when protected health information is involved.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.