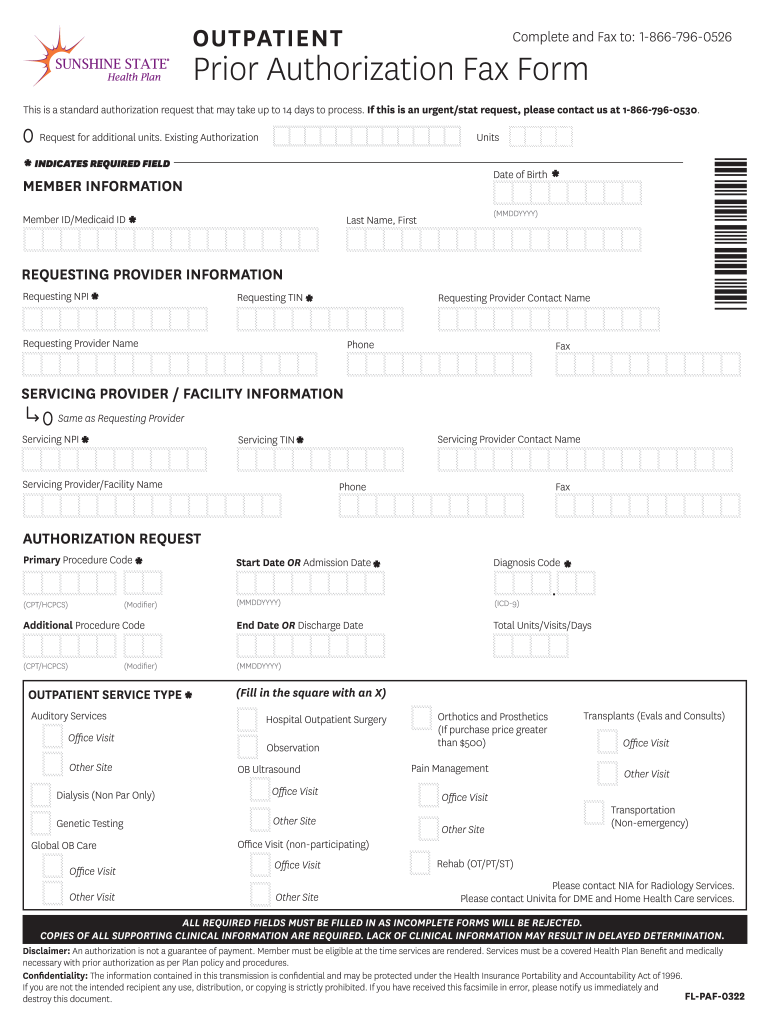
Sunshine State Helath Plan Medicaid Prior Authorization Form
Create a custom Sunshine State Helath Plan Medicaid Prior Authorization Form 0 that meets your industry’s specifications.
What this Medicaid authorization form does
The Sunshine State Helath Plan Medicaid Prior Authorization Form is used to request plan review before a covered Medicaid service, treatment, medication, or supply is provided when prior authorization applies. A provider enters member and clinical details, identifies the requested service, attaches supporting records, and obtains the required attestations or signatures. With signNow, the organization uploads the form, places fields, routes it to designated participants, and stores the completed PDF with an audit trail. Sunshine State Helath Plan—not signNow—decides submission requirements, medical necessity, and approval.
Who uses this Medicaid authorization form
Healthcare providers
Provider offices complete the member, diagnosis, requested service, clinical rationale, and provider-attestation sections before routing the form for required signatures. They should verify Sunshine State Helath Plan’s current submission instructions separately because signNow manages document execution, not payer eligibility or clinical approval.
Authorization participants
Patients, authorized representatives, utilization-review staff, and care coordinators use the workflow to review consent and authorization details. A completed signNow record can preserve signatures and audit evidence, while the payer’s rules determine whether the requested Medicaid service is approved.
Features that support this Medicaid form
The Sunshine State Helath Plan Medicaid Prior Authorization Form combines clinical information, member details, provider attestations, and signatures in one reviewable workflow.
Form preparation
Upload the Sunshine State Helath Plan Medicaid Prior Authorization Form and use signNow field tools to prepare provider, member, consent, and signature fields without recreating the document.
Signer routing
Assign fields to the provider, patient, representative, or other authorized signer so each participant receives only the actions required for this authorization request.
Audit trail
Capture timestamps, signer activity, and document history in an audit trail that supports internal review of how the authorization was completed.
Reusable templates
Use signNow templates for repeated authorization requests while preserving the plan-specific form structure and required supporting documentation.
Mobile signing
Review and sign from desktop or mobile devices, helping providers coordinate signatures when staff and patients are not in the same location.
Secure records
Store the completed PDF and signing evidence with the patient’s authorization record, subject to HIPAA safeguards and applicable retention rules.
How the authorization workflow works
Use this sequence to prepare, route, complete, and retain the Sunshine State Helath Plan Medicaid Prior Authorization Form.
Upload form: Upload the current Sunshine State Helath Plan form. Add fields: Place fields for each required participant. Route request: Send the prepared authorization to signers. Store evidence: Download the signed record and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How signNow records this form’s audit trail
The audit trail documents who interacted with the authorization, when actions occurred, and how the completed record can be retrieved for review.
Authenticate signer:
Capture timestamp:
Record document history:
Preserve evidence:
Export records:
Archive securely:
Recommended setup for this authorization
Configure the workflow around patient privacy, signer identity, audit evidence, and the retention rule applicable to the completed Medicaid authorization record.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for authorized representatives |
| Signature type | Electronic signature with signer intent |
| Audit trail | Enable completion history and export |
| Document retention | Six years under HIPAA 45 CFR 164.530(j) |
| Encryption and provisioning | AES-256 storage with role-based users |
Security controls for Medicaid records
Healthcare privacy:
Stored data:
Transport security:
Security assurance:
Information security:
Electronic signatures:
Platform requirements for completing the form
Use Chrome, Firefox, Safari, or Edge on Windows 10 or later, macOS, iOS, or Android. signNow protects browser traffic with TLS 1.2 or TLS 1.3 and supports mobile access for reviewing and signing this Medicaid authorization document.
Browsers Chrome, Firefox, Safari, and Edge Operating systems Windows 10+, macOS, iOS, Android Secure connection TLS 1.2 or newer connection
Healthcare organizations should use managed devices, current browser security updates, and access controls appropriate for protected health information. API, SSO, certificate, and long-term validation requirements depend on the organization’s signNow plan and should be configured with its compliance team before deployment.



Retention periods for authorization records
Keep the completed authorization, attachments, consent evidence, and audit trail according to the record category that applies. State Medicaid and provider-contract rules may require longer retention than these federal baselines.
Six years: HIPAA records
Three years: tax records
Three years: payroll records
Five years: injury records
Thirty years: exposure records
Risks of incomplete authorization submissions
Review delay
Resubmission
Consent dispute
Appeal evidence
Privacy pitfalls in authorization workflows
Including diagnosis or treatment details in unrestricted email exposes protected health information beyond the authorization team’s approved access scope. Routing the form to an unverified representative can produce disputed consent and require the provider to repeat the authorization workflow. Leaving member identifiers or requested-service fields visible in shared templates increases the risk of attaching clinical data to the wrong patient. Failing to download the completed PDF and audit trail can leave staff unable to reconstruct the signature and consent history during payer review.
Troubleshooting the Medicaid authorization workflow
Most issues arise from incomplete clinical fields, incorrect signer assignment, or storage controls. These checks separate signNow workflow problems from Sunshine State Helath Plan review requirements.
Upload the payer’s current Sunshine State Helath Plan Medicaid Prior Authorization Form as a PDF, then confirm the page order and readable clinical attachments. signNow can place fields after upload, but it does not determine whether the plan accepts a particular service or procedure.
Use signNow’s field placement tools to assign provider, member, date, signature, and consent fields to the correct signer. Review every required field before sending; an electronic signature does not cure missing medical-necessity information or an incorrect member identifier.
For protected health information, confirm that the organization’s signNow account has the required HIPAA configuration and Business Associate Agreement. HIPAA compliance is conditional on the BAA and appropriate organizational safeguards, not merely on using an electronic signature.
The Business plan is $8 per user per month when billed annually and includes templates and audit trails. Business Premium is $15 annually billed and adds bulk send. Plan selection does not change Sunshine State Helath Plan’s clinical authorization rules.
If a patient or representative signs electronically, provide the required consumer electronic-record disclosure and ensure the signer can access the record. ESIGN, 15 U.S.C. §7001(c), requires these safeguards for covered consumer transactions.
After completion, download the signed PDF and certificate or audit trail from signNow, then store them with the authorization record. HIPAA documentation requirements generally require six years from creation or the last effective date under 45 CFR §164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.