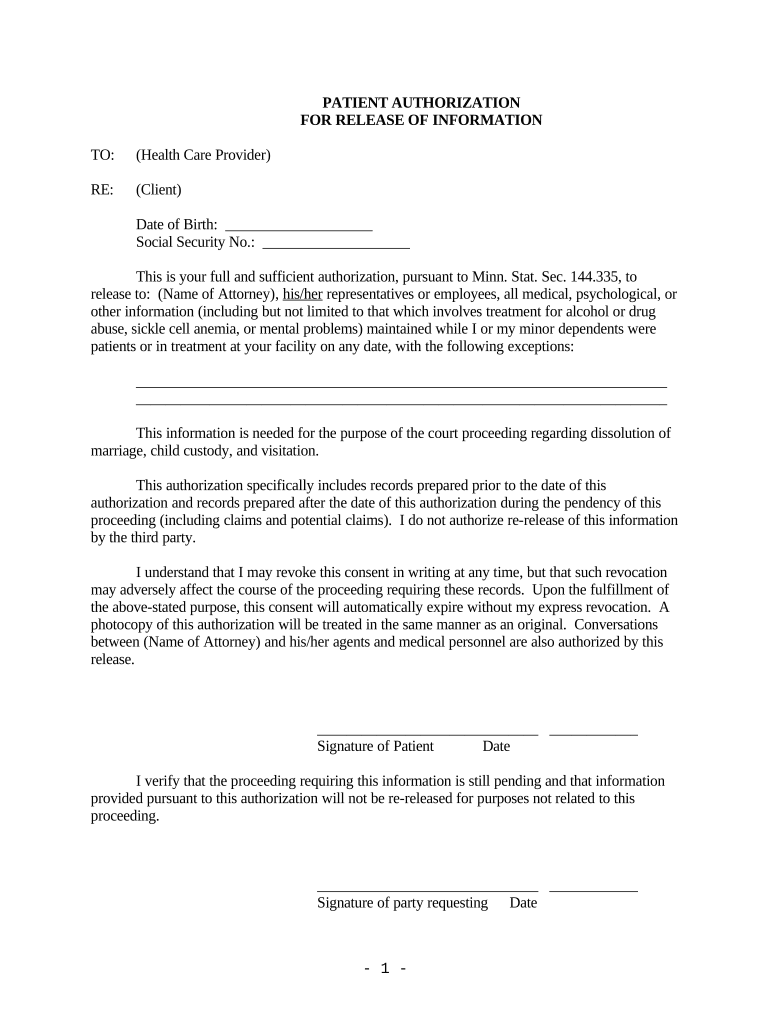
Patient Release Authorization Form
Use a Patient Release Authorization template to make your document workflow more streamlined.
What a patient release authorization does
A Patient Release Authorization Form records a patient’s permission for a healthcare provider or other covered entity to disclose specified protected health information to a named recipient. The form generally identifies the patient, information to be released, recipient, purpose, expiration, and signature. Staff should verify that the authorization is complete before releasing records and retain the signed copy with the disclosure documentation. Under HIPAA, the authorization supports controlled disclosure; it does not replace an organization’s obligation to apply its privacy, security, and minimum-necessary policies.
Business types using patient release forms
Patient release authorizations help healthcare organizations document consent before protected health information is disclosed.
Solo medical practices use the form to obtain patient permission before sharing records with specialists, insurers, attorneys, or family members, while keeping each authorization tied to the correct patient and disclosure purpose. Multi-location clinics use standardized authorization templates to route patient releases between front-desk teams, clinicians, and records departments, reducing duplicate requests and preserving a searchable signing history for every disclosed record. Hospital systems and enterprise healthcare networks use role-based workflows, HIPAA safeguards, and audit trails to manage high-volume patient releases across departments, affiliated providers, and external recipients without relying on paper routing.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the release workflow works
The signNow workflow converts a patient release from an uploaded document into a controlled, signed record with evidence for the disclosure process.
Upload the Patient Release Authorization Form: Upload form Review patient and disclosure fields: Detect fields Route the form to the patient: Send securely Store the signed form and audit trail: Archive evidence
How to complete the authorization
Prepare the patient release form, verify its disclosure details, and use signNow to obtain and retain the required signature.
Upload form:
Upload the blank or completed authorization template to signNow. Add fields:
Review detected fields and add patient, recipient, purpose, and signature fields. Send request:
Enter the authorized recipient’s email address and send the release. Store evidence:
Confirm the signed copy and audit trail are stored with the patient record.
Recommended release workflow setup
Configure the authorization workflow around patient identity, disclosure scope, signer evidence, and HIPAA record-retention obligations.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS code |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion certificate and action log |
| Document retention | Retain six years under HIPAA 45 CFR 164.530(j) |
| Encryption | Use TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Ways to send and sign the release
- Use the web app when records staff need to upload the Patient Release Authorization Form, place fields, review patient details, and send the request from a desktop workflow.
- Use the mobile app when a patient or authorized representative needs to review and sign the release from an iOS or Android device during a clinic visit or remote interaction.
- Use kiosk mode when staff supervise signing on a clinic-owned device and need the patient to complete the release without exchanging a personal email address.
- Use a shareable signing link when a clinic distributes the same authorization workflow through a patient portal, approved message, or controlled intake process.
What the audit trail records
A signNow audit trail documents the technical and administrative events surrounding the patient’s signed authorization.
Authenticate signer:
Capture timestamp:
Protect document:
Log activity:
Seal completion:
Export audit trail:
Security for patient release records
HIPAA compliance:
Transport encryption:
Stored encryption:
Security assurance:
Security certification:
Electronic signing:
Privacy and disclosure pitfalls
A release containing diagnosis, treatment, or insurance information can expose protected health information when sent to an unverified recipient or stored in an uncontrolled mailbox. Patients may sign without understanding the disclosure scope if the purpose, recipient, records, or expiration language is hidden, vague, or incomplete. Shared accounts, broad permissions, or delegated sending can allow unauthorized staff to access patient releases or send them without the organization’s required review. A signed authorization stored without its audit trail may not show when consent occurred or whether the disclosed records matched the patient’s permission.
Best practices for patient releases
Accurate fields, documented consent, controlled access, and evidence retention make a patient release easier to review before records are disclosed.
Apply the HIPAA retention period
Export evidence with every authorization
Check every disclosure field
Confirm the BAA and safeguards
Patient release processing stages
A patient release moves from authorization review through signature, verification, and record retention before disclosure occurs.
Prepare authorization
Deliver to signer
Patient turnaround
Complete and archive
Risks of an incomplete release
Disclosure challenge
Audit weakness
Privacy incident
Unauthorized release
Patient release workflow examples
Healthcare organizations use signed release authorizations to document patient consent before sharing specified records with named recipients.
Healthcare provider
A fertility care provider needs signed permission before sharing treatment records with an outside recipient identified by the patient.
- Named recipient and purpose
- Electronic signature with audit trail
The provider can route the authorization electronically, confirm the patient’s signature, and retain the completed form with disclosure documentation. signNow customer Fertility Centers of Illinois is listed in the product ground truth as an organization using the platform and provides a healthcare-relevant reference point without implying that this exact form was used.
Clinic records team
A regional clinic replaces paper routing when patients authorize release of records to specialists and legal representatives.
- Patient identity fields checked
- Signed copy retained securely
The records team can standardize the request, send it to the patient, and review the completion certificate before releasing records. The workflow creates a clearer evidence trail for authorization status, recipient details, and signing activity.



Key performance indicators that demonstrate SignNow's proven track record.
Patient release troubleshooting
These answers address signing, HIPAA configuration, field review, subscription limits, and evidence retention for Patient Release Authorization Form workflows.
Business includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, SOC 2, and GDPR. For a HIPAA workflow, signNow states that a BAA is required, so confirm the account configuration before processing protected health information.
Yes. signNow provides mobile apps for completing the authorization on a phone or tablet. Review patient identifiers, recipient information, disclosure scope, and expiration before signing, because the platform does not replace the healthcare organization’s authorization review.
The Business plan includes 100 signature invites per user per year, with overage fees. Business Premium includes bulk send, while Enterprise adds advanced signer authentication. Choose the plan based on release volume and required controls rather than assuming unlimited subscription usage.
signNow’s HIPAA compliance status includes a BAA requirement. The healthcare organization remains responsible for its privacy, security, access, minimum-necessary, and retention procedures under HIPAA, including 45 CFR 164.530(j) for six-year documentation retention.
If fields are not detected correctly, upload a clearer PDF or add the patient, recipient, purpose, expiration, and signature fields manually. Review every detected field before sending because auto-detection does not determine whether the authorization satisfies HIPAA requirements.
A completed authorization should be retained with its completion certificate and action history. signNow provides audit trails, while the covered entity must connect the record to its disclosure process and apply the six-year HIPAA documentation period under 45 CFR 164.530(j).
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.