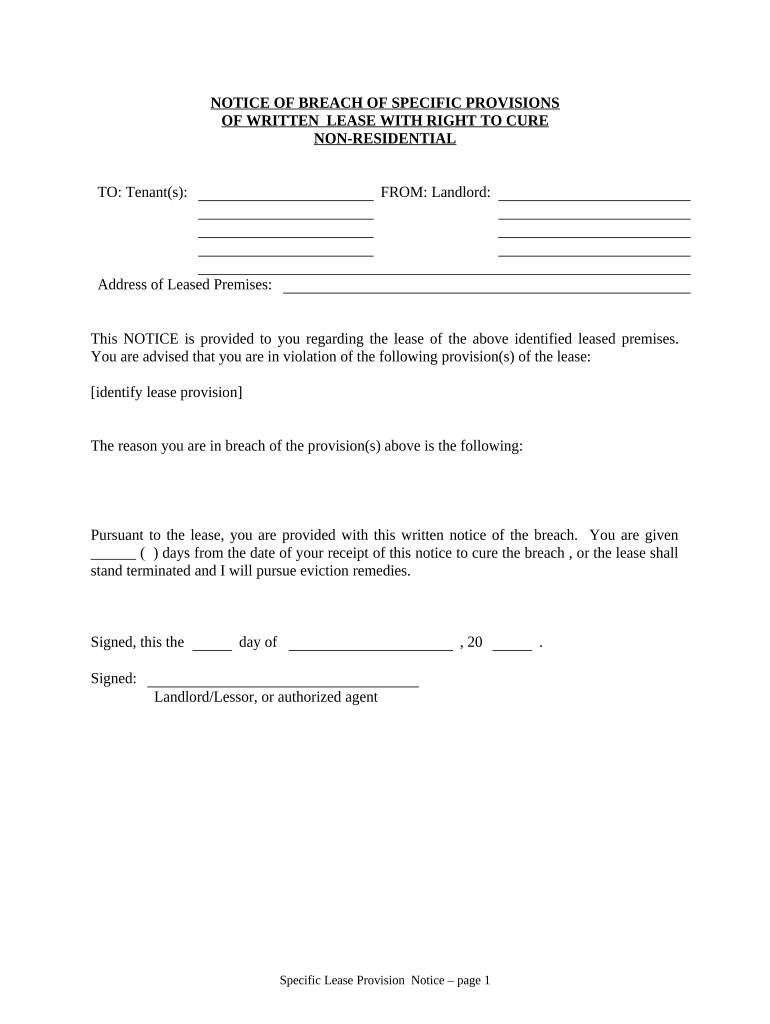
Notice Breach Form
Use a Notice Breach template to make your document workflow more streamlined.
What Notice Breach Form does
Notice Breach Form records a business’s written communication about a security or privacy breach and the recipient’s acknowledgment or signature. The completed document can identify the incident, affected information, notification details, response contacts, and signing evidence. With signNow, upload the form, review automatically detected fillable fields, add missing fields, assign recipients, and send it electronically. Each signer reviews and signs the designated fields, while signNow records delivery, authentication, timestamps, document history, and completion evidence for controlled retention. Legal treatment depends on the notice and applicable federal and state law.
Business types using Notice Breach Form
Notice Breach Form supports organizations that must issue, sign, and preserve documented breach communications.
Solo legal practices can use Notice Breach Form to document incident notifications, collect client acknowledgments, and preserve a signed record without coordinating repeated office visits. Healthcare clinics can send Notice Breach Form to affected patients, capture electronic acknowledgments, and retain a clear signing history for privacy-response documentation under HIPAA workflows. Enterprise compliance departments can standardize Notice Breach Form across regional teams, route approvals by role, and monitor completed notices through shared templates and audit trails.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Recommended Notice Breach Form setup
Configure the Notice Breach Form workflow around signer identity, evidence preservation, access control, and the retention rule governing the underlying records.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture delivery, identity, and timestamps |
| Document retention | Six years for HIPAA records |
| Encryption and provisioning | AES-256 storage with administrator-controlled access |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the Notice Breach Form audit trail works
The audit trail records technical evidence around each Notice Breach Form signing event, from signer authentication through final export.
Authenticate signer:
Capture timestamps:
Hash document:
Seal document:
Log activity:
Export evidence:
Retention practices for breach notices
Preserve the signed Notice Breach Form, audit evidence, and retention rationale together so the record remains usable throughout its required lifecycle.
Apply the governing retention period
Export the audit trail promptly
Archive final records securely
Document the retention trigger
Retention periods for signed notices
Choose the retention period by identifying the underlying records and the authority governing them, rather than applying one period to every Notice Breach Form.
Six years from creation or last effective date
Three years from filing
Six years after substantial understatement
Not applicable to breach notices
Verify state-specific retention
Privacy challenges with breach notices
Including unnecessary names, account numbers, or medical details can expose personal information beyond what the Notice Breach Form recipient needs. Sending a breach notice before confirming the recipient address can disclose incident details to an unintended person or organization. Failing to capture electronic consent can weaken the record when a consumer later disputes receiving or signing the Notice Breach Form. Leaving completed notices accessible to broad teams can create unauthorized disclosure, alteration, or deletion risks after the response is closed.
Check exclusions and state rules
State notarization
Wills and codicils
Court documents
Real-estate deeds
Notice Breach Form troubleshooting
Resolve field, authentication, privacy, and enforceability questions before distributing a completed Notice Breach Form.
Upload the original Notice Breach Form as a clear PDF, then review signNow’s detected fields before sending. If fields are missing, add signature, date, text, or initials fields manually and confirm every required recipient is assigned.
The Business plan includes templates, audit trails, and legally binding eSignatures. Business Premium adds bulk send, while Enterprise adds advanced signer authentication. Select the plan based on the number of recipients and authentication controls required for your notice process.
HIPAA workflows require a business associate agreement with signNow. Confirm that the Notice Breach Form contains protected health information, use the required agreement, restrict access, and apply your organization’s HIPAA policies rather than relying on the signature alone.
For consumer-facing electronic records, ESIGN requires disclosure of the right to paper, access to the electronic format, and a method to withdraw consent under 15 U.S.C. §7001(c). Configure and retain those disclosures with the Notice Breach Form workflow.
If a signer cannot open the Notice Breach Form, verify the recipient address, resend the invitation, or provide an authorized signing link. The completed record should remain in signNow with its audit trail after the signer finishes.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are established. They do not cover wills, certain court filings, or other statutory exclusions, so review the notice’s legal context before sending.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.