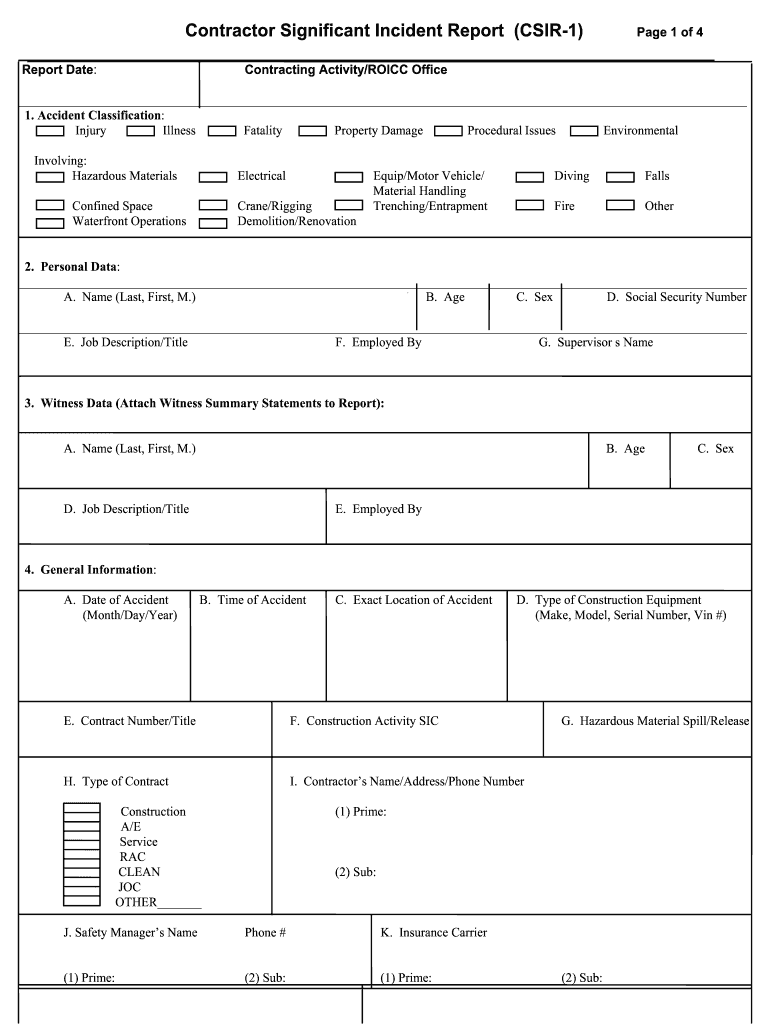
Contractor Significant Incident Report Csir 1 Form
Create a custom Contractor Significant Incident Report CSIR 1 0 that meets your industry’s specifications.
What this contractor incident report records
The Contractor Significant Incident Report Csir 1 Form is a written record of a significant event involving a contractor and the work, site, equipment, or people affected. It gives the responsible organization a structured place to describe what happened, identify participants, document immediate actions, and obtain acknowledgments. Because the form name does not identify a federal agency, nationally prescribed fields, or a universal filing deadline, the contracting organization must follow its own safety policy, contract terms, and applicable state or industry rules. signNow can preserve the completed report, signer actions, timestamps, and audit trail.
Business types using this report
The report is useful wherever contractors work under documented safety, compliance, or project-management procedures and must acknowledge a significant incident.
A small construction contractor can use the report after a site incident to capture the event, supervisor review, corrective actions, and worker acknowledgment without transporting paper between locations. A regional facilities operator can route incident reports from multiple project sites to safety managers, preserving consistent fields, signer identity, completion timestamps, and audit trails for internal review. An enterprise procurement or compliance team can standardize contractor incident reporting across business units, applying role-based access, reusable templates, and controlled retention for sensitive project records.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Complete the incident report online
Use this sequence to prepare the Contractor Significant Incident Report Csir 1 Form, collect required acknowledgments, and retain a verifiable completion record.
Upload report:
Upload the blank or partially completed report to signNow. Check fields:
Review detected fields and add missing text, date, and signature fields. Assign signers:
Assign each field to the responsible contractor or reviewer. Send report:
Send the report by email or signing link. Archive records:
Review the signed PDF and download its audit trail.
How the report workflow works
The signNow workflow keeps report preparation, signing, and evidence preservation in a defined sequence.
Upload report: Upload the Contractor Significant Incident Report Csir 1 Form. Prepare fields: Add incident details and assign responsible signers. Collect signatures: Collect signatures and acknowledgments through signNow. Preserve record: Store the completed report with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features that support incident reporting
signNow connects the report’s preparation, signature collection, evidence preservation, and controlled distribution in one documented workflow.
Document upload
Upload a blank or partially completed Contractor Significant Incident Report Csir 1 Form and keep the original layout while preparing fields for the responsible parties.
Field preparation
Review automatically detected fillable areas, then add incident-specific fields for descriptions, dates, witness information, corrective actions, and acknowledgments.
Signer assignment
Assign every signature, initials, date, and acknowledgment field to a named contractor, supervisor, or reviewer before sending the report.
Flexible signing
Collect signatures through email invitations, mobile signing, kiosk mode, or a shareable link suited to the project’s operating conditions.
Audit trail
Preserve timestamps, signer actions, and the completed PDF together so reviewers can reconstruct how the incident report was executed.
Controlled access
Use encryption and access controls to limit exposure of contractor, project, location, and incident information during transmission and storage.
Security controls for incident reports
Data encryption:
Transport security:
Security certification:
Security management:
Signature compliance:
Health data protection:
Choose a signing method for incident reports
- Use the signNow web app when a coordinator needs to upload the Contractor Significant Incident Report Csir 1 Form, assign fields, and monitor completion from a desktop workflow.
- Use the signNow mobile app when a supervisor or contractor must review and sign the incident report at a project site using a supported phone or tablet.
- Use kiosk mode when multiple contractors sign on a managed device at a controlled site, with each person completing the assigned incident acknowledgment before the next signer begins.
- Use a shareable signing link when the same report template must be distributed to identified contractors without creating a separate email invitation for every signing event.
Review the report audit trail
The audit trail shows how the Contractor Significant Incident Report Csir 1 Form moved from invitation through signing, review, completion, and archival.
Authenticate signer:
Capture timestamp:
Protect document:
Check activity:
Export evidence:
Limit access:
Retention periods for incident records
Retention depends on the report’s contents and governing policy. Apply the specific rule that covers the underlying incident record, not the form name alone.
Organization policy period
Six years for PHI
Five years for injuries
Thirty years for exposure
Longer state requirements
Record-keeping practices for incident reports
Good record keeping connects the signed Contractor Significant Incident Report Csir 1 Form to its audit trail, governing retention rule, and authorized review process.
Export the report and audit trail
Match retention to governing rules
Review the template before reuse
Limit disclosure during delivery
Privacy and disclosure pitfalls
Uploading a report with exposed personal or medical details can disclose sensitive information to every recipient listed in the signing workflow. Missing acknowledgment fields may leave contractor statements, supervisor review, or corrective-action confirmation undocumented in the final incident record. Sending the report to broad distribution lists can give unauthorized personnel access to names, locations, photographs, or injury-related information. Using an outdated template can omit project identifiers, incident timing, witness details, or required escalation instructions from the signed report.
Troubleshooting the contractor incident report
These answers address field detection, signer access, plan limits, health information, electronic-signature law, and preservation of the completed report.
Upload the Contractor Significant Incident Report Csir 1 Form again as a readable PDF, then review automatically detected fields before sending. Business includes templates and audit trails, while manual field placement remains available when detection misses a field.
Check the recipient email address, invitation status, and signing order in signNow. A signer can use the email invitation or a generated link without a paid account, provided the sender’s workflow permits that access.
Business is listed at $8/user/month with annual billing and includes 100 signature invites per user each year. If the workflow exceeds that allowance, review overage terms or consider Business Premium, Enterprise, or Site License pricing.
For reports containing protected health information, signNow identifies HIPAA compliance as requiring a BAA. Confirm the organization has the required agreement and configure recipients and access accordingly before sending.
ESIGN and UETA generally support electronic signatures when intent, consent, attribution, and record retention are established. The contracting organization must still check state requirements and internal incident-reporting policy.
Export the completed PDF and its audit trail from signNow after all assigned fields are finished. Retain them under the organization’s incident-record policy; no universal federal retention period is established by this form name.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.