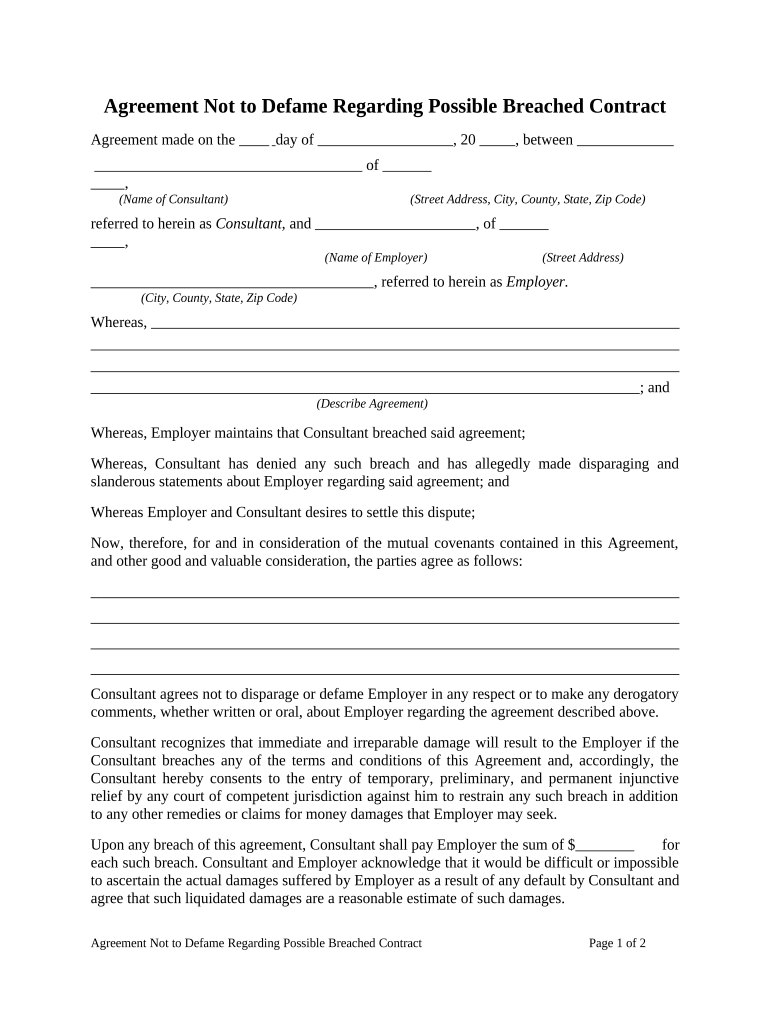
Defame Form
Use a Defame template to make your document workflow more streamlined.
Defame Form overview
Defame Form is a document used to collect information, acknowledgments, and signatures for a specific business or legal transaction. Because the available form name does not identify an issuing agency, statutory fields, filing deadline, or mandatory signer role, those details should be confirmed from the form source before completion. In signNow, a user uploads the PDF, reviews automatically detected fields, adds any missing fields, assigns signers, and sends the document. Each signer reviews and signs electronically; signNow then preserves the completed document and audit trail for authorized users.
How Defame Form works
Complete the Defame Form in signNow by preparing its fields, assigning signers, collecting signatures, and preserving the final record.
Upload form: Upload the Defame Form PDF to signNow. Check fields: Review detected fields and add missing signer fields. Send form: Assign signers and send the Defame Form. Store record: Collect signatures and store the completed record.
Steps to complete Defame Form
Use this sequence to move the Defame Form from an uploaded file to a completed, traceable electronic record.
Upload form:
Upload the Defame Form PDF. Review fields:
Check detected fields and add missing fields. Assign signers:
Enter signer details and send the form. Save records:
Download the completed form with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended Defame Form setup
Configure the Defame Form workflow around signer identity, signature evidence, controlled access, and a documented retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP address, and actions |
| Document retention | Follow the applicable business record policy |
| Encryption and provisioning | AES-256 protection with role-based access |
How the Defame Form audit trail works
The audit trail connects signer identity, document activity, timestamps, and completion evidence for the specific Defame Form transaction.
Authenticate signer:
Capture timestamps:
Protect document:
Link actions:
Review audit trail:
Export evidence:
Defame Form security controls
Transport encryption:
Stored encryption:
Security certification:
Management standard:
Signature compliance:
Healthcare protection:
Defame Form processing timeline
The processing sequence moves from field completion through signer review, completion, and organized electronic recordkeeping.
Prepare the form
Send to signers
Review and sign
Complete and archive
Defame Form platform requirements
The Defame Form workflow runs in current Chrome, Firefox, Safari, or Edge browsers on Windows and macOS. signNow mobile apps support iOS and Android access, while encrypted connections protect data during online completion and signing.
Browser support Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile systems iOS and Android mobile access
Organizations should use managed Windows, macOS, iOS, or Android devices when the Defame Form contains personal or confidential information. Administrators can also evaluate API access, SSO provisioning, mobile permissions, and retention controls before deploying the workflow across departments or external signers.
Defame Form completion risks
Enforceability dispute
Processing delay
Privacy exposure
Evidence weakness
Defame Form troubleshooting
Resolve Defame Form issues by checking field placement, signer access, electronic-signature evidence, plan limits, and applicable privacy obligations.
Upload the original PDF again and confirm that the file opens correctly before placing signNow fields. If automatic field detection does not identify a field, add the appropriate text, date, checkbox, or signature field manually, then preview the document before sending.
Check the recipient’s email address, resend the invitation, or provide a shareable signing link. If stronger attribution is required, configure SMS OTP or another available authentication method before sending the Defame Form again.
A typed or drawn signature can qualify as an electronic signature when intent, consent, attribution, and record retention are established. ESIGN and applicable UETA provisions support electronic records, subject to statutory exclusions and transaction-specific requirements.
Consumer-facing transactions may require an ESIGN disclosure explaining paper-record rights, electronic access, and consent withdrawal procedures under 15 U.S.C. §7001(c). Obtain appropriate legal review when the Defame Form is used with consumers.
Business includes legally binding eSignatures, audit trails, templates, and mobile apps at $8/user/month with annual billing. It includes 100 signature invites per user annually, with overage fees; confirm current plan terms before deployment.
If the Defame Form contains protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Do not place PHI in the workflow until the required agreement and organizational safeguards are in place.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.