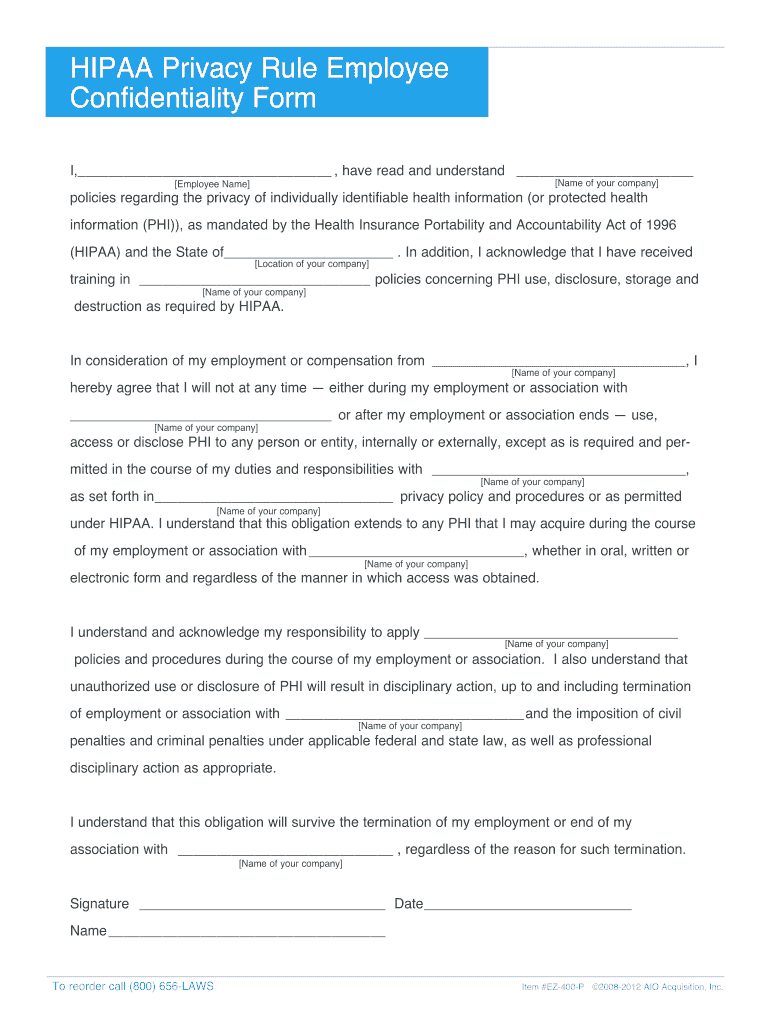
How To Creat A HIPAA Form
Use a How To Creat A Hipaa Form template to make your document workflow more streamlined.
What a HIPAA form does
A HIPAA form documents a person’s authorization, acknowledgment, or permission concerning protected health information. It identifies the patient, the information or disclosure purpose, the recipient, the signer, and any effective or expiration terms required by the organization’s approved language. In signNow, the sender uploads the form, places fillable and signature fields, routes it to the authorized signer, and stores the completed document with an audit trail. HIPAA documentation generally requires six-year retention under 45 CFR §164.530(j), while the form’s exact legal use depends on its wording and disclosure context.
How HIPAA forms support compliant transactions
A HIPAA form records authorization or acknowledgment involving protected health information. Under ESIGN and UETA, an electronic record and signature may be admissible when intent, consent, attribution, and reliable retention are shown. Wills, testamentary trusts, certain court orders, and specified family-law filings remain excluded.

Who uses HIPAA forms and why
Healthcare providers
Healthcare providers and clinics use HIPAA forms to document patient authorization for specified uses or disclosures of protected health information. Staff can prepare reusable templates, collect signatures, preserve audit evidence, and restrict access to authorized personnel.
Health operations
Medical billing, insurance, and health-services operations teams use signed HIPAA forms when a documented authorization or acknowledgment must move between patients, staff, and business associates. signNow supports controlled routing, mobile signing, and retained completion records.
Quick steps to create a HIPAA form
Prepare the approved HIPAA authorization, complete its fields, and preserve the signed record with its audit evidence.
Upload form:
Upload the approved HIPAA form PDF. Add fields:
Add patient, purpose, and signer fields. Send form:
Send to the authorized signer. Review record:
Review the completed audit trail. Store safely:
Store the signed form securely.
How the HIPAA form workflow works
A HIPAA form moves from structured field preparation to controlled signing, then becomes a retained record with evidence of the signing event.
Upload form: Upload the HIPAA authorization PDF and identify its patient, recipient, purpose, and expiration fields. Map fields: Place required signer, date, consent, and acknowledgment fields using signNow’s editor. Send securely: Send the prepared form to the authorized signer through email or a signing link. Store evidence: Collect the signature and retain the completed form with its signNow audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Ways to send and sign HIPAA forms
- Use the signNow web app to upload the HIPAA form, place authorization fields, route it to the designated signer, and retain the completed record with its audit trail.
- Use the signNow mobile app when authorized healthcare staff need to review or sign a HIPAA form from an iOS or Android device while maintaining the same signing record.
- Use kiosk mode for supervised patient completion at a clinic desk, keeping the form available on a controlled device and directing each patient through the required consent fields.
- Generate a shareable signing link when a verified recipient needs access without a separate email invitation; restrict distribution and avoid exposing PHI through an uncontrolled channel.
Recommended HIPAA form workflow setup
Configure signing, access, evidence, and retention controls before handling protected health information in a HIPAA form workflow.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS authentication |
| Signature type | Intent-based electronic signature |
| Audit trail | Export with completed authorization |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| User provisioning | Role-based access for authorized staff |
Security controls for HIPAA forms
HIPAA protection:
Stored encryption:
Transit encryption:
SOC 2 assurance:
ISO 27001 controls:
Privacy framework:
Platform requirements for HIPAA forms
Use signNow through Chrome, Firefox, Safari, or Edge on Windows or macOS. The signNow mobile apps support iOS and Android, allowing authorized users to review and sign HIPAA forms on supported mobile devices. Protect access with managed devices and current operating-system security updates.
Browser support Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile access iOS and Android mobile apps
Healthcare organizations should manage devices, user provisioning, and access permissions before processing PHI. Enterprise deployments may require API access, SSO provisioning, and a documented certificate or long-term validation policy. Confirm the required HIPAA BAA, retention controls, and organizational security procedures before production use.
Privacy challenges in HIPAA forms
Including diagnoses or treatment details beyond the authorization purpose can expose unnecessary PHI and expand the disclosure risk. Failing to capture the patient’s informed consent can weaken evidence that the signer understood and intended the authorization. Sending a signing link through an uncontrolled channel can expose patient information to an unintended recipient. Allowing broad staff access can make it difficult to demonstrate that only authorized personnel handled the completed HIPAA form.
Best practices for HIPAA form records
Use precise authorization language, controlled access, and documented retention practices when creating and storing a signed HIPAA form.
Retain authorization records six years
Export the audit trail
Minimize disclosed information
Control reusable templates
Rollout and retention for HIPAA forms
Use a controlled rollout for protected health information, then preserve completed authorizations and audit evidence for the required period.
Account setup:
Template preparation:
First send:
Team onboarding:
Seven-day trial:
Signed record:
Six-year minimum:
Policy review:
How the signNow audit trail works
A signNow audit trail connects the HIPAA form, signer activity, timestamps, and completion evidence without replacing the organization’s HIPAA records policy.
Authenticate signer:
Capture timestamp:
Track document:
Seal evidence:
Log activity:
Export records:



Troubleshooting HIPAA form workflows
Resolve signer, privacy, plan, and retention issues before sending a HIPAA authorization through signNow.
The signNow Business plan supports legally binding eSignatures, templates, mobile apps, audit trails, ISO 27001, SOC 2, and GDPR controls. For a HIPAA workflow, confirm that a business associate agreement is in place because signNow lists HIPAA compliance as requiring a BAA.
Business Premium adds bulk send and kiosk mode, which can distribute the same HIPAA authorization to multiple recipients or support supervised signing. The plan costs $15 per user per month when billed annually; verify the BAA and account configuration before sending PHI.
A missing signer email does not establish attribution. Add the intended signer, require the signer to review the authorization, and use signNow authentication such as SMS verification when appropriate. ESIGN requires intent, consent, attribution, and record retention for electronic validity.
HIPAA protects PHI, but a signature platform alone does not determine whether disclosure is authorized. Limit the form to necessary information, capture the patient’s authorization, and use signNow only with the required BAA and controlled access.
SignNow audit trails record signing activity, including timestamps and action history. Export the completed HIPAA form and its audit trail together, then retain them according to your records policy and HIPAA’s six-year documentation rule in 45 CFR §164.530(j).
The seven-day signNow free trial does not establish HIPAA compliance by itself. Before processing PHI, select an appropriate paid arrangement, execute the required BAA, configure access controls, and confirm that the workflow meets your organization’s security policy.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.