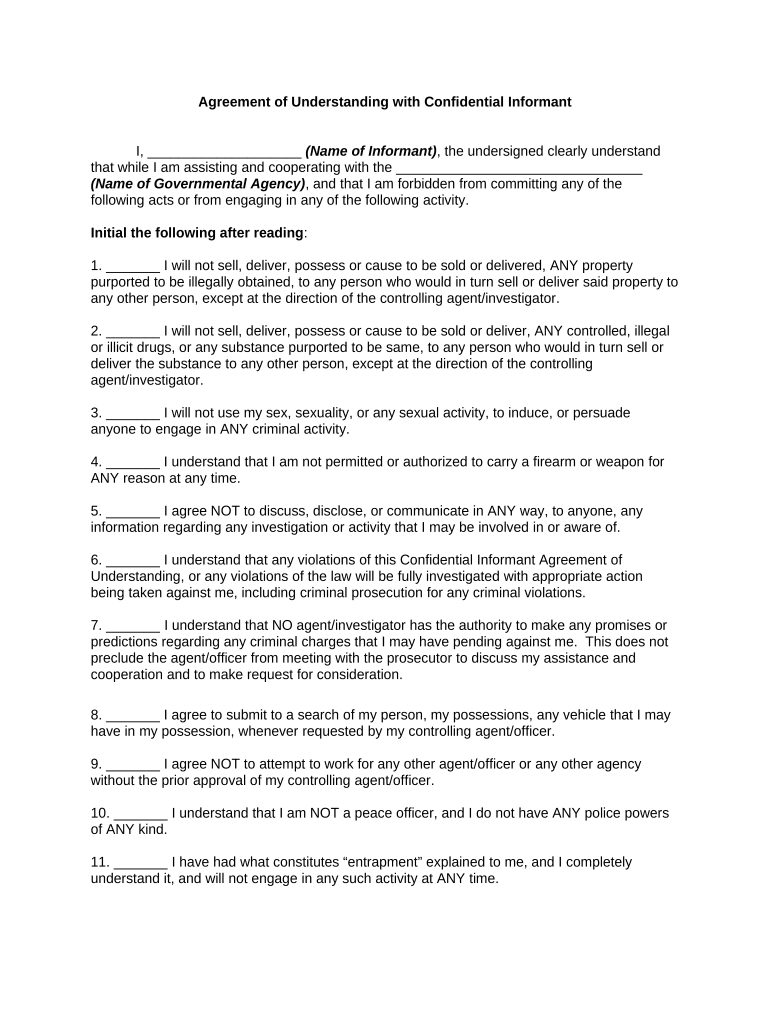
Agreement Of Understanding With Confidential Informant
Use a Agreement Of Understanding With Confidential Informant template to make your document workflow more streamlined.
What this confidential-informant agreement does
An Agreement Of Understanding With Confidential Informant records the relationship between an authorized agency or representative and an informant. It identifies duties, confidentiality expectations, permitted communications, compensation or consideration, acknowledgment of risks, and signature commitments. The parties review the terms, confirm intent to sign electronically, complete assigned fields, and retain the executed record with its audit trail. ESIGN and applicable UETA or New York ESRA rules can support electronic execution, while agency policy and state law determine additional approval, disclosure, notarization, or retention requirements.
Organizations that use this agreement
The agreement fits legal and investigative workflows where authorized parties must document confidential obligations, signatures, and controlled access.
Solo criminal-defense practitioners use the agreement to organize client-authorized informant matters, capture signatures, and preserve a clear record without exchanging uncontrolled attachments. County investigative units use assigned templates to document informant obligations, route approvals, and restrict sensitive records while preserving an audit trail for internal review. Large public-safety agencies use role-based access, delegated sending, and integrations to coordinate high-volume agreements without exposing confidential-informant data across unrelated teams.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses this confidential-informant agreement
Investigative agencies
Law-enforcement agencies and authorized investigative units use this agreement to document an informant’s obligations, confidentiality terms, compensation conditions, and permitted communications. Access should be limited to personnel with a documented need, and the executed record should follow agency retention and disclosure rules.
Legal and compliance
Government contractors, compliance teams, and attorneys may review the agreement when coordinating authorized services or litigation support. They should confirm signatory authority, protect identifying information, and avoid placing operational details in fields visible to unintended recipients.
How the agreement workflow works
The workflow keeps the agreement’s sensitive terms connected to the correct signers and its completion evidence.
Upload and inspect: Upload the agreement and inspect every detected field. Assign responsibilities: Assign each signature and acknowledgment to an authorized person. Route securely: Send the controlled packet through signNow. Preserve evidence: Store the signed PDF and audit trail.
How to prepare and send the agreement
Follow these steps to turn the confidential-informant agreement into a controlled, auditable signing packet.
Upload document:
Upload the completed Agreement Of Understanding With Confidential Informant to signNow. Place fields:
Review detected fields and add signature, date, initials, and acknowledgment fields. Assign signers:
Assign every field to the correct authorized signer. Send and store:
Send the agreement, monitor completion, and preserve the signed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail documents execution evidence for the confidential-informant agreement rather than merely recording account or template setup.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Retrieve evidence:
Archive securely:
Process the agreement from draft to archive
Use a controlled sequence to prepare, route, sign, and preserve this confidential-informant agreement.
Prepare the agreement
Deliver to signers
Complete signatures
Archive the record
Legal standing of the signed agreement
A signed confidential-informant agreement can support evidence of intent, attribution, consent, and the agreed obligations when the record is retained and reproducible under ESIGN, 15 U.S.C. ch. 96, and applicable UETA or New York ESRA rules. Electronic execution does not replace requirements for wills, codicils, testamentary trusts, court orders, official court filings, or family-law decrees.

Risks of incomplete execution or control failures
Signer identity
Electronic consent
Document integrity
Agency authorization
Confidentiality breach
Recommended signing workflow controls
Use documented controls for identity, execution, evidence, retention, encryption, and authorized access to the confidential-informant agreement.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for authorized signers |
| Signature type | Intent-based electronic signature |
| Audit trail | Enable timestamped action history |
| Document retention | Follow agency records schedule |
| Encryption | TLS 1.2 or TLS 1.3 in transit |
Privacy and disclosure pitfalls to prevent
Including an informant’s full identifying information in visible fields can expose sensitive personal data to unauthorized recipients. Sending the agreement before confirming electronic consent can weaken evidence that the signer agreed to digital execution. Assigning operational details to shared templates can reveal confidential information to users without a documented need to know. Using personal email accounts can complicate identity verification, access revocation, and later retrieval of the executed record.
Platform requirements for signing securely
Prepare and sign the Agreement Of Understanding With Confidential Informant in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android, with encrypted connections using TLS 1.2 or TLS 1.3.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile systems iOS and Android mobile apps
Agencies should use managed Windows, macOS, iOS, or Android devices when the agreement contains identifying or operational information. Confirm access controls, SSO provisioning, API requirements, and any certificate or long-term-validation configuration with the organization’s security and records teams before deployment.
Best practices for completing the agreement
Careful drafting, limited disclosure, verified signer identity, and controlled preservation make this sensitive agreement easier to review later.
Define the informant’s obligations precisely
Minimize exposed confidential information
Document intent and signer identity
Preserve the executed record



Questions about completing this agreement
These answers address execution, identity, privacy, and signNow workflow issues specific to a confidential-informant agreement.
Upload the agreement again as a readable PDF, then review signNow’s detected fields manually. Confirm that every signature, date, initials, and acknowledgment field is assigned to the intended authorized signer before sending.
A Business plan includes legally binding eSignatures, templates, and audit trails. If the agency requires bulk send, kiosk mode, or advanced signer authentication, review Business Premium or Enterprise plan requirements before configuring this agreement.
signNow supports ESIGN and UETA workflows, but the agreement must still show intent, consent, attribution, and retained reproducible records. Confirm any state-specific agency rule or required notarization separately before relying on electronic execution.
Use role-based access and limit recipients to authorized personnel. If an email address is wrong, stop the transaction, revoke or correct access where available, and issue a new controlled request rather than forwarding confidential details.
Enable SMS OTP or another available authentication control when the informant’s identity requires more than email-link access. Record the chosen control in agency procedures and verify that the recipient can receive the code securely.
Download the completed agreement and its audit trail after signing, then store both under the agency’s approved records schedule. The audit trail provides timestamps and action history, but it does not replace legal review or classification controls.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.