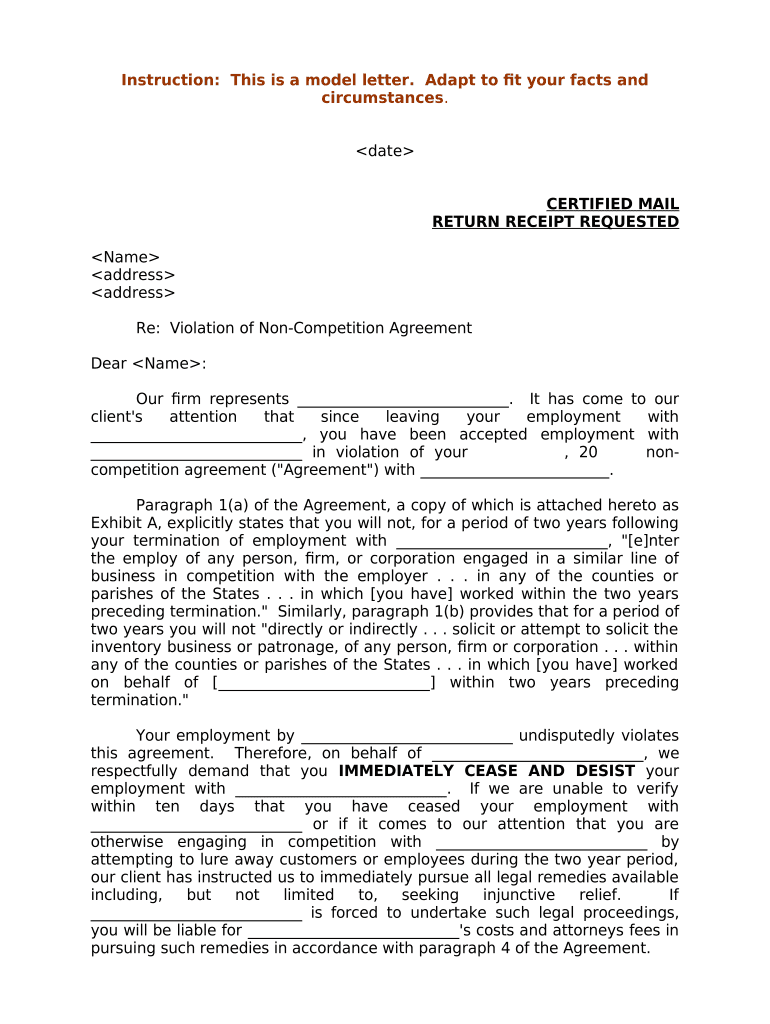
Violation Letter Form
Use a Sample Violation Letter template to make your document workflow more streamlined.
What Violation Letter Form records
Violation Letter Form is a structured document for recording an alleged violation, identifying the relevant parties, stating the supporting facts, and documenting the requested response or corrective action. It can organize the issue, notice date, recipient information, description of conduct, attachments, acknowledgment, and signatures in one record. Because the form’s legal effect depends on the underlying transaction and applicable state or federal law, it should not be treated as a universal government filing. Electronic execution may be recognized under the ESIGN Act and UETA when intent, consent, attribution, and record retention requirements are satisfied.
Who benefits from Violation Letter Form
Violation Letter Form helps organizations document alleged violations consistently while preserving signer identity, timing, and response records.
Solo compliance consultants use Violation Letter Form to document alleged breaches, organize facts, and obtain a dated acknowledgment without building a custom workflow for each matter. Small business legal teams use Violation Letter Form to send a consistent notice, collect the recipient’s response, and preserve signed records alongside supporting correspondence. Enterprise compliance departments use Violation Letter Form to standardize violation notices across business units, control access through administrator settings, and retain an auditable signing record.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How Violation Letter Form works
Use this sequence to prepare, route, complete, and preserve a Violation Letter Form through signNow.
Upload form: Upload the current Violation Letter Form into signNow. Prepare fields: Review detected fields and add missing inputs. Route notice: Send the notice to the designated recipient. Store evidence: Collect signatures and preserve the completed record.
How the Violation Letter audit trail works
The signNow audit trail records the technical events that connect each signer and action to the completed Violation Letter Form.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper sealing:
Event logging:
Audit export:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended Violation Letter Form setup
Configure the form around signer attribution, document integrity, controlled access, and retention requirements applicable to the underlying violation.
| Setting | Recommendation |
|---|---|
| Authentication method | Email authentication with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Retain the completed event history |
| Document retention | Follow the applicable records policy |
| Encryption | TLS in transit and AES-256 at rest |
Privacy pitfalls when sending violation letters
Including unnecessary personal information in Violation Letter Form can expose private details to recipients, administrators, or downstream storage systems. Failing to capture the recipient’s informed consent for electronic records can weaken evidence that the signed Violation Letter Form was properly executed. Assigning broad workspace access may let unauthorized users view allegations, attachments, signer details, or completed Violation Letter Form records. Sending an outdated version can create conflicting violation descriptions, response obligations, or signature records that are difficult to reconcile later.
Risks of incomplete violation letters
Weak evidence
Dispute risk
Proof gap
Privacy exposure
Legal standing and document limits
A completed Violation Letter Form may provide business evidence when the signer demonstrates intent, consents to electronic records, can be attributed to the signature, and the record can be retained and reproduced under the ESIGN Act and applicable UETA or New York ESRA rules. Electronic execution does not replace requirements for wills, codicils, testamentary trusts, court orders, official court filings, or family-law decrees, which are excluded under ESIGN.

Features for completing violation letters
signNow combines field preparation, signer routing, electronic signatures, and audit evidence for organizations documenting Violation Letter Form workflows.
Structured notice
Capture the allegation, affected parties, dates, supporting facts, and requested response in one structured document instead of scattered email messages.
Fillable fields
Use detected or manually placed fields for the notice, acknowledgment, signature, initials, and date sections required by your workflow.
Remote signing
Route Violation Letter Form to the intended recipient by email or signing link and monitor completion without relying on paper delivery.
Audit trail
Preserve signer actions, timestamps, and document history in an audit trail that supports later review of the completed notice.
Access control
Apply role-based access and controlled templates so approved teams send consistent violation notices without exposing unrelated records.
Record continuity
Keep the signed form and completion evidence together so reviewers can evaluate the notice, response, and execution history as one record.
Platform requirements for Violation Letter Form
Complete Violation Letter Form through supported desktop browsers such as Chrome and Edge on Windows or macOS, or through signNow mobile apps on iOS and Android. Use an encrypted connection and a current operating system.
Desktop browsers Chrome and Edge Desktop systems Windows and macOS Mobile apps iOS and Android
Organizations handling sensitive violation records should manage devices, identity access, and storage permissions centrally. Teams requiring automated routing can evaluate signNow API access, SSO provisioning, and integrations with systems such as Microsoft 365, Google Workspace, Salesforce, or NetSuite.
Security for Violation Letter Form
Data in transit:
Data at rest:
Security report:
Security certification:
Health data:
Electronic signatures:
Violation Letter Form troubleshooting
Resolve field, signing, consent, security, plan, and legal-validity questions before distributing a completed Violation Letter Form.
Upload the current Violation Letter Form as a supported document, then use signNow’s field-detection tools to review every notice, response, date, and signature field before sending. The Business plan includes templates and audit trails, but the sender remains responsible for verifying field placement and content.
A recipient can often sign without creating an account, depending on the sender’s configuration. For stronger attribution, configure signNow authentication such as SMS verification or another available method, and preserve the resulting audit trail with the completed Violation Letter Form.
For consumer-facing electronic records, ESIGN requires disclosure of the right to receive paper, access to the electronic format, and a process for withdrawing consent under 15 U.S.C. §7001(c). Configure the workflow accordingly before sending Violation Letter Form.
The Business plan is listed at $8 per user per month with annual billing and includes audit trails and templates. Paid plans include 100 signature invites per user per year; confirm current overage terms before sending high volumes.
signNow lists HIPAA compliance with a business associate agreement when protected health information is involved. Do not place health information in Violation Letter Form unless the organization has the required agreement and safeguards.
Electronic signatures may satisfy ESIGN and UETA requirements when intent, consent, attribution, and record retention are established. Those laws do not decide whether a particular violation notice is legally required, sufficient, or subject to state-specific procedures.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.