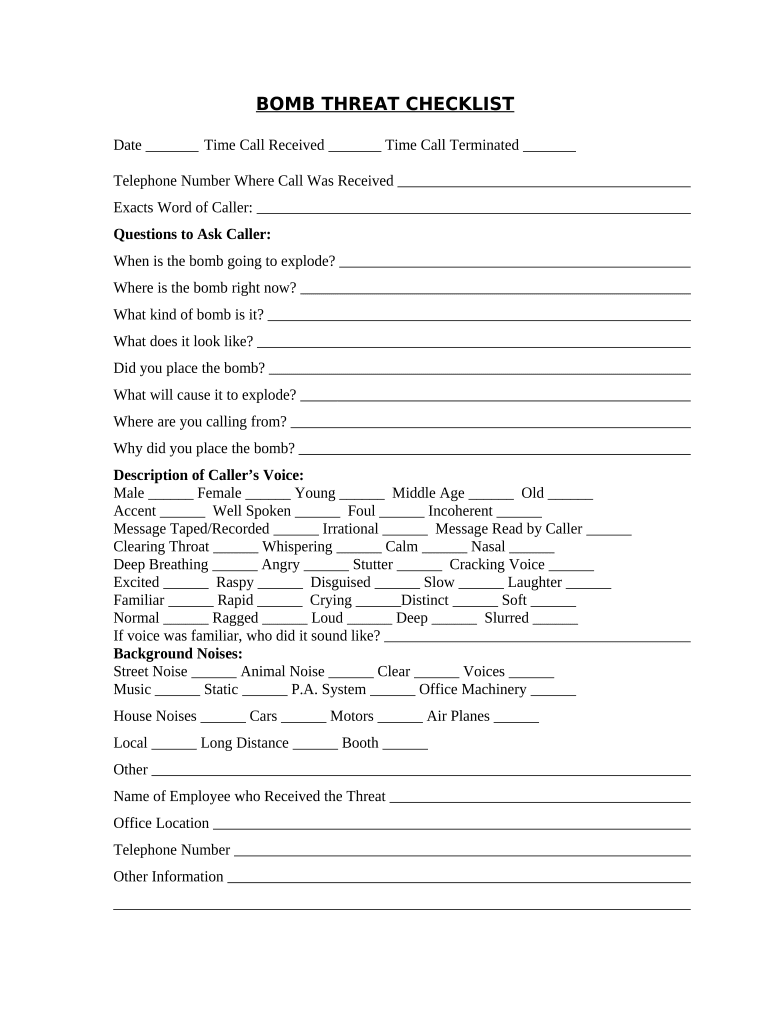
Bomb Threat Checklist Form
Use a Bomb Threat Checklist template to make your document workflow more streamlined.
What the Bomb Threat Checklist Form records
Bomb Threat Checklist Form is a structured incident record for documenting a threatening message and the observations surrounding it. A staff member records the caller’s exact words, stated location, time, voice characteristics, background sounds, number display, and other details that may assist emergency response. The completed checklist can be reviewed by authorized personnel and preserved with its signing history. It does not replace emergency procedures or law-enforcement direction; call emergency services and follow site policy when a threat is received.
Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

Organizations that use the checklist
Bomb Threat Checklist Form is most useful where personnel must capture a threatening message quickly, preserve observations, and route the record through a defined security process.
A small business with one facility can use the checklist to standardize how reception or security staff record threatening calls and route completed observations to an owner or designated response lead. A school district or healthcare network can provide facility-specific templates, capture staff observations consistently, and limit completed records to security, administration, and authorized investigators. A multi-site enterprise can use shared templates, delegated sending, and audit trails to coordinate incident documentation across offices while preserving a separate record for each reported threat.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Challenges in completing the checklist
Call-takers may omit exact wording, caller details, background sounds, or the time and location needed for follow-up. Handwritten notes can become difficult to read, especially when staff record a threatening message during an active security incident. Uncontrolled access can expose sensitive incident details, witness information, or emergency-response instructions to unauthorized personnel. Separate paper copies make it harder to confirm who completed the checklist, when it was reviewed, and whether details changed.
Features that support incident documentation
A structured Bomb Threat Checklist Form helps personnel capture precise observations, route the record for review, and preserve an accountable electronic history.
Structured capture
Capture the caller’s exact words, stated location, time, voice characteristics, background sounds, and other observations in structured fields that support later review.
Review routing
Route the completed checklist to a supervisor or security lead for review without requiring staff to exchange paper copies during an incident.
Audit trail
Record signer identity, timestamps, IP information, and document activity through an audit trail that helps establish how the checklist was handled.
Secure access
Keep incident documentation in a controlled electronic record that authorized personnel can retrieve when coordinating with law enforcement or internal investigators.
Reusable template
Use reusable templates so security teams can maintain consistent prompts across offices, facilities, campuses, or operating shifts.
Mobile completion
Complete the form from a desktop or mobile device when an incident occurs away from an administrative workstation.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the checklist workflow works
signNow turns the Bomb Threat Checklist Form into a controlled electronic workflow while leaving incident-specific facts for the responsible staff member to enter.
Upload: Upload the checklist PDF Verify: Review detected fields Route: Send to authorized reviewers Preserve: Store the signed record
What the audit trail records
The audit trail documents how Bomb Threat Checklist Form moved from preparation through review, signing, completion, and later retrieval.
Identify signer:
Timestamp action:
Log activity:
Seal record:
Attach certificate:
Export history:
Ways to complete and route the checklist
- Use the signNow web app when security or administrative staff need to upload the Bomb Threat Checklist Form, verify fields, and send it from a managed workstation.
- Use the signNow mobile app when authorized personnel must complete observations from a facility floor, reception area, or other location away from a desktop computer.
- Use kiosk mode when a designated station allows multiple authorized staff members to complete or sign the checklist under controlled, in-person supervision.
- Use a shareable signing link only for an identified audience and approved workflow; do not distribute sensitive bomb-threat details through an unrestricted public link.
Platform requirements for the checklist
Bomb Threat Checklist Form can be completed through a current Chrome, Firefox, Safari, or Edge browser on Windows 11 or macOS. signNow protects sessions with TLS 1.2 or TLS 1.3, and its mobile apps support iOS and Android access when personnel must document an incident away from a desk.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows 11 and macOS Mobile devices iOS and Android mobile access
Organizations should use managed Windows, macOS, iOS, or Android devices for sensitive incident records. Confirm camera, notification, and network permissions before deployment, then restrict completed checklists through signNow roles, audit trails, and approved storage policies. Offline availability and device-specific behavior should be tested against the organization’s emergency-response procedures before field use.



Security controls for incident forms
Transport encryption:
Stored encryption:
Security certification:
Information security:
Electronic signatures:
Health information:
Best practices for bomb threat records
Accuracy, controlled access, and a preserved audit history matter because this checklist may guide emergency response and later investigation.
Record the caller’s exact words
Document observations immediately
Restrict incident-record access
Preserve the complete record
Processing stages for the checklist
The workflow moves from field preparation to authorized review, signing, and preservation without changing the incident facts entered by staff.
Prepare the document
Deliver to reviewer
Complete the review
Archive the record
Troubleshooting checklist workflows
These answers address field detection, signer identity, electronic-record consent, audit evidence, and legal limits relevant to Bomb Threat Checklist Form.
signNow can upload a PDF, detect fillable areas, and let the sender add or adjust fields. Review every detected field against the checklist before sending, because automated detection cannot verify incident-specific wording or required response prompts.
The Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month when billed annually. Business Premium adds bulk send, while Enterprise adds advanced signer authentication and conditional fields.
For a consumer-facing electronic record, ESIGN requires disclosure of the right to receive paper records, access to the electronic format, and a method to withdraw consent under 15 U.S.C. §7001(c). Review whether that rule applies to your audience.
SignNow records signer activity in an audit trail, including timestamps and action history. Use the completed document and certificate of completion as part of the incident file, while following your organization’s retention and evidence procedures.
A signing link may be appropriate for an identified response team, but sensitive bomb-threat details require access controls and careful distribution. Use stronger signer authentication where organizational policy or the incident’s sensitivity requires it.
signNow is ESIGN- and UETA-compliant, but those laws do not make every document electronically valid. Wills, court orders, family-law decrees, and other statutory exclusions remain outside the federal electronic-signature framework.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.