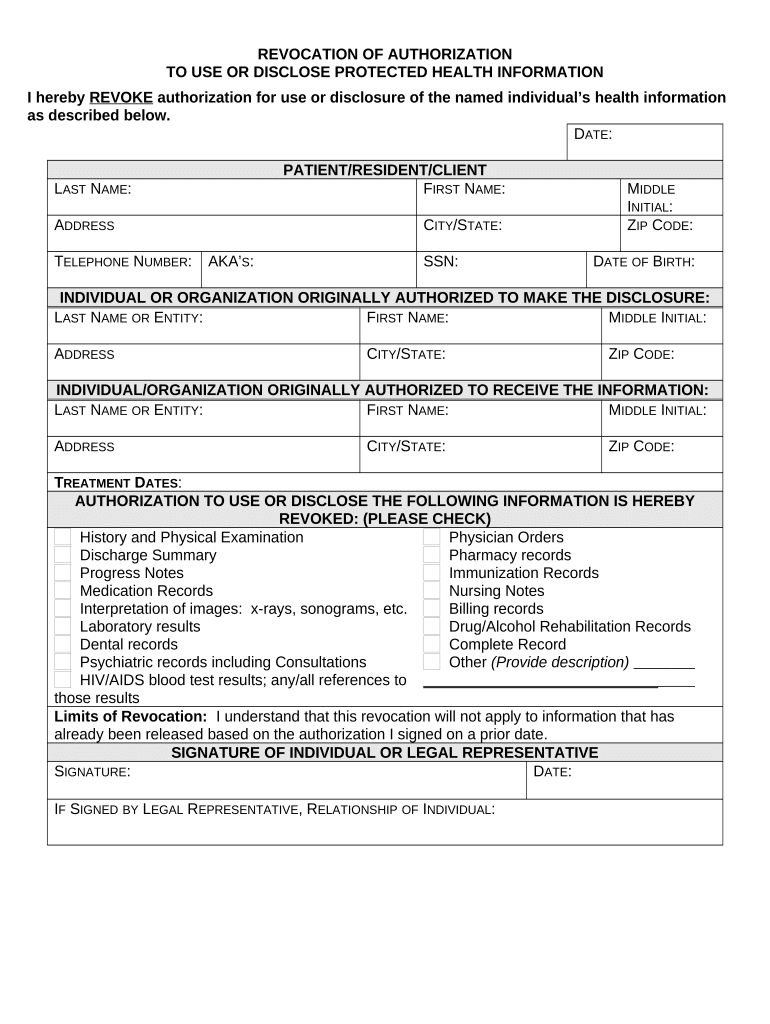
Revocation Authorization Form
Use a Revocation Authorization Form template to make your document workflow more streamlined.
What a Revocation Authorization Form does
A Revocation Authorization Form records that a person or organization is withdrawing authority previously granted to another party. It normally identifies the original authorization, the permission or disclosure being ended, the affected recipient or records, the effective date, and the revoking party’s signature. The recipient then uses the notice to stop relying on the revoked authority, subject to the form’s terms and applicable law. In signNow, you can upload the form, review detected fields, send it for signature, and preserve the completed record with its audit trail.
Who uses a Revocation Authorization Form
Healthcare
Healthcare organizations can use a Revocation Authorization Form to document withdrawal of a previously granted authorization, identify the affected records or disclosure, and capture the signer’s date and signature. A HIPAA-covered workflow should preserve the completed form with related authorization records and apply the organization’s approved privacy controls.
Administrative teams
Legal, financial, and administrative teams can use a Revocation Authorization Form when an individual or business wants to end previously granted authority. The completed document should identify the original authorization, state what is revoked, record the effective date, and preserve evidence that the notice reached the relevant recipient.
Who benefits from this form
Revocation Authorization Forms are useful wherever an organization must document that previously granted authority, consent, or disclosure permission has ended.
A solo attorney can use the form to document a client’s withdrawal of authority, send the notice for signature, and preserve the signed record with an audit trail for the matter file. A healthcare practice can record withdrawal of authorization involving protected health information, provided its workflow addresses HIPAA requirements, access controls, and a business associate agreement where required. An enterprise compliance team can standardize revocation notices through shared templates, delegated sending, and controlled access while retaining audit evidence for internal review and regulatory inquiries.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Complete the form in signNow
Use this sequence to prepare, send, sign, and preserve a Revocation Authorization Form without separating the notice from its evidence.
Upload document:
Upload the Revocation Authorization Form to signNow. Review fields:
Confirm detected fields and add missing details. Set recipients:
Assign recipients and send for signature. Store record:
Download the signed form and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the revocation workflow works
A Revocation Authorization Form becomes easier to manage when its notice, signature, delivery, and evidence remain in one controlled workflow.
Upload form: Upload the completed Revocation Authorization Form. Check fields: Review detected fields and add missing signature or date fields. Send notice: Send the revocation notice to the responsible recipient. Preserve evidence: Store the signed record with its audit trail.
Recommended workflow setup
Configure the Revocation Authorization Form around signer identity, record integrity, and the retention requirements for the authorization being withdrawn.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS code |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export with completed document |
| Document retention | Apply underlying record policy |
| Encryption | AES-256 at rest and TLS 1.2 or 1.3 |
What the audit trail records
The signNow audit trail documents the evidence surrounding a Revocation Authorization Form, helping reviewers connect the signer, actions, timestamps, and final record.
Authenticate signer:
Capture timestamps:
Record version:
Seal document:
Track activity:
Retrieve evidence:
Privacy and disclosure pitfalls
Including unnecessary personal data can expose sensitive information beyond the recipients who need the Revocation Authorization Form. Failing to identify the original authorization may leave recipients unsure which permission, records, or disclosure the revocation addresses. Sending without documented electronic consent or access procedures can weaken reliance on an electronic notice in consumer-facing transactions. Broad user permissions can allow unauthorized staff to view, alter, or send a sensitive revocation record.
Platform requirements for signing
A Revocation Authorization Form can be prepared through supported web browsers on Windows or macOS, while signNow mobile apps support signing on iOS and Android. Use a current browser, an internet connection protected by TLS 1.2 or 1.3, and a device that can display the complete document.
Browsers Chrome, Firefox, Safari, and Edge Operating systems Windows 10, macOS, iOS, and Android Secure connection TLS 1.2 or 1.3 connection
Organizations handling sensitive revocation records should manage devices, accounts, and permissions centrally. signNow plans provide audit trails and mobile apps; enterprise deployments can evaluate SSO, API access, and authentication controls against internal security requirements and the record’s sensitivity.
Security for revocation records
Data encryption:
Transport security:
Security certification:
Information security:
Electronic signatures:
Health information:
Best practices for revocation records
Accurate identification, controlled delivery, and complete evidence make a Revocation Authorization Form easier to interpret and defend.
Identify the authority precisely
Verify every required field
Match controls to sensitivity
Archive the complete record
Legal standing and evidentiary value
A signed Revocation Authorization Form can help show intent, attribution, consent withdrawal, and record integrity in a U.S. business transaction. ESIGN and applicable state electronic-transactions law generally recognize qualifying electronic records, but wills, codicils, court filings, family-law decrees, and other statutory exclusions require separate legal review.

Troubleshoot revocation workflows
These answers address field detection, signer assignment, electronic consent, audit evidence, plan limits, and healthcare safeguards for this form.
Upload the original file again and inspect whether its pages contain selectable fields. signNow can detect fillable fields, but scanned or unusual layouts may require manually placing signature, date, and recipient fields before sending.
Open the recipient settings and confirm the signer’s email address, signing order, and assigned fields. A recipient cannot complete a field assigned to another signer, so reassign the missing signature or date field before resending.
For a consumer-facing electronic record, review the ESIGN Act requirements in 15 U.S.C. §7001(c): disclosure of paper rights, access to the electronic format, and withdrawal procedures. Configure the workflow to document applicable consent before signing.
The signNow Business plan is listed at $8 per user per month with annual billing and includes audit trails. Paid plans include 100 signature invites per user annually; review plan limits and overage terms before sending at scale.
Use signNow’s audit trail to review authentication, timestamps, actions, and the completed record. Export the signed Revocation Authorization Form and audit trail together, then store them under the retention policy for the underlying authorization.
signNow states that HIPAA compliance requires a business associate agreement. If the revocation concerns protected health information, execute the required BAA and apply the healthcare organization’s access, retention, and disclosure procedures.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.