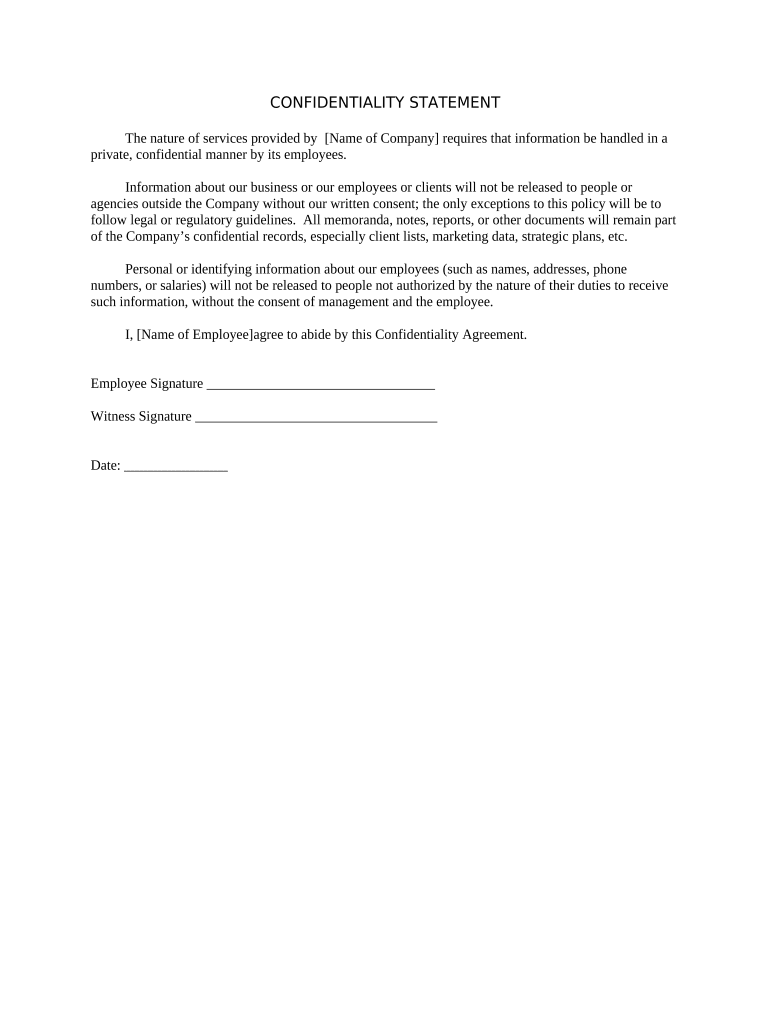
Confidentiality Statement Form
Use a Confidentiality Statement template to make your document workflow more streamlined.
What a confidentiality statement does
A Confidentiality Statement Form records a person’s acknowledgment that specified information must be kept confidential and handled under stated restrictions. It commonly identifies the protected information, permitted use, disclosure limits, recipient or signer, and signature date. In signNow, the sender uploads the statement, reviews detected fillable fields, adds any required signature fields, and sends it to the intended signer. The signer reviews and completes the document, while signNow preserves the completed record and audit trail. ESIGN and UETA generally recognize qualifying electronic signatures, subject to applicable exclusions and consent requirements.
Who uses this form
Business and legal teams
Businesses use confidentiality statements to define how employees, contractors, vendors, and recipients may handle proprietary information. The document can accompany an NDA, employment packet, vendor agreement, or controlled disclosure workflow.
Regulated and project teams
Healthcare, financial-services, technology, and construction organizations use the form when sensitive operational, client, or project information must be acknowledged before access.
Key features for this form
signNow provides a structured way to prepare, route, sign, and retain Confidentiality Statement Forms across business workflows.
Field preparation
Upload the existing confidentiality statement, identify fillable areas, and add signature, initials, date, or text fields before sending.
Recipient routing
Send the statement to employees, contractors, vendors, or other named recipients through a controlled signing request.
Audit evidence
Capture signer activity and completion details in an audit trail connected to the signed confidentiality statement.
Flexible delivery
Use email delivery or a signing link when recipients need access without creating an account.
Record retention
Keep completed forms and audit records available for authorized business review and retention policies.
Business integrations
Connect signed statements with Salesforce, NetSuite, Google Drive, or Microsoft 365 workflows where supported.
How the form works online
A confidentiality statement moves from uploaded document to signed record through four controlled signNow actions.
Upload document: Upload the confidentiality statement PDF to your signNow account. Prepare fields: Review detected fields and add missing signature or date fields. Send to signer: Enter recipients and send the statement for completion. Store evidence: Collect signatures and retain the completed record with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail connects the confidentiality statement to signer activity, document integrity, and a retrievable completion record.
Authenticate signer:
Timestamp action:
Hash document:
Seal record:
Log document history:
Export audit trail:
Security for confidentiality statements
Transport encryption:
Stored encryption:
Security certification:
Information security:
Healthcare safeguards:
Electronic signature law:



Privacy and disclosure pitfalls
Personal information may remain visible in signed copies shared beyond the intended confidentiality audience. Missing electronic-consent language can weaken evidence that a signer agreed to use electronic records. Unrestricted template access can expose proprietary terms before authorized recipients receive the document. A missing audit trail can make signer identity, timing, and document history harder to establish.
Best practices for signed records
Retention and access controls should match the information protected by the Confidentiality Statement Form and the records surrounding it.
Export and protect audit records
Set a documented retention rule
Archive the signed statement securely
Limit disclosure before sending
Retention periods by record class
A Confidentiality Statement Form has no single federal retention period; keep it according to the regulated record or business purpose it supports.
3 years for tax records
6 years for HIPAA records
6 years for broker records
7 years for audit records
30 years for exposure records
Risks of incomplete execution
Signer identity
Electronic consent
Access control
Missing audit trail
Confidentiality form troubleshooting
These answers address field preparation, signer authentication, electronic-signature evidence, healthcare safeguards, and signNow plan limits.
Upload the PDF to signNow, then inspect auto-detected fields. Add any missing signature, date, initials, or acknowledgment fields before sending the Confidentiality Statement Form.
The Business plan includes templates, audit trails, and legally binding eSignatures at $8/user/month with annual billing. Business Premium adds bulk send at $15/user/month annually.
signNow supports ESIGN and UETA requirements for electronic signatures. Confirm signer intent, electronic-record consent, attribution, and record retention; consumer-facing workflows may require the disclosure described in 15 U.S.C. §7001(c).
A HIPAA-covered confidentiality statement requires an appropriate business associate arrangement and documented safeguards. signNow lists HIPAA compliance with a BAA required; the organization remains responsible for its privacy obligations.
Use signNow authentication controls appropriate to the disclosure risk, such as SMS-based verification where configured. Review the audit trail for signer identity, timestamps, and document history before relying on the record.
Paid subscription plans include 100 signature invites per user per year, with overage fees. The Site License uses $1.50 per signature invite and is designed for usage-based deployment.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.