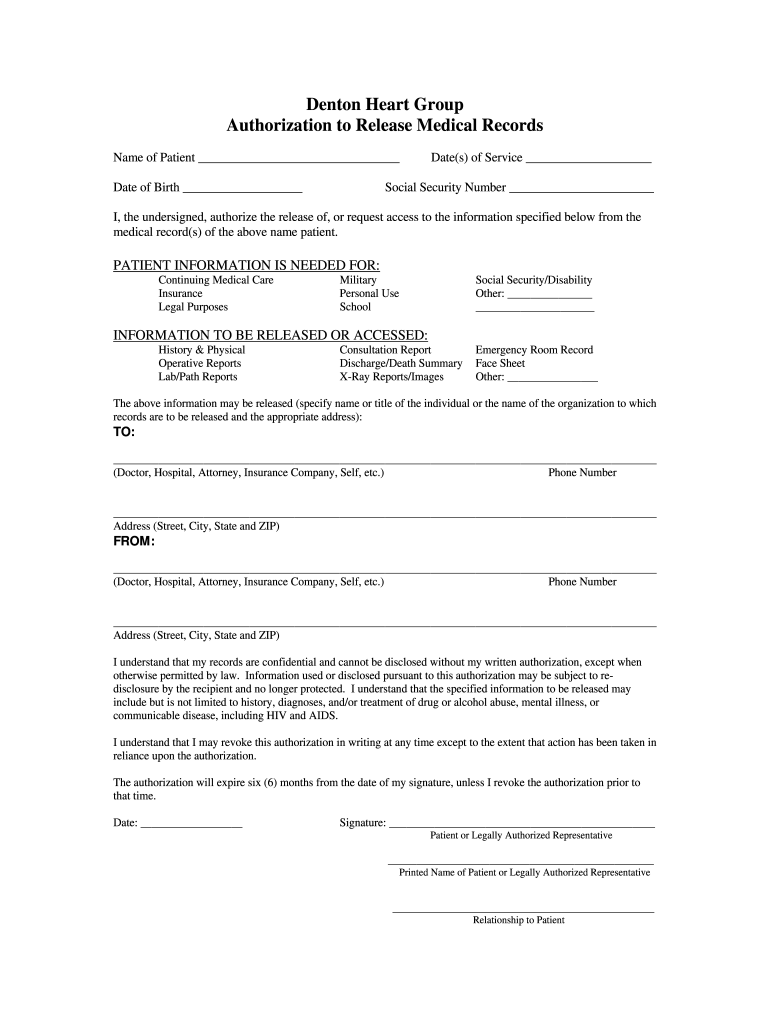
Generic Release Of Information Form
Create a custom Generic Release Of Information Form 0 that meets your industry’s specifications.
What this release form does
A Generic Release Of Information Form is a written authorization allowing a named person or organization to disclose specified information to an identified recipient for a stated purpose. It can cover medical, employment, financial, legal, or other records, but its scope should identify the information, recipient, purpose, and expiration. With signNow, upload the form, place or detect fillable fields, send it to the authorized signer, and preserve the completed record with its audit trail. HIPAA-related disclosures require appropriate authorization and safeguards; state law may impose additional requirements.
Who uses this release form
Healthcare and legal
Healthcare providers use the form to authorize disclosure of patient records, treatment information, and insurance details, with HIPAA safeguards and documented consent. Human resources teams use it for employee records and benefits administration, while legal departments use it to authorize specific disclosures during disputes or transactions.
Business operations
Businesses use the form for contracts, NDAs, invoices, HR records, and consent requests when a person or organization must authorize information sharing. Clear recipient details, permitted purposes, expiration dates, and signature records help reduce disclosure errors and create an accessible record of authorization.
How the release form works
A release form identifies who may disclose specified information, who may receive it, and why the disclosure is permitted.
Complete details: Enter the disclosing party, recipient, purpose, records, and expiration date. Add fields: Review the authorization scope and add required signer fields. Request signatures: Send the release to authorized signers by email or link. Store records: Download the completed form with its audit trail.
What the audit trail records
The signNow audit trail documents who interacted with the release, what they did, and when the completed authorization was preserved.
Authenticate signer:
Capture timestamps:
Hash document:
Seal activity:
Track consent:
Export audit trail:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features for release authorizations
signNow connects field preparation, signer routing, authentication, audit evidence, and record storage around the specific authorization details this form requires.
Fillable fields
Place names, dates, purposes, recipients, signatures, and authorization fields directly onto the release before sending it for completion.
Signer routing
Route the authorization to the person approving disclosure and capture the signed record without paper handling.
Audit trail
Record authentication events, timestamps, and document history to support consent and later review.
Signer security
Use SMS authentication or configured signer controls when the release contains sensitive personal or health information.
Secure storage
Preserve the completed release and audit evidence together for retrieval under the organization’s records policy.
Reusable template
Reuse an approved release layout while updating the recipient, purpose, records, and expiration for each authorization.
Security for signed releases
Stored data:
Data transmission:
Service controls:
Security management:
Health information:
Electronic signatures:
Recommended release form setup
Configure the release around signer identity, authorization evidence, privacy safeguards, retention obligations, and controlled access to completed records.
| Setting | Recommendation |
|---|---|
| Authentication method | Email with SMS verification |
| Signature type | Electronic signature with intent |
| Audit trail | Enable complete signing history |
| Document retention | Six years for HIPAA records |
| Encryption | AES-256 at rest and TLS in transit |
Record-keeping practices for releases
Careful scope, audit-trail export, retention analysis, and restricted storage help preserve the authorization’s evidentiary and privacy value.
Define the disclosure scope precisely
Export the audit trail with records
Match retention to the record
Archive signed releases securely
Privacy pitfalls in release forms
Including full medical histories when the recipient needs only specified treatment records exposes unnecessary protected health information. Leaving the purpose, recipient, or expiration date blank can weaken consent and create uncertainty about permitted disclosure. Sending the completed release to an unverified email address can disclose personal information to the wrong recipient. Allowing broad internal access to signed releases increases exposure risk and weakens documented access control.
Legal standing of this release form
A signed release can provide evidence of authorization when the signer intended to sign, consented to electronic records, can be identified, and the record remains reproducible under ESIGN and applicable UETA law. Wills, codicils, testamentary trusts, court orders, official court filings, and certain family-law documents are excluded from ESIGN’s coverage.

State rules and document exclusions
State law may require acknowledgment
ESIGN exclusion applies
Court filing rules may control
Recording office requirements apply
Troubleshooting release form workflows
These answers address field setup, electronic-signature validity, privacy controls, plan limits, recipient errors, and retention for this authorization form.
Upload the release as a PDF or editable document, then place signature, date, and text fields manually. signNow Business includes templates and audit trails, allowing you to preserve the completed authorization and signing history.
A release may be electronically signed when the parties demonstrate intent, consent to electronic records, signer attribution, and record retention. ESIGN, 15 U.S.C. ch. 96, and applicable UETA rules support electronic records, subject to document-specific exclusions and state law.
Use signNow’s SMS authentication or stronger signer authentication when the release contains protected health information. HIPAA compliance requires a business associate agreement with signNow and appropriate access controls; the form itself must still capture valid authorization.
The signNow Business plan costs $8 per user per month when billed annually and includes audit trails and templates. Paid subscription plans include 100 signature invites per user per year, with overage fees; Business Premium adds bulk send.
Use role-based recipients and verify the recipient’s email before sending. Restrict the authorization to named records, purposes, and dates, because a broad release may disclose more information than the underlying consent permits.
Export the completed document and audit trail from signNow, then store both under the applicable records policy. HIPAA-related records require six years from creation or the last effective date under 45 CFR §164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.