Muschealth Orgpatients Visitorsmedical Recordsobtaining Musc Medical Recordsmusc Healthcharleston Sc Form
Use a Muschealth orgpatients visitorsmedical recordsObtaining MUSC Medical RecordsMUSC HealthCharleston SC template to make your document workflow more streamlined.
What this medical records form does
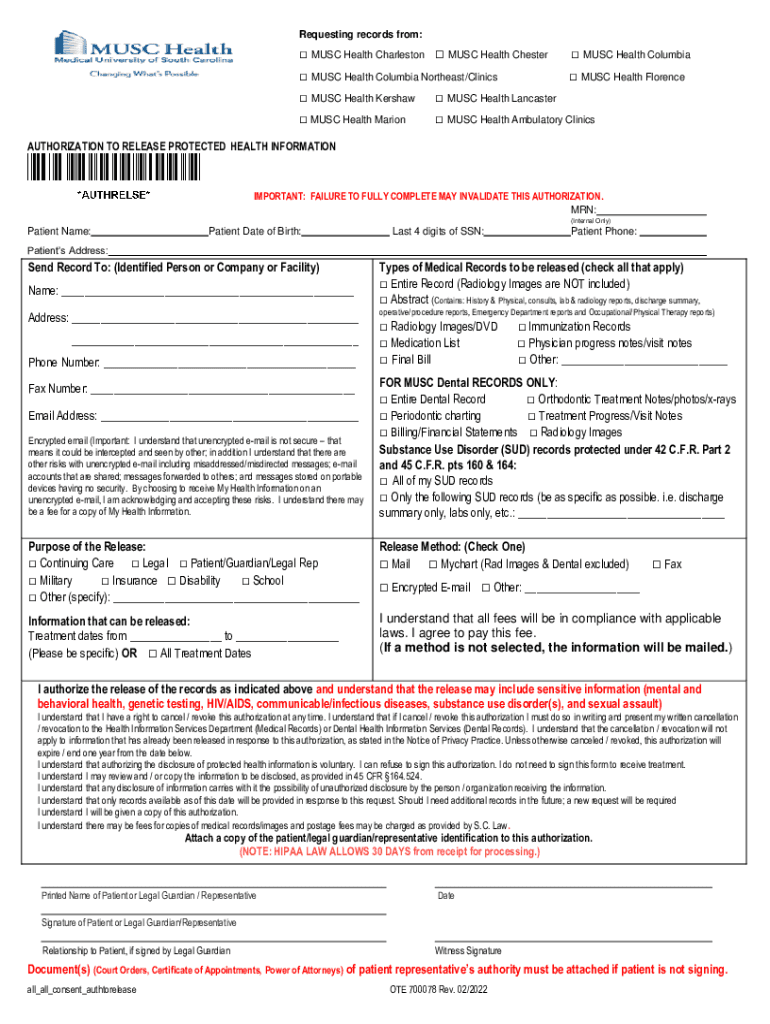
This form is a request and authorization record used to obtain medical records from MUSC or an associated Charleston, South Carolina healthcare provider. The requester identifies the patient, specifies the records and date range sought, provides delivery instructions, and authorizes release to the named recipient. A provider may verify identity, confirm authorization, and apply applicable HIPAA and South Carolina requirements before releasing information. With signNow, the completed form can be uploaded, fields can be prepared, signatures can be collected, and the final record can be stored with an audit trail.
Who uses this MUSC form
Patients
Patients and authorized representatives use the form to identify the requested MUSC records, approve disclosure, and specify the intended recipient and delivery method.
Healthcare teams
Healthcare administrators and release-of-information teams use the signed authorization to review scope, confirm identity, and document controlled disclosure workflows.
Complete the MUSC records request
Prepare the MUSC medical records request in signNow by checking identity, authorization, requested dates, recipient details, and delivery instructions before sending.
Upload form:
Upload the medical records request PDF. Check fields:
Review detected fields and add missing patient details. Add signer:
Enter the patient or authorized representative as signer. Send request:
Send the authorization through signNow. Complete form:
Collect the signature and download the completed copy.
Audit trail for the authorization
The audit trail helps show who completed the MUSC authorization, when actions occurred, and whether the completed document changed afterward.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Record activity:
Export evidence:
Recommended workflow setup
Use a controlled signing workflow that identifies the patient, limits disclosure, and preserves the completed authorization with its supporting evidence.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion history export |
| Document retention | Six years under 45 CFR 164.530(j) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for medical record requests
Transport encryption:
Stored data protection:
Security certification:
Information security:
Health information:
Electronic signatures:
Legal standing of the authorization
A signed MUSC medical records authorization can support a release request when it demonstrates the signer’s intent, identifies the records and recipient, and can be reproduced with its signing history. ESIGN and applicable state electronic-transactions law support electronic signatures, while HIPAA requirements and provider policies still govern disclosure.

Key features for this authorization
signNow features can support the specific MUSC medical records workflow from form preparation through signature collection, audit evidence, and controlled archival.
Form preparation
Upload the MUSC authorization and prepare its patient, representative, recipient, and signature fields without recreating the form.
Signer routing
Route the request to the identified patient or authorized representative through a controlled signing invitation.
Audit trail
Capture timestamps, signer actions, and completion history that help document how the authorization was executed.
Data protection
Use encryption in transit and at rest when storing a completed authorization within the signNow workflow.
Mobile signing
Collect signatures through desktop or mobile workflows when the signer cannot attend an in-person appointment.
Secure archive
Download the signed authorization and completion evidence for the healthcare organization’s approved records system.



Platform requirements for this form
The signNow workflow for this MUSC authorization runs in Chrome, Firefox, Safari, or Edge on Windows and macOS, with signNow mobile apps available for iOS and Android.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows and macOS desktops Mobile apps iOS and Android signNow apps
Organizations handling protected health information should use managed devices, role-based access, and approved storage. Confirm that the selected signNow plan and business process support HIPAA requirements, including a business associate agreement where required, before routing patient records.
Privacy pitfalls in records requests
Including a patient’s full medical history when only a defined date range or department is authorized increases unnecessary disclosure exposure. Sending the signed authorization to an unverified recipient can disclose protected health information outside the intended release. Leaving representative authority or patient identity fields incomplete can delay MUSC verification and prevent records from being released. Using an unsecured email address or shared folder for the completed form can expose sensitive patient information.
Best practices for MUSC requests
Accurate identity details, a narrow records scope, controlled delivery, and documented retention make this medical-records authorization easier to review and protect.
Verify patient identity before sending
Define the records and date range
Limit the authorized recipient
Archive the signed authorization securely
Retention rules for the authorization
Retention depends on the organization and record type. For HIPAA-covered documentation associated with this request, the federal minimum listed below is six years under 45 CFR 164.530(j).
Six years: HIPAA documentation
Six years: privacy policies
Six years: privacy communications
Six years: documented actions
Six years: responsible designations
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting MUSC records requests
Use these answers to resolve signer, privacy, audit-trail, and plan questions before sending a MUSC medical records authorization.
Business includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, SOC 2, and GDPR features. HIPAA use requires a BAA, so confirm the applicable signNow arrangement before processing protected health information.
A missing signer email or incomplete patient identity field can prevent routing or provider review. Reopen the draft, verify the signer’s address, and check every required field before resending the MUSC authorization.
Use signNow’s audit trail to preserve timestamps, signer activity, and completion history. ESIGN and UETA focus on intent, consent, attribution, and record reproducibility; the audit trail helps document those elements but does not replace HIPAA authorization requirements.
HIPAA compliance is listed for signNow with a BAA required. A BAA does not make every workflow compliant automatically; limit access, identify the recipient, and follow the covered entity’s privacy and security procedures.
Business Premium adds bulk send and kiosk mode, while Business provides templates, audit trails, and mobile apps. A single MUSC authorization generally does not require bulk send; choose the plan based on the organization’s workflow volume.
Electronic signatures generally receive legal recognition under ESIGN and applicable state law when intent, consent, attribution, and reproducible records are present. Provider policy, HIPAA requirements, and any required identity verification still control whether MUSC accepts the authorization.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.