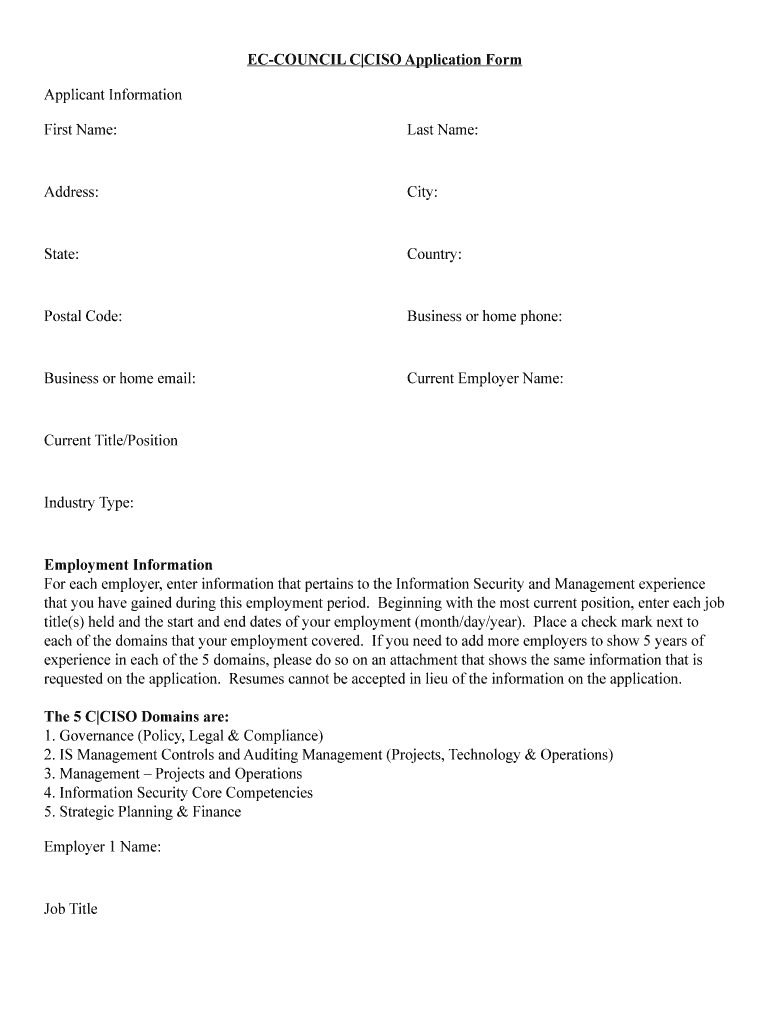
Cciso Exam Eligibility Application Form Certified Ciso Ec Council
Create a custom CCISO Exam Eligibility Application Form Certified CISO EC Council 0 that meets your industry’s specifications.
What the CCISO eligibility application does
The CCISO Exam Eligibility Application is the application used to request eligibility review for the Certified Chief Information Security Officer examination administered by EC-Council. It collects the applicant’s professional background, education, experience, and related evidence for review. The form is not the CCISO examination itself and does not establish certification by itself. Applicants should use the current EC-Council instructions, enter consistent career information, attach requested documentation, and retain the submitted application and completion record. SignNow can organize the form, collect signatures, and document the signing history.
Legal standing of the signed application
For a business transaction, an electronic record and signature may receive legal recognition under the federal ESIGN Act, 15 U.S.C. chapter 96, and applicable state law, including UETA or New York’s ESRA. That recognition does not guarantee EC-Council acceptance or replace its eligibility rules. Wills, court filings, and family-law decrees remain excluded from ESIGN’s scope.

How to complete the CCISO application
Use this sequence to prepare the CCISO Exam Eligibility Application, route it for review, and preserve the completed record in signNow.
Upload form: Upload the CCISO application PDF to signNow. Check fields: Auto-detect fillable areas and review field placement. Assign signers: Add the applicant and authorized reviewer as signers. Complete record: Collect signatures and retain the completed record.
Features for the CCISO eligibility workflow
signNow applies document preparation, signer routing, audit history, and storage controls to the specific CCISO Exam Eligibility Application workflow.
Form preparation
Upload the CCISO eligibility application and review detected fields before sending, reducing manual placement work while keeping the applicant’s original document structure visible.
Signer routing
Assign applicant and reviewer fields directly on the CCISO application so each person receives only the actions required for completing or approving the submission.
Audit trail
Collect signatures electronically with an event history that documents signing actions, timestamps, and the completed application record for later administrative review.
Reusable template
Use templates for recurring employer-supported CCISO applications while preserving the form-specific fields and instructions required for each candidate’s eligibility submission.
Document storage
Connect completed applications with Google Drive or Box for controlled storage, subject to the organization’s retention and access policy.
Mobile signing
Use mobile apps when applicants or reviewers need to inspect and sign the CCISO application away from a desktop workstation.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Who uses the CCISO application
Cybersecurity directors pursuing EC-Council’s CCISO credential can use a controlled signing workflow to submit professional history, eligibility evidence, and reviewer approvals without repeatedly emailing editable copies of the application. Security consulting firms and employer-supported candidates can route one CCISO eligibility application through designated administrators, preserving signer identity, timestamps, document history, and access controls for internal records.
Recommended CCISO application setup
Configure the CCISO application workflow around signer identity, controlled access, auditability, and the retention policy that applies to the applicant’s records.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signing intent |
| Audit trail | Capture timestamps and signer actions |
| Document retention | Follow EC-Council and organizational policy |
| Encryption | AES-256 at rest and TLS in transit |
Security controls for application records
Encryption:
Secure transfer:
Independent controls:
Security management:
Electronic signatures:
Protected health data:
What the CCISO audit trail records
The audit trail supplements the CCISO application by recording who acted, what changed, and when the completed document was finalized.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Preserve history:
Export trail:
Platform requirements for the CCISO application
Prepare the CCISO Exam Eligibility Application in signNow using Chrome, Firefox, Safari, or Edge on Windows or macOS. The signNow mobile apps support signing on iOS and Android devices.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows and macOS desktop access Mobile apps iOS and Android signNow apps
Organizations supporting CCISO applicants should use managed devices, approved browser versions, and role-based access for application records. Where integrations or automated provisioning are required, confirm the selected signNow plan supports the organization’s API, SSO, storage, and administrative controls before deployment.
Retention rules for CCISO application records
The CCISO application has no single universal federal retention period identified here. Apply only a rule that genuinely covers the record’s contents and purpose.
CCISO application records
3 years: tax records
6 years: HIPAA records
3 years: payroll records
Longer applicable period
Challenges when preparing the CCISO application
Applicants may not know which experience, education, or certification evidence the CCISO eligibility review requires before submission. Manually transferring career history into the CCISO application can create inconsistent dates, titles, and supporting-document references. Multiple reviewers may need access to one application while limiting exposure of identity, employment, and professional background information. Incomplete signatures or missing attachments can delay an eligibility review when the application is sent without a final checklist.
CCISO application troubleshooting
Resolve these named CCISO application issues by checking field assignment, signer delivery, plan limits, consent obligations, acceptance rules, and record retention.
Upload the original CCISO application PDF again and inspect detected fields before sending. If a required area was missed, place the field manually and confirm that the applicant, reviewer, and signature fields are assigned correctly. The Business plan includes templates and audit trails for this workflow.
Check the recipient email address, spam filtering, and signing-order settings first. Resend the invitation from the document workspace after confirming the CCISO applicant’s address. A shareable signing link can provide another delivery method, but access should remain limited to the intended signer.
The Business plan is listed at $8 per user per month with annual billing and includes 100 signature invites per user per year. If the organization needs bulk send, Business Premium is listed at $15 per user per month annually.
For consumer-facing electronic records, ESIGN requires disclosure of the right to receive paper records, access to the electronic format, and a process for withdrawing consent under 15 U.S.C. §7001(c). Apply that requirement when the CCISO workflow involves a consumer-facing transaction.
signNow states that its electronic signatures comply with ESIGN and UETA, but EC-Council’s current application instructions control acceptance. Confirm whether EC-Council requires a particular signature, attachment, or submission method before relying on an electronic copy.
Export the completed CCISO application and its audit trail from signNow, then store both under the organization’s documented retention policy. No universal federal retention period was identified for this specific EC-Council application, so do not substitute HIPAA, tax, or employment schedules without a separate applicable basis.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.