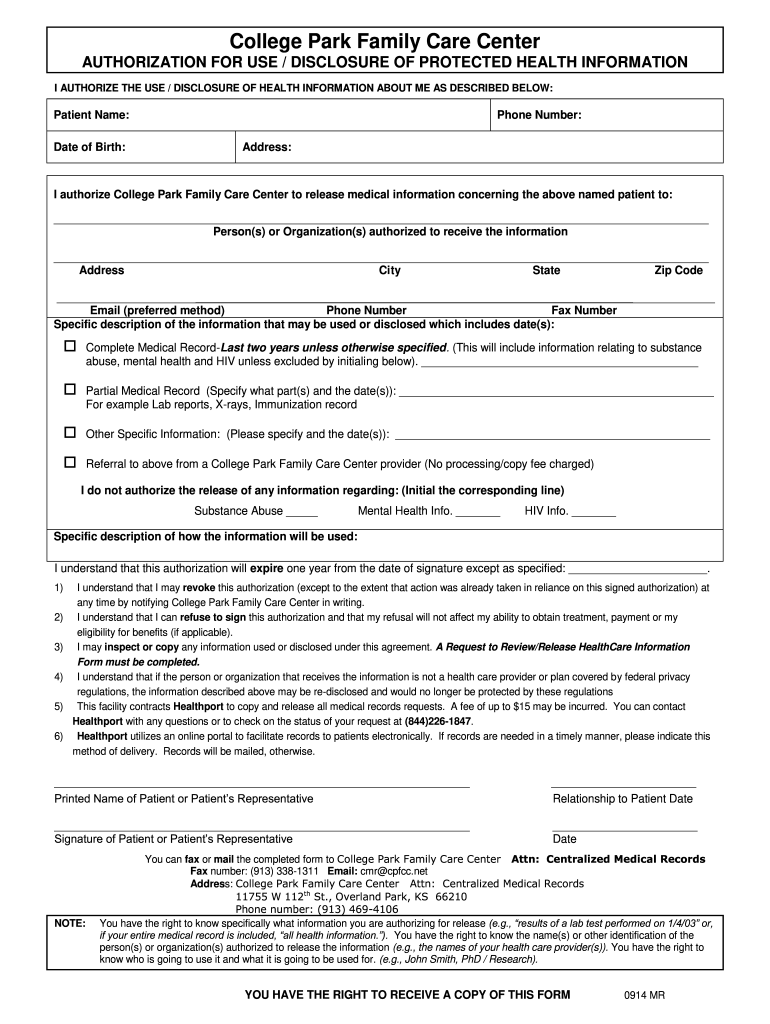
Authorization For Usedisclosure Of Protected Health Information
Use a Authorization For UseDisclosure Of Protected Health Information template to make your document workflow more streamlined.
What this authorization form does
An Authorization for Use or Disclosure of Protected Health Information lets a patient identify the health information that may be used or disclosed, name the recipient, state the purpose, and sign consent. Under HIPAA, a valid authorization generally describes the information, person or class authorized to disclose it, recipient, purpose, expiration, and signature. The signed record helps a healthcare provider document permission before releasing protected health information. Electronic signing may also be recognized under ESIGN and applicable state electronic-transactions law when consent and record-access requirements are met.
Who uses this authorization form
Healthcare providers
Healthcare providers use patient authorizations to document permission before releasing records to family members, insurers, attorneys, researchers, or another named recipient.
Patients and representatives
Patients and authorized representatives review the disclosure scope, recipient, purpose, expiration, and signature before permitting protected health information to be shared.
Features that fit authorization workflows
signNow combines document preparation, patient signing, authentication, audit evidence, and controlled storage for authorization workflows involving protected health information.
Field preparation
Upload the authorization PDF and review signNow’s detected fields before adding or correcting patient, recipient, purpose, expiration, and signature fields.
Remote signing
Send the document to the patient or representative by email, or use a controlled signing link when the workflow permits.
Consent capture
Collect typed or drawn signatures with an electronic record of signer activity, timestamps, and completion events.
Signer verification
Use SMS OTP or other available authentication controls when the disclosure risk requires stronger signer verification.
Audit trail
Retain the completed authorization and certificate of completion with the related disclosure documentation for later review.
HIPAA workflow
Use a HIPAA-supported configuration with a BAA and safeguards for protected health information in transit and at rest.
Complete the authorization in signNow
Prepare the patient authorization in signNow by checking its disclosure scope, recipient, purpose, expiration, and signature fields before delivery.
Upload:
Upload the authorization PDF Check fields:
Review detected fields and add missing recipient, purpose, expiration, and signature fields. Send:
Send the authorization to the patient or representative. Complete:
Collect the signature and download the completed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended authorization workflow setup
Use a controlled workflow that confirms the patient’s identity, preserves consent evidence, and limits access to protected health information.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps and signer actions |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
What the audit trail records
A signNow audit trail documents the technical events surrounding this patient authorization, helping staff connect the signed record with its completion history.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident sealing:
Completion certificate:
Audit export:
Security for protected health information
HIPAA safeguards:
Stored data:
Data transmission:
Control reporting:
Security management:
Electronic signatures:



Platform requirements for signing
A patient authorization can be prepared and signed through a supported web browser or signNow mobile app. Use current Chrome, Firefox, Safari, or Edge on Windows or macOS, or use the iOS and Android applications.
Supported browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile systems iOS and Android mobile apps
Healthcare organizations should also manage device access, user provisioning, and API permissions according to their HIPAA security policies. A HIPAA workflow requires a business associate agreement with signNow and appropriate administrative, technical, and physical safeguards for protected health information.
Privacy pitfalls to avoid
A vague description of records can authorize more disclosure than the patient intended and make later review difficult. An unnamed recipient or missing purpose can prevent staff from confirming whether the proposed disclosure matches the patient’s consent. Sending protected health information to an incorrect email address can expose sensitive records outside the intended recipient’s control. Unrestricted staff access to completed authorizations can increase privacy risk and weaken the organization’s ability to demonstrate minimum-necessary handling.
Retention schedule for authorization records
Retention depends on the record category and governing rule. For a HIPAA authorization, use the HIPAA documentation period and check state healthcare-record requirements before destruction.
6 years: HIPAA authorization records
3 years: federal tax records
6 years: substantial tax understatement
Not applicable: employment records
State law: verify longer periods
Risks from incomplete authorization
Disclosure may lack authorization
Consent evidence is incomplete
PHI may reach an unintended party
Additional rules may apply
Authorization form troubleshooting
Use these answers to resolve field, authentication, HIPAA configuration, plan, and retention questions before releasing protected health information.
signNow can upload a PDF and detect fillable fields, but staff should review every field against HIPAA authorization requirements. Confirm the information description, recipient, purpose, expiration, patient signature, and any required notices before sending.
signNow supports HIPAA-compliant use when the required business associate agreement is in place. Configure access controls and authentication, and confirm that the organization’s workflow protects PHI beyond the signing event.
The Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month with annual billing. HIPAA use requires the appropriate contractual and administrative configuration.
Business Premium costs $15 per user per month with annual billing and adds bulk send and kiosk mode. Bulk send is useful only when each authorization is individually reviewed for patient-specific information.
Signers can receive an email invitation and may use SMS OTP when stronger authentication is needed. Authentication does not replace checking the authorization’s recipient, purpose, scope, and expiration.
The HIPAA documentation rule requires six years from creation or the last effective date under 45 CFR 164.530(j). Export the completed authorization and audit trail, then apply state retention rules that require longer storage.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.