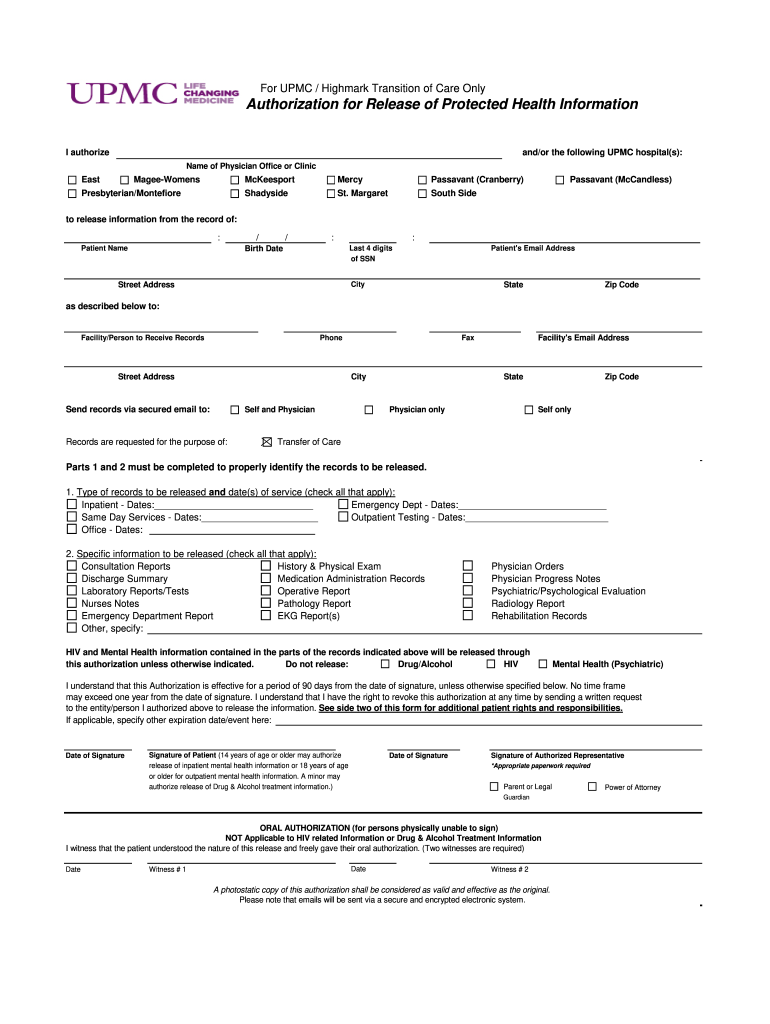
Upmc Authorization To Release Information
Create a custom Upmc Authorization To Release Information 0 that meets your industry’s specifications.
What the UPMC authorization does
The Upmc Authorization To Release Information is a healthcare authorization that records a patient’s permission for UPMC to disclose health information to an identified recipient. It helps UPMC staff confirm what may be released, why the disclosure is requested, and how the authorization was approved. With signNow, a sender uploads the form, places or confirms fillable fields, sends it to the required signer, and stores the completed copy with an audit trail. HIPAA privacy requirements still govern the underlying disclosure, regardless of signing method.
Who completes and handles this authorization
Patients
Patients authorize UPMC to release specified health information to an identified recipient.
UPMC staff
UPMC release-of-information staff route, verify, and retain completed authorizations.
Who uses the UPMC authorization form
UPMC patient-access teams use the authorization to route approved health information to the named recipient, while preserving the signed document and audit history for later review under HIPAA procedures. Patients and designated representatives use the form to document permission for UPMC to disclose specified health information, helping recipients receive an attributable electronic record instead of relying on an unsigned email request.
How the UPMC authorization workflow works
The signNow workflow moves the UPMC authorization from upload through signature while preserving evidence of completion.
Upload form: Upload the UPMC authorization Prepare fields: Confirm or place required fields Send request: Send it to the authorized signer Archive record: Store the signed copy and audit trail
Quick steps for the UPMC authorization
Use this sequence to prepare, sign, and preserve the Upmc Authorization To Release Information in signNow.
Upload form:
Upload the completed UPMC form Detect fields:
Let signNow detect fillable fields Review details:
Review recipients and disclosure details Send signature:
Send for the required signature Store evidence:
Store the signed form and audit trail
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the audit trail records authorization
signNow records each signing event so UPMC authorization activity can be reviewed, verified, and exported with the completed document.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident sealing:
Event logging:
Audit retrieval:
Recommended UPMC authorization setup
Configure the UPMC authorization workflow around verified identity, attributable consent, protected records, and documented retention.
| Setting | Recommendation |
|---|---|
| Authentication and provisioning | Use role-based access with signer verification |
| Signature type | Use an electronic signature with intent |
| Audit trail | Retain certificate of completion |
| Document retention | Six years under HIPAA 45 CFR 164.530(j) |
| Encryption | Use TLS 1.2/1.3 and AES-256 |
Security controls for UPMC records
HIPAA protection:
SOC 2 Type II:
ISO 27001:
Transit encryption:
Stored encryption:
Privacy controls:



Healthcare authorization workflow examples
Healthcare teams can apply signNow’s document workflow to patient authorization records while keeping disclosure decisions under UPMC privacy procedures.
Fertility healthcare
Fertility Centers of Illinois uses signNow for healthcare documents and has cited its API and responsive implementation support.
- Healthcare authorization workflows need attributable patient signatures.
The customer story supports using signNow for structured healthcare document workflows, but it does not establish a specific UPMC deployment or authorization turnaround. Any UPMC team should configure fields, recipients, access controls, and retention according to its own privacy procedures.
Patient services
A healthcare operations team can upload the UPMC authorization, confirm its disclosure fields, and route it to the patient or representative.
- Completed forms remain linked to signing evidence.
This scenario keeps the authorization workflow focused on the actual document: identify the signer, capture permission, preserve the completed copy, and retain the audit trail. It does not replace UPMC privacy review or determine whether a particular disclosure is permitted.
Privacy pitfalls in release authorizations
Patient identifiers or recipient details may be entered incorrectly, creating ambiguity about whose information UPMC may disclose. A missing signature, date, or authorization scope can prevent staff from treating the release request as complete. Sending the authorization to the wrong recipient can expose protected health information beyond the intended disclosure. Broad sharing permissions can create privacy risk when the requested information exceeds the stated purpose.
Best practices for authorization records
Accurate fields, controlled access, and complete evidence help keep UPMC authorization records usable throughout their retention period.
Verify every authorization field before sending
Match authentication to disclosure sensitivity
Export and archive the complete record
Document the controlling retention period
Retention schedule for authorization records
Keep signed authorization materials for the applicable federal period, while checking UPMC policy and any longer state requirement.
Six years — authorization copy
Six years — signed release
Six years — completion certificate
Six years — disclosure record
Six years — electronic record
Troubleshooting UPMC authorization workflows
These answers address field preparation, signer evidence, HIPAA configuration, plan capabilities, and protection of the completed authorization record.
On the Business plan, upload the UPMC authorization, place signature fields, and send it for completion. Business includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, SOC 2, and GDPR controls; HIPAA use requires a BAA.
A missing signature field usually means the uploaded PDF was not prepared correctly. Review auto-detected fields, add the patient or representative signature field manually, confirm the recipient, and send a new request rather than relying on an incomplete document.
signNow records timestamps, document history, signer actions, and a certificate of completion. Export those records with the signed authorization and restrict access because the audit trail supports evidence of signing but does not decide whether disclosure is permitted.
HIPAA-compliant use requires a business associate agreement with signNow. Confirm the BAA and configure access controls before routing protected health information through the workflow; the HIPAA certification or feature label alone does not replace that agreement.
Business Premium adds bulk send and kiosk mode, while Enterprise adds advanced signer authentication, formula fields, conditional fields, payments, and advanced integrations. Select a plan based on UPMC workflow needs rather than assuming every feature exists on Business.
signNow encrypts data in transit with TLS 1.2/1.3 and at rest with AES-256. Encryption protects stored and transmitted records, but staff must still verify recipients, limit access, and follow UPMC privacy procedures for each release.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.