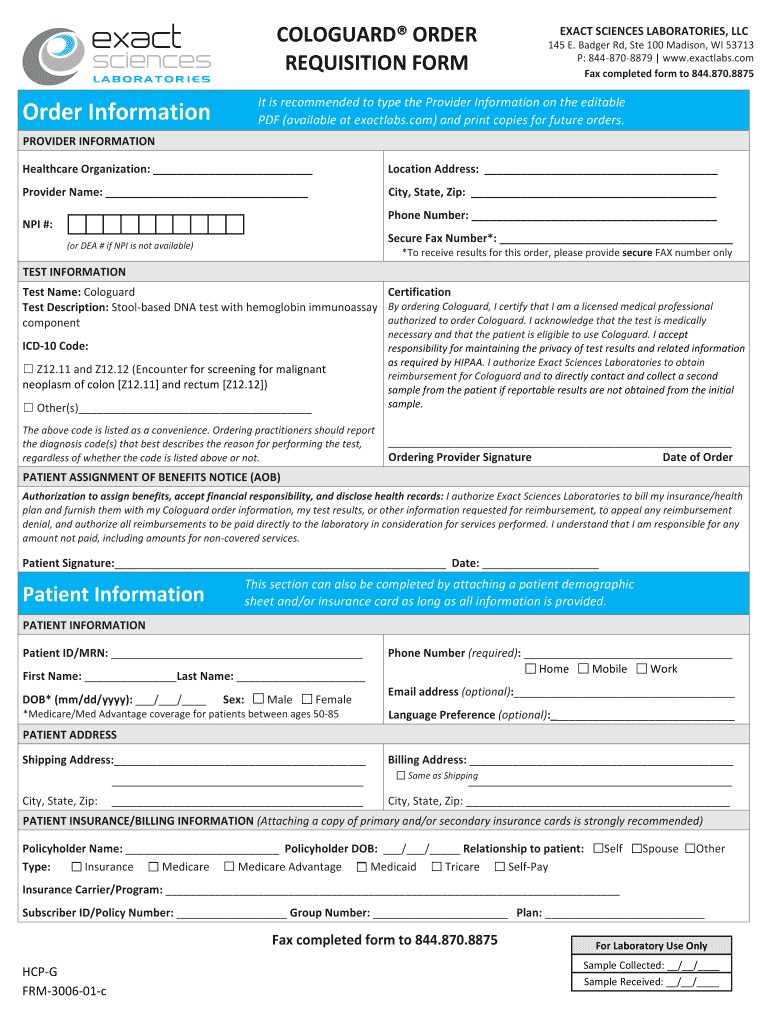
Cologuard Order Form
Use a Cologuard Order Form 0 template to make your document workflow more streamlined.
What the Cologuard Order Form does
The Cologuard Order Form collects information and authorization needed to order a Cologuard colorectal cancer screening test. A healthcare provider or authorized organization supplies the form, the patient reviews the requested information, and the patient signs where required. With signNow, the sender uploads the form, reviews auto-detected fillable fields, sends it to the signer, and stores the completed PDF with an audit trail. The form does not replace clinical advice, laboratory processing, insurance review, or provider verification. When protected health information is present, HIPAA safeguards and applicable organizational policies govern access and retention.
Who uses the Cologuard Order Form
Healthcare providers
Healthcare providers use the Cologuard Order Form to collect patient information and authorization connected with colorectal cancer screening. Teams should limit access to the completed form, apply HIPAA safeguards when protected health information is present, and preserve the signed record and audit trail.
Patients
Patients complete requested fields and sign the Cologuard Order Form electronically when the workflow permits. A provider should confirm that the submitted information is accurate and explain any separate clinical, laboratory, or insurance steps that the form itself does not replace.
How the Cologuard form workflow works
signNow moves the Cologuard Order Form from upload through field review, signature collection, and auditable storage.
Upload form: Upload the Cologuard Order Form Review fields: Auto-detect and review fillable fields Send form: Send the prepared form to the signer Store record: Store the signed form with its audit trail
How the Cologuard audit trail works
The audit trail records technical evidence around each Cologuard Order Form signing event, separate from preparing the form itself.
Authenticate signer:
Timestamp action:
Hash document:
Seal document:
Log activity:
Export evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended Cologuard form setup
Configure Cologuard Order Form workflows around signer identity, protected health information, auditability, and controlled access.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture IP, timestamps, and signer actions |
| Document retention | Retain six years for HIPAA records |
| Encryption and provisioning | AES-256 with administrator-managed users |
Security for Cologuard form data
HIPAA safeguards:
Transport encryption:
Stored encryption:
SOC 2 certification:
ISO 27001 certification:
Signer authentication:
Mobile options for Cologuard orders
Use the signNow mobile app on iOS 15 or later or Android 10 or later to prepare and sign a Cologuard Order Form.
iPhone app iOS 15 or later with signNow mobile app Android app Android 10 or later with signNow app Mobile tools Camera capture and offline signing
Camera capture can digitize a paper Cologuard Order Form, while offline signing supports work without an active connection. Reconnect before sending or synchronizing the completed document, and use managed devices when the form contains protected health information.
Best practices for Cologuard orders
Accurate field review, controlled access, verified signer identity, and record reconciliation reduce errors when handling a Cologuard Order Form.
Review detected fields against the source
Verify the patient’s identity before sending
Limit access to authorized healthcare staff
Reconcile and archive the completed form
Privacy pitfalls in Cologuard workflows
Patient names, contact details, insurance information, or health-related content can be exposed when completed forms are downloaded to unmanaged devices or sent through ordinary email. Electronic consent may be incomplete if the patient cannot access the record, does not receive the required disclosure, or signs without understanding the transaction. Broad template or completed-document permissions can expose protected health information to staff who do not need access for the Cologuard workflow. A missing audit trail, unsigned field, or mismatched patient identity can make the completed order difficult to reconcile with the provider’s record.
Cologuard record retention schedule
Retention depends on whether the completed Cologuard Order Form contains protected health information, patient authorization, or related provider records.
Six years for HIPAA records
State period for provider records
Payer-required retention period
Authorization-specific retention period
Audit trail retention period
Cologuard Order Form troubleshooting
Resolve field, invitation, authentication, privacy, and plan questions before finalizing a Cologuard Order Form workflow.
Upload the original Cologuard Order Form and review signNow’s detected fields before sending. The Business plan includes templates and audit trails, allowing the sender to correct field placement without changing the form’s clinical or patient information.
Confirm the signer’s email address and resend the invitation from signNow. SMS OTP can add authentication, but the recipient still needs access to the signing link and the device must support the browser or mobile workflow.
Use signNow’s audit trail to review signer identity, timestamps, IP information, and recorded actions. The audit trail documents the electronic transaction but does not replace clinical review or provider authorization requirements.
A Cologuard Order Form containing protected health information requires appropriate administrative and technical safeguards. signNow identifies HIPAA compliance as requiring a BAA, so confirm that agreement and internal access controls before processing PHI.
Consumer-facing electronic records may require consent disclosures under ESIGN, including access to the electronic format and procedures for withdrawing consent. Confirm the healthcare organization’s disclosure process before sending the form electronically.
The Business plan is listed at $8 per user per month when billed annually and includes 100 signature invites per user per year. Additional plan limits, overages, or higher authentication needs should be checked before deployment.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.