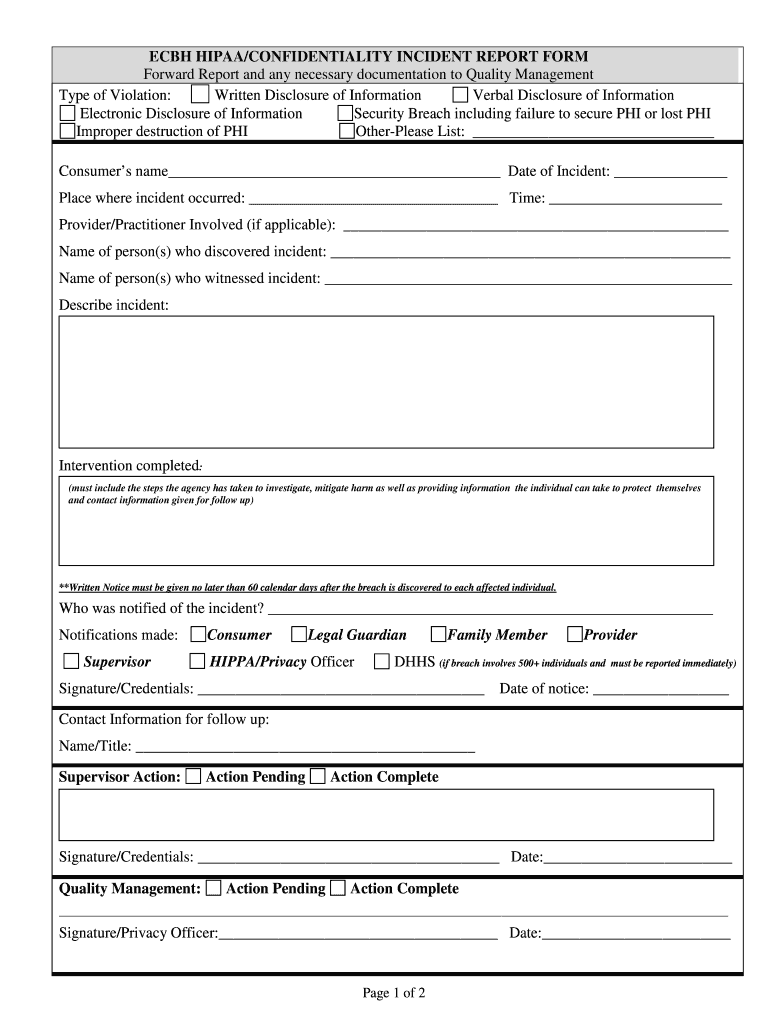
HIPAA Incident Report Form
Get a Hipaa Incident Report Form 0 template with airSlate SignNow and complete it in a few simple clicks.
What the HIPAA Incident Report Form does
A HIPAA Incident Report Form records what happened when protected health information may have been accessed, used, or disclosed improperly. It typically captures the incident date, people or systems involved, information affected, discovery details, containment actions, risk assessment, notifications, and corrective measures. A covered entity or business associate can complete the report, route assigned fields for review and signature, and preserve the final record. HIPAA requires certain documentation to be retained for six years from creation or the last effective date under 45 CFR 164.530(j).
Who uses the HIPAA incident report
Healthcare organizations
Covered entities and business associates use the report to document suspected PHI access, investigate the timeline, assign containment actions, and retain evidence for HIPAA privacy and security reviews.
Incident-response teams
Privacy officers, security teams, and incident managers use each report to coordinate reviewers, capture approvals, record notifications, and preserve a traceable decision history.
Who benefits from HIPAA incident reporting
Healthcare organizations use this form to turn suspected PHI incidents into documented investigations, assigned actions, and reviewable records.
Solo healthcare practices can document suspected PHI incidents, assign review fields, and retain signed reports without coordinating paper packets across offices. Hospital privacy teams can route incident details to investigators, security reviewers, and authorized signers while preserving a unified audit trail for each report. Enterprise health systems can connect signNow workflows to existing applications, apply role-based access controls, and standardize six-year documentation retention under HIPAA 45 CFR 164.530(j).
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the HIPAA report workflow works
The report moves from structured preparation to authorized review, signature, and controlled retention without losing its audit evidence.
Upload form: Upload the HIPAA Incident Report Form to signNow. Prepare fields: Auto-detect and review fields for incident details and approvals. Route report: Send assigned sections to authorized reviewers and signers. Preserve evidence: Complete, download, and retain the signed report with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How to complete the HIPAA incident report
Use signNow to prepare the report, assign its incident-response fields, collect signatures, and preserve the completed record with its audit trail.
Upload form:
Upload the HIPAA Incident Report Form to signNow. Review fields:
Let signNow auto-detect fillable fields, then review placements. Assign roles:
Assign each incident-response field to the correct signer. Send report:
Send the report for signature through the approved recipient channel. Archive record:
Store the signed PDF and audit trail together.
Recommended HIPAA report workflow setup
Configure the report workflow around signer identity, audit evidence, protected storage, and the six-year HIPAA documentation requirement.
| Setting | Recommendation |
|---|---|
| Authentication method | Use SMS OTP for elevated signer verification |
| Signature type | Use an electronic signature with documented intent |
| Audit trail | Export the completed audit trail with each report |
| Document retention | Retain six years under HIPAA 45 CFR 164.530(j) |
| Encryption | Use TLS in transit and AES-256 at rest |
What the HIPAA audit trail records
A signNow audit trail preserves technical evidence around each HIPAA Incident Report Form signing event, separate from the form setup process.
Authenticate signer:
Capture timestamp:
Hash document:
Seal history:
Log activity:
Export evidence:
Record-keeping practices for HIPAA reports
Retain the signed report, supporting evidence, and audit trail together so incident decisions remain traceable throughout the required record life.
Apply the six-year HIPAA retention rule
Export the audit trail with each report
Archive reports in restricted storage
Track dates and authorized destruction
HIPAA Incident Report Form retention schedule
Retain the report and related HIPAA documentation for the applicable six-year period, measured from creation or the last effective date under 45 CFR 164.530(j).
Six years for HIPAA documentation
Six years for response policies
Six years for workforce training
Six years for privacy notices
Six years from effective date
Privacy pitfalls in incident reporting
Including unnecessary patient identifiers in the HIPAA Incident Report Form increases exposure if the completed report is shared beyond the incident-response team. Failing to document the individual’s consent or authorization context can leave reviewers unable to explain why protected health information was disclosed. Assigning broad workspace permissions may allow staff without incident-response duties to view, download, or forward completed reports containing PHI. Sending a report to an unverified email address can disclose incident details before recipient identity and access requirements are confirmed.



Key features for HIPAA incident reports
signNow combines structured preparation, assigned fields, electronic signatures, and audit evidence for organizations documenting suspected PHI incidents.
Structured fields
Capture incident dates, affected information, involved systems, discovery details, and containment actions in one structured report for consistent review.
Role assignment
Assign investigation, privacy, security, and approval fields to the people responsible for completing each portion of the report.
Electronic signing
Send the HIPAA Incident Report Form for electronic signatures while preserving signer actions, timestamps, and completion history.
Audit evidence
Export the completed report with its audit trail so reviewers can connect the final document to its signing events.
Mobile access
Use signNow’s mobile apps to review or sign assigned report fields when authorized staff are away from a desktop.
Controlled retention
Retain the final report in controlled storage alongside supporting evidence, using HIPAA’s six-year documentation rule as the baseline.
Troubleshooting HIPAA incident reports
Resolve access, compliance, authentication, and retention questions by matching the report workflow to signNow plan features and applicable U.S. requirements.
SignNow’s Business plan includes audit trails, templates, and legally binding eSignatures at $8/user/month when billed annually. For a HIPAA workflow, confirm that a Business Associate Agreement is in place before handling protected health information.
HIPAA compliance requires a BAA with the covered entity or business associate arrangement; the platform’s HIPAA status alone does not create one. SignNow identifies HIPAA compliance as requiring a BAA, so complete that agreement before processing PHI.
If a signer cannot access the report, verify the recipient email, resend the invitation, or provide a controlled signing link. SMS-based authentication can add identity assurance, but the organization remains responsible for access procedures and PHI disclosure controls.
Business Premium adds bulk send, while Enterprise adds advanced signer authentication. If one incident report is sent at a time, Business may provide the required audit trail; select a higher plan only when its documented features are needed.
A completed form should preserve the signer’s intent, attribution, and record reproducibility. ESIGN and UETA recognize electronic signatures, but HIPAA privacy and security obligations still require appropriate access controls, retention, and a BAA.
The Business plan includes 100 signature invites per user per year, with overage fees. If your incident program exceeds that allowance, review the plan terms or Site License option rather than assuming subscription signing is uncapped.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.