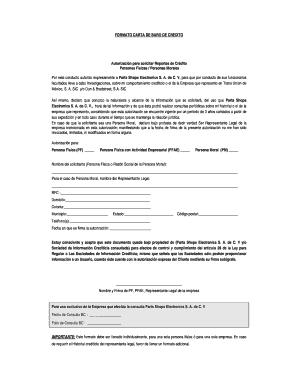
Formato Carta DE Buro DE Credito Autorizaci N Para
Use a FORMATO CARTA DE BURO DE CREDITO Autorizaci N Para template to make your document workflow more streamlined.
What this credit authorization letter does
Formato Carta DE Buro DE Credito Autorizaci N Para is an authorization letter used to document an individual’s permission for a named organization or recipient to request or review credit information. It is not a credit report and does not itself approve a loan, tenancy, or account. The sender should complete the parties, authorization scope, relevant dates, and signature details according to the organization’s approved form. With signNow, the sender uploads the letter, reviews detected fields, assigns the signer, sends it electronically, and retains the completed document with its audit trail.
Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

Who uses this authorization letter
Lenders and landlords
Credit-report authorization letters are used by lenders, landlords, employers, and service providers when an individual permits a named recipient to request or review credit information. The letter should identify the parties, scope, and date, then preserve the signer’s consent.
Screening departments
Consumer-facing teams can complete this authorization letter before underwriting, rental screening, or account review. signNow helps place signature fields, route the document, and retain the completed record, while the requesting organization remains responsible for lawful credit-report access.
Business types that use this form
This authorization letter is useful wherever an organization needs documented permission before requesting or reviewing an individual’s credit information.
Independent landlords can send a named credit-report authorization before evaluating a rental applicant, preserving the signed consent and audit history without arranging an office appointment. Regional lending offices can standardize authorization letters across branches, assign signing fields, and retain completed records for underwriting review and internal controls. Enterprise screening departments can route authorization letters through controlled workflows, use shared templates, and connect completed records with approved business systems.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How to complete the authorization letter
Complete the letter carefully, confirm the permitted recipient, and preserve evidence of consent after signing.
Upload document:
Upload the authorization letter and let signNow detect fillable areas. Check details:
Review names, dates, scope, and recipient information for accuracy. Place fields:
Add signer fields and specify the recipient or organization. Send securely:
Send the letter for electronic signature through signNow. Store record:
Download the completed letter and preserve its audit trail.
Recommended workflow setup
Use a controlled signing workflow that identifies the signer, records consent, protects personal information, and preserves the completed authorization letter.
| Setting | Recommendation |
|---|---|
| Signer authentication method | Email invitation with optional SMS verification |
| Authorization signature type | Typed, drawn, or click-to-sign signature |
| Credit letter audit trail | Enable completion history and certificate |
| Authorization record retention | Follow applicable state and industry policy |
| Encryption and user provisioning | Use encrypted storage with controlled access |
How the audit trail records consent
The audit trail links the signer’s actions, timestamps, and completed authorization letter so the organization can review the signing history.
Signer authentication:
Timestamp capture:
Document integrity:
Event logging:
Record retrieval:
Audit export:
Features for this authorization letter
signNow supports the document workflow from upload through signed-record retention, while the requesting organization remains responsible for lawful credit-information use.
Field detection
Upload the credit-report authorization letter and identify signature areas without rebuilding the document from scratch. Review detected fields before assigning them to the signer.
Assigned fields
Assign the signature, date, and other required fields to the correct participant so the authorization reflects the intended signer and recipient relationship.
Electronic routing
Send the authorization electronically instead of coordinating paper delivery, while maintaining a record of invitations, signing activity, and completion.
Audit trail
The completed letter remains connected to an audit trail documenting the signing sequence, timestamps, and actions associated with the authorization workflow.
Organized records
Store the signed authorization and completion evidence together so staff can retrieve the record when reviewing a credit-report request.
Reusable workflow
Business plans include legally binding eSignatures, templates, and audit trails, giving organizations a repeatable workflow for this specific authorization letter.
Security for signed credit authorizations
TLS 1.2/1.3 protects data:
AES-256 protects stored records:
SOC 2 Type II report available:
ISO 27001 certified controls:
GDPR and CCPA compliance:
ESIGN and UETA compliance:
Privacy and disclosure pitfalls
Including a full Social Security number or unnecessary account details can expose sensitive personal information beyond the stated credit-review purpose. A missing signature date or unclear recipient may make it difficult to establish when consent began and who was authorized to receive information. Sending the completed letter to every participant instead of designated recipients can disclose credit-related personal data unnecessarily. Failing to preserve the signed authorization and audit trail can weaken the organization’s ability to demonstrate consent during a later inquiry.
Best practices for credit authorizations
Careful field review, controlled access, and documented retention help keep this authorization letter usable as consent evidence.
Review every authorization field before sending
Restrict access to signed records
Preserve the audit trail with the letter
Set retention using applicable authority
Platform requirements for signing
Use signNow through Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides iOS and Android apps for reviewing and signing the authorization letter on supported mobile devices. Secure connections use TLS 1.2/1.3.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile apps iOS and Android signNow apps
Organizations should manage access through approved devices and accounts, particularly when the authorization contains personal information. Teams requiring centralized provisioning, integrations, or advanced controls should confirm the selected signNow plan, administrator permissions, and applicable privacy requirements before deployment.
Troubleshooting signed credit authorizations
Resolve delivery, field, consent, plan, and privacy questions before relying on a completed credit-report authorization letter.
If the signer cannot open the invitation, verify the email address, resend the request, or use a signNow signing link. The Business plan includes templates, audit trails, and legally binding eSignatures, but the recipient still needs access to the delivery channel.
If the letter has no visible signature field, reopen the document in signNow, review auto-detected fields, and add a signature field manually. Confirm that the field is assigned to the intended signer before sending the credit-report authorization.
If the recipient name is incorrect, cancel or correct the draft before signing. After completion, do not alter the signed authorization; create a corrected version and retain the original according to the organization’s record policy.
For consumer-facing electronic records, ESIGN requires disclosure of the right to receive paper records, access to electronic records, and procedures for withdrawing consent under 15 U.S.C. §7001(c). Obtain legal review before applying this workflow to regulated consumer transactions.
The Business plan is listed at $8 per user per month with annual billing and includes audit trails. It includes 100 signature invites per user annually; overage terms apply, so review plan limits before sending high-volume authorizations.
If the authorization involves protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. The authorization letter itself does not establish HIPAA compliance; configure the required agreement and organizational safeguards separately.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.