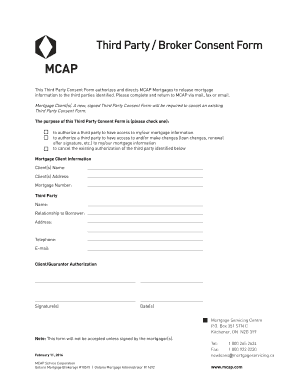
Mcap Third Party Broker Consent Form
Use a MCAP Third Party Broker Consent Form template to make your document workflow more streamlined.
What the Mcap consent form does
The Mcap Third Party Broker Consent Form records a person’s permission for a broker or other authorized third party to act, communicate, or access information for a defined transaction. The signer reviews the parties, scope, and conditions, then applies an electronic signature when the transaction permits electronic records. In signNow, upload the form, review or add fillable fields, assign the consenting party and broker, send the request, and store the completed PDF with its audit trail. ESIGN and applicable state electronic-transaction law can support business records, but state-specific requirements and document exclusions still control.
Who uses this broker consent form
Independent brokers
Independent brokers use the form to document a client’s permission for a third party to communicate, negotiate, or access transaction information. It can accompany brokerage agreements, consent forms, service contracts, and related disclosures while preserving a clear record of the authorized relationship.
Brokerage firms
Brokerage firms and transaction teams use the form alongside contracts, NDAs, invoices, and consent records. A completed document identifies the consenting party, authorized broker relationship, and signing evidence needed for organized handoffs between clients, brokers, lenders, and service providers.
Key features for broker consent records
Mcap Third Party Broker Consent Form workflows combine structured authorization, signer routing, audit evidence, and controlled storage for broker-related transactions.
Reusable template
Upload the Mcap form and place required fields for the consenting party, broker, dates, and acknowledgments. A reusable template reduces omissions when the same authorization process serves multiple transactions.
Signer routing
Assign the consent to the correct signer and control the signing order when broker, client, or internal review must happen sequentially. Recipient-specific fields help keep authorization details attached to the right person.
Audit trail
Collect a signature with an electronic record showing signing activity, timestamps, and document history. This creates a more reviewable record than exchanging unsigned attachments through separate email threads.
Signer access
Use email delivery, SMS authentication, or a signing link according to the transaction’s identity and access requirements. The selected method can reduce misdirected consent requests and clarify who received the form.
Secure storage
Store the executed consent and completion evidence with the related broker file. Centralized retrieval helps teams answer which party authorized the relationship and when the consent was completed.
Business integrations
Connect completed consents to Salesforce, Microsoft Dynamics 365, NetSuite, Google Drive, Box, or other supported systems. The connection can reduce manual downloading and duplicate data entry.
How to complete the broker consent form
Follow this sequence to prepare the Mcap consent, route it to the intended parties, and preserve the completed authorization record.
Upload form:
Upload the completed Mcap form. Check fields:
Review detected fields and add missing ones. Assign signers:
Assign each field to the correct signer. Send request:
Send the consent request by email or link. Store evidence:
Review the signed PDF and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended consent workflow setup
Configure the Mcap workflow around verified recipients, clear authorization, preserved evidence, and controlled access to completed broker records.
| Setting | Recommendation |
|---|---|
| Authentication method | Email delivery with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps and action history |
| Document retention | Keep signed PDF with audit trail |
| User provisioning | Assign controlled roles and permissions |
Platform requirements for Mcap forms
Open the Mcap consent in Chrome, Firefox, Safari, or Edge over TLS 1.2 or 1.3. signNow mobile apps support iOS and Android for reviewing and signing documents, subject to current app requirements.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows 10+, macOS 12+ Mobile systems iOS 15+, Android 10+
Organizations using managed Windows 10, macOS 12, iOS 15, or Android 10 devices should apply current security updates and control access to downloaded consent records. Enterprise deployments may also configure SSO, API access, and managed permissions where the selected signNow plan supports them.



Security for signed consent records
Transport encryption:
Stored encryption:
Security certification:
Information security:
Electronic signatures:
Health information:
Inside the Mcap audit trail
The audit trail records technical evidence around the Mcap consent rather than replacing the form’s authorization language or signer review.
Authenticate signer:
Timestamp action:
Hash document:
Seal record:
Export trail:
Review archive:
Privacy and disclosure pitfalls
The form may expose names, contact details, transaction data, or account information when shared with an unauthorized broker or recipient. Broad consent language may not show what the signer authorized, making later disputes about scope harder to resolve. Sending the form to a shared mailbox can weaken signer attribution and prevent reliable proof of who approved the broker relationship. Unrestricted access to completed consents can expose personal information beyond the employees handling the transaction.
Best practices for this consent form
Accurate parties, clear authorization language, and preserved signing evidence make the Mcap consent workflow easier to review and administer.
Review every authorization field
Verify signer identity before sending
Describe the authorized activity clearly
Archive the signed record securely
Legal standing of broker consent
For a qualifying business transaction, the Mcap consent can be an electronic record under ESIGN, 15 U.S.C. chapter 96, and applicable state law such as UETA when the signer demonstrates intent, consents to electronic records, and the record remains reproducible. Wills, certain court filings, and family law decrees are excluded.

Key performance indicators that demonstrate SignNow's proven track record.
Mcap consent form troubleshooting
Resolve field, signer, legal-validity, and record-preservation questions before relying on a completed Mcap broker consent.
Upload the original Mcap PDF again, then inspect signNow’s detected fields before sending. Add missing signature, date, or consent fields manually and assign each one to the intended recipient. Automatic detection does not replace a page-by-page review of this form.
Use the signNow Business plan for legally binding eSignatures, templates, and audit trails at $8 per user per month when billed annually. If the workflow requires bulk send, Business Premium is listed at $15 per user per month annually.
Confirm the email address and resend the Mcap request from the document’s recipient controls. If identity assurance matters, add SMS authentication and verify the signer’s phone number before delivery. Do not substitute a shared mailbox for the consenting party’s address.
ESIGN and UETA support electronic records when intent, consent, attribution, and record retention are demonstrated. For a consumer-facing transaction, provide the required electronic-record disclosure under 15 U.S.C. §7001(c), including paper-record access information.
signNow records signing activity in an audit trail, including timestamps and action history. After completion, download the signed PDF and audit trail together, then apply the transaction’s retention and access policy rather than relying only on the platform account.
Do not use electronic signing alone when the transaction actually requires a notary, witness, in-person appearance, or a document excluded by ESIGN. Wills, certain court filings, and family law decrees remain outside the federal electronic-signature framework.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.