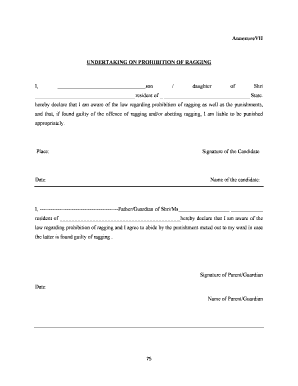
Prohibition Of Ragging Form
Use a Prohibition Of Ragging template to make your document workflow more streamlined.
What the Prohibition Of Ragging Form does
The Prohibition Of Ragging Form is a written acknowledgment that sets out an institution’s prohibition on ragging and records the signer’s agreement to follow that rule. In U.S. education settings, the institution determines the form’s required statements, signer groups, and submission process. With signNow, an administrator uploads the form, places or detects fillable fields, identifies the student or other signer, and sends the document electronically. The signer reviews the notice, completes required fields, signs, and receives a completed copy while signNow preserves the transaction history.
Who uses the Prohibition Of Ragging Form
Higher education
Universities and colleges can send the form to enrolled students, collect acknowledgments, and retain signed records for institutional conduct programs.
Student affairs
Student-affairs offices can route forms to students, parents, or staff, while preserving signer identity, timestamps, and the completed document.
How the form workflow works
The signNow workflow follows the institution’s approved form, signer list, and record policy from preparation through archival.
Upload: Upload the institution’s form Prepare: Detect or place required fields Route: Send to each designated signer Archive: Store the completed record
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended workflow configuration
Use a controlled configuration that connects signer identity, the approved form version, electronic consent, and the retained Audit Trail.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS 2FA |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable signNow Audit Trail export |
| Document retention | Follow institutional records policy |
| Encryption | TLS 1.2/1.3 and AES-256 |
What the Audit Trail records
The Audit Trail documents the signing events that connect a student’s identity, actions, timestamps, and completed acknowledgment.
Authenticate signer:
Capture timestamp:
Record document history:
Seal transaction:
Retrieve records:
Export evidence:
Platform requirements for online completion
Complete the Prohibition Of Ragging Form through signNow using Chrome or Firefox on Windows, Safari on macOS, or Chrome on Android.
Desktop browsers Chrome and Firefox on Windows 10 or later Apple desktop Safari on macOS 12 or later Android access Chrome on Android 11 or later
Organizations should use managed Windows, macOS, iOS, or Android devices with current security updates. Browser access requires TLS 1.2 or newer. Administrators should also confirm network access, identity controls, and retention policies before distributing the form to students or staff.
Security for signed acknowledgments
Encryption:
Independent assurance:
Information security:
Health information:
U.S. eSignatures:
Signer verification:
Privacy and disclosure pitfalls
Leaving the institution’s conduct policy version unstated can make it difficult to identify which prohibition a signer acknowledged. Collecting a student’s signature without documenting electronic consent may weaken evidence that the signer agreed to transact electronically. Sending completed acknowledgments to unrestricted folders can expose student names, signatures, or disciplinary information to unauthorized viewers. Using a shared link without identity controls can make it difficult to attribute a signed Prohibition Of Ragging Form to the correct student.
Retention and record-keeping practices
Preserve the signed acknowledgment, its Audit Trail, and the exact template version under the institution’s approved records policy.
Export the signed form and Audit Trail
Apply the appropriate retention schedule
Use controlled archival storage
Preserve the issued template version
Troubleshooting the signing workflow
Resolve field, identity, consent, plan, and retention questions before distributing the Prohibition Of Ragging Form.
Upload the institution-approved PDF into signNow, then review automatically detected fields before sending. If a field is missing, add it manually and assign it to the student or administrator responsible for completing that specific part.
Use signNow’s email delivery or a controlled signing link, and verify the student’s identity before release. For stronger assurance, configure two-factor authentication or SMS verification when the institution’s policy requires it.
signNow supports legally binding electronic signatures and audit trails under its ESIGN and UETA compliance features. The institution must still establish intent, obtain electronic consent where required, and retain a reproducible record.
The Business plan includes templates, audit trails, and mobile apps. Business Premium adds bulk send and kiosk mode, which can help an institution distribute the same acknowledgment to many students or collect signatures at an event.
Export the completed Prohibition Of Ragging Form together with its signNow Audit Trail and preserve the matching template version. Access controls should limit retrieval to authorized student-affairs, compliance, or records personnel.
A consumer-facing electronic record requires disclosure of the right to paper, proof of electronic access, and a withdrawal process under 15 U.S.C. §7001(c). Review whether that rule applies before sending the form to a consumer signer.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.