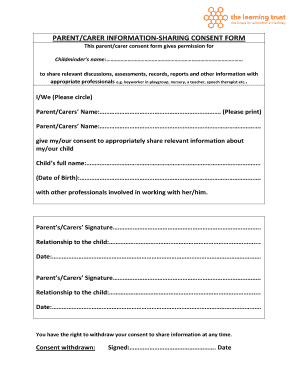
Consent To Share Information
Use a Consent To Share Information Template template to make your document workflow more streamlined.
What Consent To Share Information does
Consent To Share Information is a written permission record that identifies what information may be disclosed, to whom, and for what purpose. In a U.S. workflow, the signer reviews those limits, confirms consent, and signs the document before the recipient releases or receives covered information. Healthcare organizations may use it with HIPAA privacy procedures, while schools and other organizations may apply FERPA or state privacy rules when relevant. signNow lets a sender upload the form, place fields, invite the signer, capture the signing event, and retain the completed record with its audit trail.
Who completes this consent form
Healthcare disclosures
Healthcare organizations use this form to document patient permission before disclosing protected health information to named providers, caregivers, insurers, or representatives. The form should identify the information covered, recipient, purpose, and any expiration or revocation terms required by the organization’s HIPAA procedures and applicable state law.
Regulated information
Legal, education, financial, and nonprofit organizations use this form when a person authorizes release of records to a named third party. The sender should match the consent language to the applicable privacy rule, limit access to the stated purpose, and preserve the signed record for later review.
Business types that use information consents
Consent To Share Information is most useful where authorization, privacy, and proof of signer intent must remain connected to each disclosure.
Solo healthcare practices use signed patient authorizations to document permission before sharing records with specialists, insurers, or family members, while preserving the completed consent form and audit trail. Regional legal firms use information-release consents to obtain client permission before sending case materials, medical records, or financial documents to opposing counsel and outside experts. Enterprise healthcare networks use standardized consent templates, role-based access, and centralized audit trails to coordinate disclosures across clinics while supporting HIPAA-governed information-sharing workflows.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the consent workflow works
The process connects the consent language, signer identity, electronic signature, and retained evidence in four controlled stages.
Upload: Upload the form Prepare: Detect fields Send: Invite signer Complete: Store evidence
What the consent audit trail records
A signNow audit trail provides technical evidence around the Consent To Share Information signing event rather than replacing the form’s substantive disclosure limits.
Authenticate signer:
Capture timestamps:
Protect document:
Log actions:
Review scope:
Export evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Choose the right signing method
- Use the signNow web app when an administrator prepares the consent form, places fields, assigns recipients, and needs a complete browser-based record of the transaction.
- Use the signNow mobile app when a clinician, caseworker, or client must review and sign Consent To Share Information from an iOS or Android device.
- Use kiosk mode when people sign at a staffed clinic or office, with the organization controlling the device and presenting the consent form directly.
- Use a shareable signing link when a designated recipient needs secure access without a separately addressed email invitation, while retaining the completed form and audit trail.
Features that support consent records
Consent To Share Information workflows benefit from connected fields, signer verification, audit evidence, reusable templates, and controlled record handling.
Assigned fields
Signer fields connect the person’s name, signature, initials, and date to the exact Consent To Share Information authorization being executed.
Mobile access
A signer can review and complete the consent from a browser or mobile device without returning a paper copy to the sender.
Audit trail
The audit trail preserves delivery, access, signing, and completion events so the organization can investigate how authorization was obtained.
Reusable templates
Templates help healthcare or legal teams reuse approved consent language while reducing manual field placement for each new disclosure.
Signer verification
Authentication options let the sender match the signing experience to the sensitivity of medical, educational, financial, or legal information.
Record control
Completed consent records can be retained with related workflow evidence, supporting controlled retrieval during privacy or compliance reviews.
Security for consent information
Stored data:
Data transfer:
Health information:
Control assurance:
Security management:
U.S. eSignatures:



Mobile options for consent signing
signNow mobile apps support Consent To Share Information workflows on iOS and Android. A sender can prepare or route the form from a mobile device, while a signer can review assigned fields and complete the authorization without relying on a desktop browser.
Mobile apps iOS and Android Limited connectivity Offline signing Document intake Camera capture
Organizations should manage mobile access through approved devices, user permissions, and privacy procedures. Camera-based capture can help digitize a paper consent before field placement, while offline signing availability should be confirmed for the specific workflow and device. Sensitive records should synchronize only through controlled accounts and approved storage.
Best practices for signed consents
Accurate scope, appropriate authentication, controlled access, and authority-based retention make Consent To Share Information easier to administer and defend.
Define the disclosure precisely
Match verification to risk
Preserve authorization evidence
Control access after signing
Privacy pitfalls to prevent
A broad authorization may fail to identify the records, recipient, or purpose clearly enough for a privacy officer to approve the requested disclosure. Sending a completed consent form to the wrong email address can expose medical, educational, financial, or legal information beyond the signer’s stated permission. A missing signature date, expiration term, or revocation procedure can make it difficult to determine whether the authorization remained effective when disclosure occurred. Unrestricted template access can let an unapproved user change recipient or disclosure language without the review required by organizational privacy controls.
Processing stages for consent forms
Consent To Share Information has no single federal signing deadline; processing depends on document readiness, signer response, and the applicable disclosure policy.
Prepare document
Deliver to signer
Signer turnaround
Complete and archive
Consent workflows in practice
Healthcare and legal teams use specific consent language, named recipients, and retained evidence when information must move beyond the original organization.
Healthcare operations
Fertility Centers of Illinois needed a dependable way to collect sensitive patient-related signatures and manage documents across its healthcare operations.
- Patient authorization workflows
- Secure electronic signing
- API-supported document handling
John Butler, founder of Fertility Centers of Illinois, said the organization valued signNow’s responsive team and API. For a Consent To Share Information workflow, that combination can connect patient authorization collection with downstream systems while keeping the signed record and signing evidence available for controlled review.
Legal disclosure
A regional law practice can use a consent template when clients authorize release of medical or financial records to a named expert or opposing counsel.
- Named recipient fields
- Purpose-specific authorization
- Exportable signing evidence
The practice should tailor the document’s scope to the specific matter rather than rely on a broad release. signNow can route the prepared consent for signature, capture the signing history, and preserve the completed authorization for the case file, subject to the firm’s retention and access policies.
Consent form troubleshooting questions
Resolve field, authentication, legal-effect, and retention questions before sending Consent To Share Information for signature.
Upload the original Consent To Share Information form and use signNow’s field placement tools to add signer, date, initials, and acknowledgment fields. Review every field before sending because missing limits or recipient details can weaken the authorization.
Business includes legally binding eSignatures, templates, audit trails, and mobile apps at $8/user/month when billed annually. Business Premium adds bulk send and costs $15/user/month annually. The selected plan should match volume, authentication, and team requirements.
For healthcare disclosures, signNow states that HIPAA compliance requires a business associate agreement. The organization must also define the information, recipient, purpose, and expiration or revocation process required by its privacy policy and applicable law.
A consent form can be signed electronically when the signer demonstrates intent, consents to the electronic transaction, can be identified, and the record remains accurate and reproducible. ESIGN and applicable UETA rules support electronic records, subject to statutory exclusions.
Use signNow’s signer authentication options, including SMS verification where appropriate, then confirm the signer’s email and access details. Stronger authentication may be appropriate when the consent authorizes sensitive medical, financial, or educational information.
Export and preserve the completed document with its audit trail, including signing timestamps and action history. HIPAA-covered records generally require six years from creation or the last effective date under 45 CFR §164.530(j), while organizational policy may require longer.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.