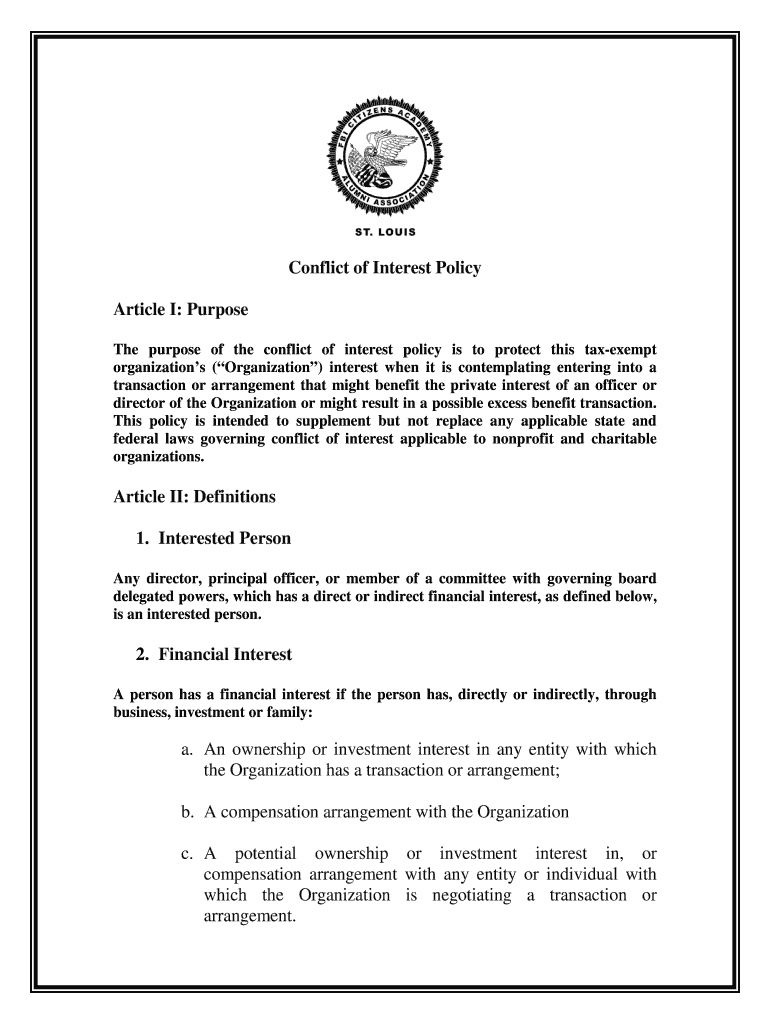
Nonprofit Conflict Of Interest Policy For 501C3 Form
Use a Sample Nonprofit Conflict Of Interest Policy Template For 501c3 template to make your document workflow more streamlined.
What this nonprofit policy records
A Nonprofit Conflict Of Interest Policy For 501C3 Form records whether directors, officers, or key participants disclose financial interests and follow the organization’s recusal and approval procedures. It is a governance document, not an IRS exemption application or a universal federal filing. The organization approves its wording, identifies required signers, and collects acknowledgments through a controlled process. With signNow, an administrator uploads the policy, reviews detected fields, assigns signers, sends it, and stores the completed document with its audit trail. State law, bylaws, grant terms, and board policy determine additional requirements.
Which nonprofit organizations benefit most
Organizations use this policy to document disclosures, abstentions, approvals, and annual acknowledgments across their governance structure.
Small charitable organizations can use a reusable policy template to collect annual director and officer disclosures, record recusals, and preserve signed acknowledgments without coordinating paper packets. Regional nonprofit networks can share an approved policy template across chapters while delegating sending to local administrators, preserving consistent language and centralized completion records for board reviews. Large nonprofit enterprises can route conflict disclosures through departments, use role-based permissions, and connect completed policies to governance records while maintaining an auditable signing history.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How nonprofit teams manage policy access
Board administrators can maintain a reusable conflict-of-interest policy template, assign signing roles, restrict editing permissions, and delegate sending to authorized staff. Shared templates help chapters or committees collect consistent disclosures without allowing every user to change the approved policy language. Nonprofit operations teams can use role-based access, signer routing, and completion tracking for directors, officers, and key employees. Administrators retain control of templates and audit records while delegated senders distribute the approved policy to the correct participants.
How to complete the policy online
Prepare the approved nonprofit conflict-of-interest policy, place the required acknowledgment fields, and preserve the completed record with its audit trail.
Upload policy:
Upload the approved policy PDF to signNow. Check fields:
Review detected fields and add missing signer fields. Assign roles:
Assign the board, officer, or employee signer roles. Send and track:
Send the policy and monitor completion status. Store records:
Download the signed policy and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
A signNow audit trail helps connect the nonprofit policy acknowledgment to signer activity, timestamps, document history, and the exported completion record.
Authenticate signer:
Capture timestamp:
Link document:
Seal record:
Review events:
Export history:
Recommended policy workflow setup
Use a controlled template, verified signer access, and a reproducible record for each nonprofit policy acknowledgment.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export completed certificate and activity log |
| Document retention | Three years from filing for tax records |
| Encryption | TLS 1.2/1.3 and AES-256 |
Features for nonprofit policy acknowledgments
signNow organizes the nonprofit policy cycle from approved template through signed record, helping governance teams document disclosures and acknowledgments consistently.
Document preparation
Upload the organization’s approved conflict-of-interest policy and prepare it without recreating the document. Auto-detected fields can reduce manual placement work before the board or staff acknowledgment cycle begins.
Role assignment
Assign directors, officers, employees, or committee members to defined signing roles. Routing keeps each acknowledgment connected to the correct person and reduces uncertainty about who must complete the policy.
Electronic signing
Collect typed or drawn signatures with recorded intent and signer activity. The completed policy provides a clearer governance record than an untracked email attachment or paper acknowledgment.
Audit evidence
Capture timestamps, signer actions, and delivery information in the audit trail. Exporting that history with the signed policy supports later board, grant, or internal compliance review.
Reusable templates
Reuse the approved template for annual disclosures and policy renewals. Version control helps prevent staff from circulating superseded conflict-of-interest language to directors or officers.
Mobile access
Complete acknowledgments from desktop or mobile devices when participants are distributed across locations. signNow supports mobile apps alongside its web workflow for nonprofit governance processes.


Retention periods for policy records
No single federal period governs every nonprofit conflict-of-interest policy; match retention to the underlying tax, governance, grant, and state-law record requirements.
Three years for tax records
Six years for major understatement
Indefinite records for fraud
State-law period may be longer
Policy schedule set by organization
Security for signed policy records
Data in transit:
Stored documents:
Security controls:
Information security:
Electronic signatures:
Sensitive records:
Pricing and workflow comparison
signNow pricing and included policy workflow features are shown alongside competitor values that are not verified in the available vendor data.
| Features | signNow | DocuSign | Adobe Sign | PandaDoc | Dropbox Sign |
|---|---|---|---|---|---|
| Starting price | $8/user/month annually | Not verified | Not verified | Not verified | Not verified |
| Free trial | 7 days, no credit card | Not verified | Not verified | Not verified | Not verified |
| Bulk send | Business Premium included | Not verified | Not verified | Not verified | Not verified |
| Audit trail | Included in Business | Not verified | Not verified | Not verified | Not verified |
| Unlimited users | Included on paid plans | Not verified | Not verified | Not verified | Not verified |
Privacy and disclosure pitfalls
Personal addresses, financial interests, or related-party details can be exposed when the policy is distributed without restricted access or careful document permissions. A signer may acknowledge the policy without clearly disclosing the transaction, relationship, financial interest, or required recusal information requested by the organization. Using an outdated template can omit newly approved board procedures, definitions, approval thresholds, or annual acknowledgment language required by the nonprofit’s governance policy. Emailing signed PDFs without the audit trail can make it harder to establish signer attribution, completion timing, and the exact policy version acknowledged.
Questions about completing this policy
These answers address field preparation, electronic-signature requirements, plan selection, evidence preservation, and protection of nonprofit policy records.
Upload the original policy PDF again and inspect whether fields are flattened, protected, or image-based. signNow can detect fillable areas, but a scanned policy may require manually placing signature, date, disclosure, and acknowledgment fields before sending.
The Business plan includes legally binding eSignatures, audit trails, templates, and mobile apps at $8/user/month when billed annually. Business Premium adds bulk send at $15/user/month annually, which can help distribute the same policy to many recipients.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are established. For a consumer-facing electronic record, review the ESIGN disclosure requirements in 15 U.S.C. §7001(c) before collecting consent.
Use signNow’s signer routing and role assignments to identify the director, officer, employee, or committee member responsible for each acknowledgment. If a conflict requires recusal or board approval, record that action in the organization’s governance process as well.
Export the completed policy and audit trail together, then store them in a restricted governance archive. The record should preserve the approved policy version, signer identity, completion date, and related board or committee documentation.
For sensitive nonprofit records, signNow provides TLS 1.2/1.3 encryption in transit, AES-256 encryption at rest, SOC 2 Type II certification, and ISO 27001 certification. Apply organization-specific access controls and retention rules to the exported records.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.