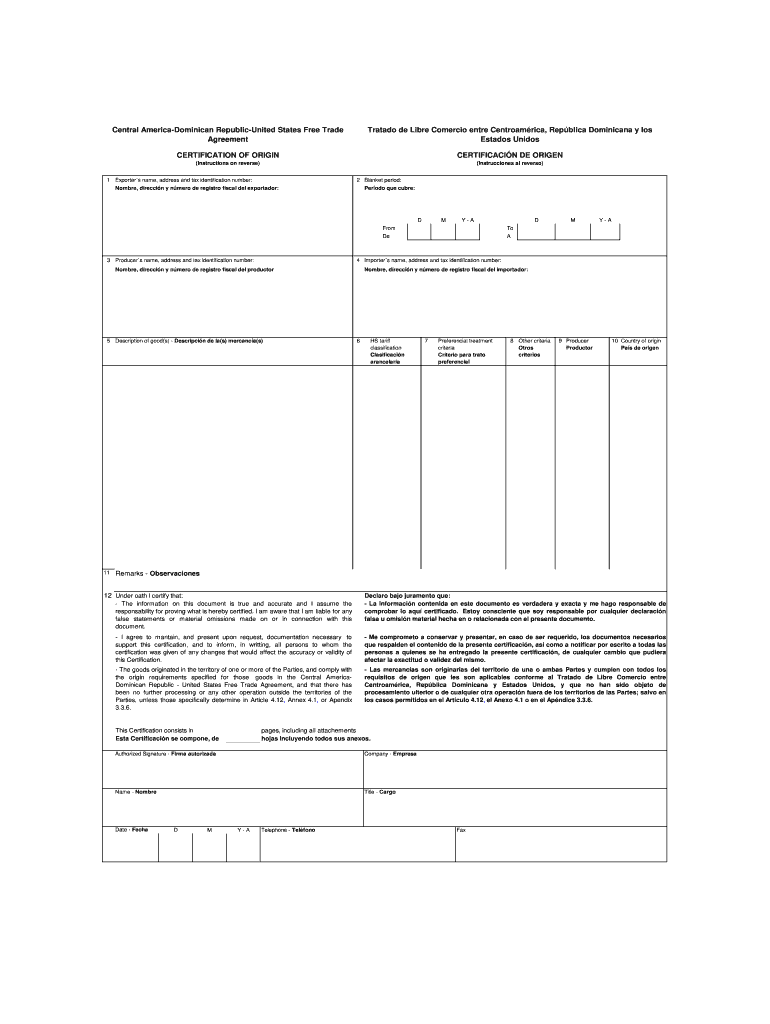
Certificado DE Origen Cafta Dr Cetrex Form
Use a Certificado De Origen CAFTA DR Cetrex template to make your document workflow more streamlined.
What this certificate form does
Certificado DE Origen Cafta Dr Cetrex Form is a trade document used to record origin information for a CAFTA-DR transaction. In signNow, the sender uploads the certificate, reviews automatically detected fillable fields, assigns the appropriate exporter, producer, or importer signers, and sends the document for electronic completion. SignNow preserves the signed PDF and audit trail, supporting evidence of intent and attribution under ESIGN and applicable state law. The completed record does not itself replace customs filing, supporting proof, or agency-specific requirements.
Who uses this certificate workflow
Exporters and trade teams
Exporters and trade teams can use the certificate workflow to collect transaction details, signatures, and supporting acknowledgments in one controlled record. Contracts, NDAs, HR forms, invoices, and consent forms may also be completed in signNow, but each document still follows its own legal and operational requirements.
Commercial operations
Manufacturers, distributors, brokers, and compliance staff can route certificates to authorized signers, preserve completion evidence, and share the final record with internal reviewers. The same workflow handles related commercial documents, provided the sender confirms which parties must sign and which agency or customer receives the document.
How to complete the certificate
Use signNow to prepare the certificate, assign its authorized signers, and preserve the completed document with execution evidence.
Upload:
Upload the certificate PDF. Check fields:
Review detected fillable fields. Add signers:
Assign authorized signers. Send:
Send the signing request. Store:
Download the completed record.
Recommended certificate workflow setup
Configure certificate signing around verified signer identity, documented intent, audit evidence, and the retention rule governing the transaction.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Export with every completed certificate |
| Document retention | Apply the transaction-specific written policy |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How this certificate workflow works
The signNow process turns the certificate into a controlled signing workflow while leaving CAFTA-DR eligibility and official submission duties with the responsible trade parties.
Upload document: Upload the certificate PDF to signNow. Review fields: Auto-detect fields, then correct missing assignments. Request signatures: Send the certificate to authorized signers. Preserve evidence: Store the signed certificate and audit trail.
Certificate preparation and signing stages
The certificate workflow has four operational stages; no universal signer deadline is established in the supplied records, so parties should set one contractually.
Prepare the certificate
Deliver to signers
Complete signer review
Archive the record
Recordkeeping practices for signed certificates
Retain the completed certificate with its audit evidence, applying the underlying transaction rule rather than an unsupported universal period.
Apply the correct retention period
Export the audit trail
Archive signed certificates securely
Reconcile records periodically
What the certificate audit trail records
The audit trail separates the certificate’s business content from evidence showing who accessed, signed, and completed the document.
Authenticate signer:
Capture timestamp:
Record document history:
Seal completion:
Retrieve record:
Export evidence:
Signer authentication and certificate security
PKI support:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Audit trail:
Certificate privacy and disclosure pitfalls
Exporter and importer details can be exposed when completed certificates are emailed without access controls or shared with unintended recipients. Missing signer consent or unclear electronic-record disclosures can weaken evidence that each party intended to sign digitally. Incorrect role permissions may let an unauthorized team member edit certificate fields or send the document before compliance review. Storing the signed certificate without its audit trail can make later verification of signer identity, timestamps, and document history more difficult.
State rules and document exclusions
State law may require notarization
ESIGN exceptions exclude wills
Certain decrees remain excluded
State recording rules may apply



Troubleshooting certificate completion
Resolve certificate workflow issues by checking field accuracy, signer access, plan capabilities, authentication, and the distinction between signing and official submission.
Upload the original certificate as a PDF and inspect the detected fields before sending. signNow’s editor lets you place or correct text, date, checkbox, and signature fields; verify exporter and importer details manually because field detection cannot validate CAFTA-DR eligibility.
The Business plan includes templates, audit trails, mobile apps, and legally binding eSignatures at $8/user/month with annual billing. If this certificate must be sent to many signers, Business Premium adds bulk send at $15/user/month annually.
A signNow audit trail records signing activity, timestamps, and document history, supporting evidence of intent and attribution. For U.S. transactions, ESIGN under 15 U.S.C. chapter 96 and UETA provide the relevant legal framework, subject to applicable document exceptions.
If a signer cannot open the invitation, resend it or generate a signNow quick invite link when available on the selected plan. Confirm the recipient address, browser access, and required authentication method before changing the certificate fields.
A certificate containing business or personal information should use controlled access and an appropriate authentication method. signNow supports two-factor authentication options, while HIPAA workflows require a business associate agreement when protected health information is involved.
Do not use this workflow to replace a government filing, customs submission, notarization, or other requirement imposed by the applicable authority. signNow can complete and retain the document, but the exporter remains responsible for CAFTA-DR eligibility and submission rules.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.