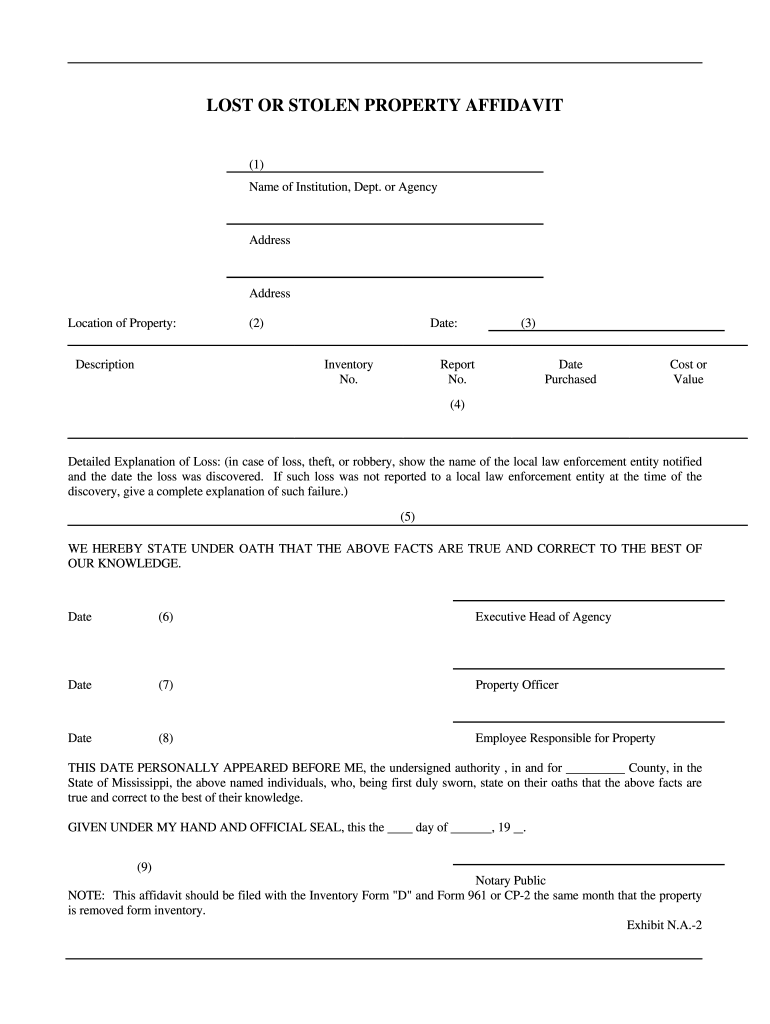
Affidavit Of Theft Form
Automate complex legal workflows with a Affidavit Of Theft 0 template.
What the affidavit records
An Affidavit Of Theft Form is a signed statement describing an alleged theft and the declarant’s knowledge of the relevant facts. It commonly identifies the person making the statement, the affected property or account, the incident details, and the declarant’s signature. With signNow, upload the form, allow fillable fields to be detected, review each entry, send it to the intended signer, and retain the executed document with its audit trail. State law or a receiving organization may require notarization or additional evidence.
Complete and sign the affidavit accurately
signNow helps organize the Affidavit Of Theft Form, collect the declarant’s signature, and preserve evidence of how the statement was completed.
Field detection
Upload the Affidavit Of Theft Form and let signNow detect fillable areas, reducing manual field placement before you enter statement details and signer information.
Guided completion
Add names, dates, addresses, and item descriptions directly to the affidavit while keeping the document organized for review and signature.
Remote sending
Send the completed Affidavit Of Theft Form to the declarant or authorized signer by email without printing or scanning separate copies.
Audit trail
Capture the signer’s intent, authentication events, timestamps, and actions in an audit trail connected to the signed affidavit record.
Reusable template
Use templates when your organization repeatedly prepares theft affidavits with the same fields, clauses, routing order, and approval requirements.
Record storage
Store the completed affidavit and certificate of completion together so reviewers can connect the signed statement with its execution history.
Legal standing of the affidavit
An Affidavit Of Theft Form records a declarant’s facts and signature; its evidentiary weight depends on accuracy, attribution, and applicable state requirements. ESIGN and UETA generally recognize electronic signatures for covered transactions, but they exclude wills, certain court orders, and family-law decrees.

How the affidavit workflow works
The signNow workflow moves the Affidavit Of Theft Form from an uploaded document to a signed, reviewable record.
Upload: Upload the Affidavit Of Theft Form. Complete: Confirm detected fields and add details. Send: Send it to the declarant. Archive: Store the signed record and trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended affidavit workflow setup
Configure the Affidavit Of Theft Form around signer identity, factual accuracy, audit evidence, and controlled record retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email invitation with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps and signer actions |
| Document retention | Follow the matter’s documented policy |
| Encryption | Use TLS 1.2/1.3 and AES-256 |
Inspect the affidavit audit trail
The audit trail records execution evidence separately from the affidavit’s factual statements, helping reviewers evaluate how the signed record was created.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper evidence:
Action history:
Trail export:
Authenticate the affidavit signer
PKI signatures:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Evidence trail:
Platform requirements for signing
Complete the Affidavit Of Theft Form in Chrome, Firefox, Safari, or Edge on Windows 10 or macOS 12 and later environments. signNow mobile apps support iOS 15 and Android 11 for reviewing and signing the affidavit.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows 10, macOS 12 Mobile apps iOS 15, Android 11
Organizations handling sensitive theft statements should manage Windows, macOS, iOS, and Android devices through approved controls, restrict downloads, and verify recipient access. Teams using API, SSO, or certificate-based signing should confirm the selected signNow plan and configure those controls before production use.
Preserve the affidavit as reliable evidence
Retention and handling should reflect the theft matter, the people named in the affidavit, and any state-law or organizational recordkeeping requirement.
Set a documented retention period
Export the audit trail
Separate executed records from drafts
Restrict disclosure and access
Check state-specific requirements
State notarization
Wills and codicils
Court orders
Real-estate deeds
Family-law decrees
Avoid privacy and disclosure errors
Including unnecessary Social Security numbers, account credentials, or medical details can expose personal data beyond what the theft recipient needs. Sending an affidavit to the wrong recipient can disclose allegations, identifying information, or incident details without authorized consent. Failing to preserve the completion certificate and audit trail can weaken the record’s ability to show who signed and when. Using a template without reviewing incident dates, property descriptions, and declarant information can create factual inconsistencies in the executed affidavit.
Resolve Affidavit Of Theft Form issues
These answers address field placement, signer identity, legal recognition, plan capabilities, access, and sensitive information handling for this affidavit workflow.
On the Business plan, upload the Affidavit Of Theft Form, place or confirm fields, and assign the signer before sending. If detected fields are misplaced, adjust them manually and verify every statement field before delivery.
The Business plan includes legally binding eSignatures and audit trails. ESIGN and UETA generally support electronic signatures when intent, consent, attribution, and record retention requirements are satisfied; state-specific rules can still affect an affidavit’s use.
Use SMS OTP or another available authentication method when the recipient’s identity needs stronger evidence than an email link. Advanced signer authentication is associated with Enterprise capabilities, so confirm plan availability before configuring the workflow.
A signer can often complete the Affidavit Of Theft Form without a signNow account by opening the invitation. If access fails, confirm the email address, resend the invitation, or provide a shareable signing link through an approved channel.
Business Premium includes bulk send, but one theft affidavit should still be reviewed for matter-specific facts before delivery. Use bulk send only for genuinely identical documents and verify each recipient and statement before sending.
If the affidavit contains protected health information, signNow identifies HIPAA compliance as requiring a BAA. Confirm that the organization has the required BAA and apply access controls before collecting or sharing the record.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.