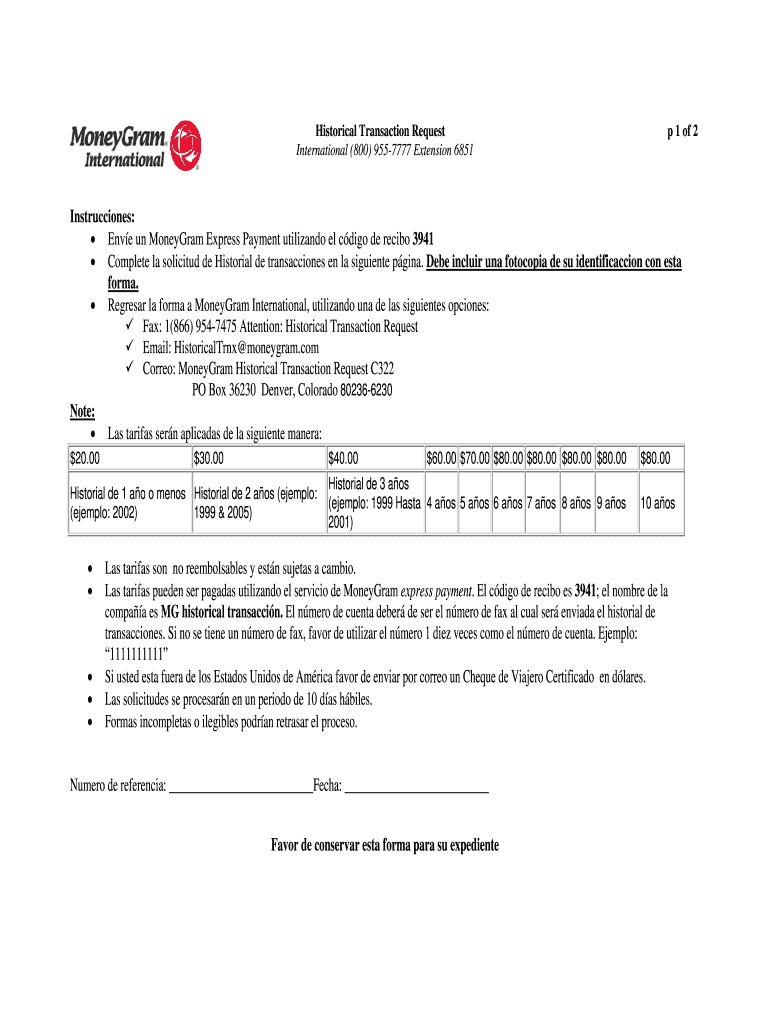
Moneygram Historical Request Form
Use a Moneygram Historical Request template to make your document workflow more streamlined.
What the Moneygram historical request form does
The Moneygram Historical Request Form is a written request for records relating to a prior Moneygram transaction or account activity. It gives the requester a structured way to identify the relevant person, transfer, date range, and records sought, while allowing Moneygram to verify authority before releasing information. A requester completes the form, adds supporting details, signs where required, and submits it through the channel specified by Moneygram. With signNow, the completed PDF can be uploaded, fields reviewed, routed for signature, and retained with an audit trail.
Who uses the Moneygram historical request form
Moneygram customers
Moneygram customers and financial-services teams use the form to request transaction history, document authorization, and related account records. Signers should confirm identity, provide accurate dates or reference details, and review every disclosure before submitting. signNow can route the completed request to authorized recipients while preserving the signed record and audit trail.
Operations teams
Compliance, legal, and support teams use the form when investigating transfers, resolving disputes, or responding to documented information requests. They can organize supporting invoices, consent forms, and correspondence alongside the request, then restrict access to personnel with a defined business need.
Features for Moneygram request handling
signNow organizes the Moneygram Historical Request Form workflow from upload through signature and evidence export, while your team controls authorization and retention decisions.
Field detection
Upload the Moneygram Historical Request Form and review its detected fields before assigning signer, date, and initials fields. This reduces manual preparation while keeping transaction-specific information under the sender’s control.
Flexible signing
Route the request to an authorized signer by email or signing link. The signer can review the exact transaction details before applying a typed or drawn electronic signature.
Audit trail
Capture signer actions, timestamps, and document history in an audit trail. Export the completed record and evidence package when compliance, support, or legal teams need review.
Mobile access
Use mobile apps for iOS and Android to review or sign the Moneygram request away from a desktop. Mobile access supports timely handling without removing required authorization checks.
Controlled storage
Connect completed request workflows with Google Drive, Box, Egnyte, or Microsoft 365. Centralized storage can help teams organize signed forms while applying their own access and retention policies.
Access controls
Apply role-based access and signer authentication to sensitive transaction records. signNow’s security controls complement, but do not replace, Moneygram’s authorization requirements or your organization’s records policy.
How to complete the Moneygram request form
Use this sequence to prepare the request, collect the required signature, and preserve evidence of completion.
Upload form:
Upload the completed Moneygram Historical Request Form to signNow. Check fields:
Review detected fields and add missing signer, date, or initials fields. Send request:
Send the request to the authorized Moneygram recipient by email. Store records:
Download the completed form and audit trail for controlled records storage.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the Moneygram audit trail records
The audit trail documents who handled the Moneygram request, what actions occurred, and when the completed record became available for review.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Create certificate:
Export evidence:
Recommended Moneygram request setup
Use a controlled signing workflow that verifies the requester, preserves the completed form, and separates platform security from your organization’s records obligations.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enabled with downloadable completion record |
| Document retention | Three years from filing when IRC §6501(a) applies |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
Platform requirements for completing the form
The Moneygram Historical Request Form workflow runs in Chrome, Firefox, Safari, or Edge on Windows and macOS, with TLS 1.2/1.3 protecting data in transit. signNow also provides mobile apps for iOS and Android, allowing authorized users to review and sign from supported devices.
Browser support Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Secure connection TLS 1.2/1.3 required for transport
Organizations should use managed devices, controlled sign-in, and role-based access when handling transaction history. Teams connecting signNow through an API or enterprise identity system should configure provisioning, access policies, and retention controls before routing requests containing personal or financial information.
Security for Moneygram request records
Data at rest:
Data in transit:
Security certification:
Security management:
Privacy compliance:
Health data protection:
Legal standing of the signed request
A signed Moneygram Historical Request Form can support a business record when the signer shows intent, consents to electronic records, can be identified, and the record remains reproducible. ESIGN, 15 U.S.C. ch. 96, and UETA generally recognize qualifying electronic signatures, but they do not require Moneygram to release records. Wills, court orders, and official court filings remain outside these rules’ ordinary scope.

Best practices for Moneygram request records
Accurate fields, documented authorization, and controlled retention make a historical transaction request easier to review and support later.
Verify every transaction detail
Export the audit trail
Apply the correct retention rule
Archive supporting evidence securely
Privacy challenges when requesting Moneygram records
Including transaction numbers, addresses, or identification details in an email attachment can expose personal information beyond the authorized review group. A missing electronic-records consent disclosure may weaken the record when the requester is a consumer and paper-record rights apply. Sending the completed request to an unverified recipient can disclose transaction history without documented authorization. Leaving signer identity or signature dates incomplete can make Moneygram’s review slower and complicate later evidence assessment.
State rules and document exclusions
Notarization required
Real-estate deed
Wills and codicils
Family-law decree
Troubleshooting Moneygram form workflows
These answers address signature, privacy, plan, and evidence questions that arise when preparing a Moneygram Historical Request Form.
Business includes legally binding eSignatures, templates, and audit trails at $8 per user per month with annual billing. Upload the completed Moneygram Historical Request Form, review fields, and send it to the authorized signer. The plan’s annual signature-invite allowance and overage terms should be reviewed before high-volume use.
Business Premium adds bulk send and costs $15 per user per month with annual billing. It may fit a team sending the same Moneygram request structure repeatedly, but each request should still contain accurate transaction-specific details and authorization.
Consumer-facing electronic records require disclosure of the right to receive paper, proof that the consumer can access the electronic format, and a withdrawal procedure under ESIGN, 15 U.S.C. §7001(c). Configure that process before requesting a consumer’s transaction history electronically.
signNow encrypts data in transit with TLS 1.2/1.3 and at rest with AES-256. Its SOC 2 Type II and ISO 27001 certifications describe platform controls, but your organization remains responsible for recipient verification, authorization, and lawful retention of Moneygram records.
Use SMS authentication or another configured signer-verification control when the request contains sensitive transaction information. Authentication helps attribute the signature, but it does not replace Moneygram’s own identity or authorization review before records are released.
The Business plan supports audit trails and costs $8 per user per month annually; Enterprise costs $30. Enterprise adds advanced signer authentication and integrations. Select the plan based on the request volume, signer controls, and system requirements actually documented by your organization.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.