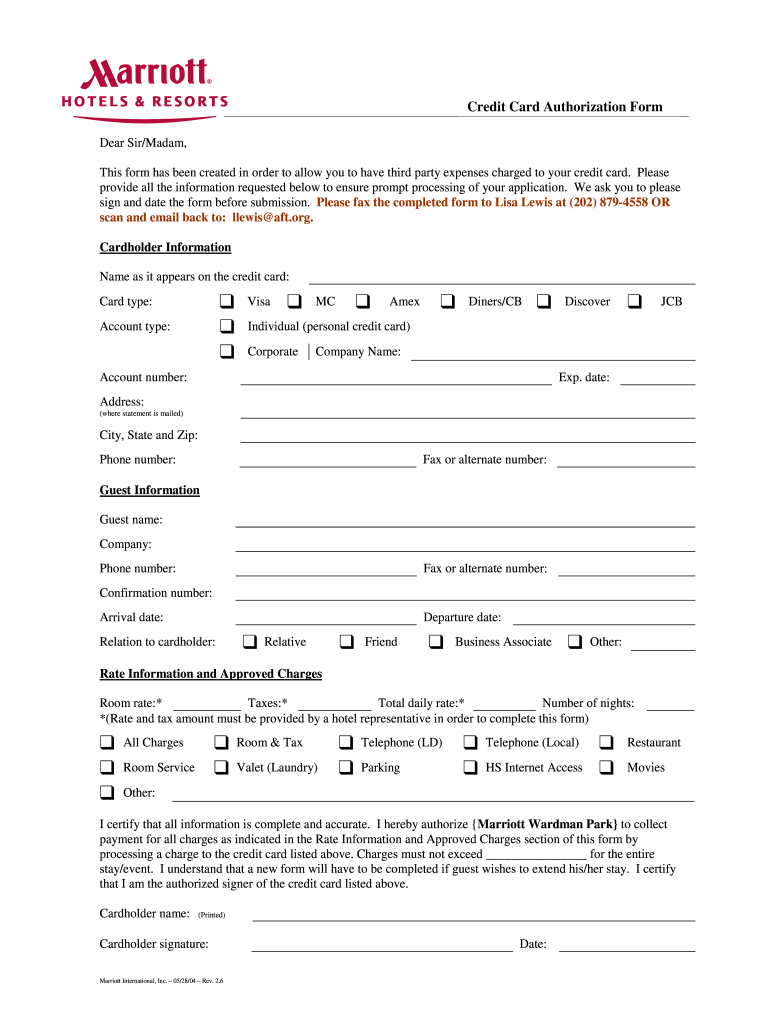
Credit Card Authorization Form Marriott Aft Aft
Use a Credit Card Authorization Form Marriott AFT Aft template to make your document workflow more streamlined.
What this Marriott authorization form does
Credit Card Authorization Form Marriott Aft Aft records a cardholder’s approval for a specified Marriott-related charge or payment arrangement. The signer reviews the transaction information presented in the form, confirms authorization, and signs electronically when the transaction and applicable law permit electronic execution. With signNow, a sender uploads the form, reviews detected fields, assigns the cardholder, sends it for signature, and retains the completed document with an audit trail. ESIGN and applicable state electronic-transaction law can support enforceability when intent, consent, attribution, and record retention are established.
Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

How this authorization works in signNow
The Marriott Aft Aft workflow moves from document preparation to signer delivery, completed authorization, and auditable storage.
Upload: Upload the Marriott Aft Aft file Detect fields: signNow detects fillable fields Send: Assign the cardholder and send Store: Store the signed record and audit trail
Complete the Marriott authorization in signNow
Use this sequence to prepare, send, sign, and retain the Marriott Aft Aft authorization.
Upload:
Upload the Marriott Aft Aft authorization to signNow. Check fields:
Review detected fields and add missing fields. Assign signer:
Assign the cardholder as the signer. Complete:
Send, collect the signature, and store the audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended authorization workflow setup
Configure the Marriott Aft Aft workflow around signer identity, transaction evidence, secure transmission, and controlled record retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email delivery with SMS OTP |
| Signature type | Typed or drawn e-signature |
| Audit trail | Enable completion certificate and history |
| Document retention | Retain under hotel records policy |
| Encryption | TLS 1.2/1.3 and AES-256 |
Track authorization processing stages
Processing time depends on document readiness, signer availability, and the delivery method selected for the Marriott Aft Aft authorization.
Prepare document
Deliver to signer
Signer turnaround
Archive record
Protect authorization records and card data
Data in transit:
Data at rest:
Security reporting:
Information security:
Cardholder safeguards:
Electronic signatures:



Best practices for Marriott Aft Aft authorizations
Accurate transaction details, controlled access, and a preserved audit trail make this authorization easier to reconcile and defend.
Review transaction details before sending
Assign fields to the correct cardholder
Preserve the signed record and audit trail
Restrict access to payment information
Privacy and disclosure pitfalls to avoid
Full payment-card details in the signed PDF can increase exposure if the file is emailed, downloaded, or stored outside an approved PCI DSS-controlled process. A missing transaction amount or unclear authorization language can make the signer’s consent difficult to connect to the specific Marriott charge. Sending the form to the wrong email address can disclose cardholder information and produce an audit trail for the wrong recipient. Allowing broad staff access to completed authorizations can expose payment information beyond employees who need it for processing or reconciliation.
Compare authorization form signing plans
signNow pricing and features are shown first; competitor figures remain unverified where the available vendor information does not confirm them.
| Features | signNow | DocuSign | Adobe Sign | PandaDoc | Dropbox Sign |
|---|---|---|---|---|---|
| Starting annual price | $8/user/month, Business plan | Not verified | Not verified | Not verified | Not verified |
| Free trial availability | 7 days, no credit card | Not verified | Not verified | Not verified | Not verified |
| Bulk send availability | Business Premium, $15/user/month | Not verified | Not verified | Not verified | Not verified |
| Audit trail availability | Included with Business plan | Not verified | Not verified | Not verified | Not verified |
| HIPAA compliance | Available with BAA requirement | Not verified | Not verified | Not verified | Not verified |
Troubleshoot Marriott Aft Aft authorization issues
Use these answers to resolve field, signer, plan, consent, legal-validity, and payment-card handling questions for this authorization workflow.
For a missing field in the Marriott Aft Aft file, upload the document again and review signNow’s detected fields before sending. Add or correct fields manually so the cardholder’s authorization, signature, and date are captured in the intended locations.
The signNow Business plan is listed at $8 per user per month with annual billing and includes legally binding eSignatures, templates, audit trails, and mobile apps. Confirm current plan terms before sending high-volume authorization batches.
Business Premium includes bulk send at $15 per user per month with annual billing. The Business plan does not have that listed bulk-send feature, so repeated Marriott authorizations may require individual preparation or a higher plan.
For consumer-facing electronic records, ESIGN requires disclosure of the right to receive paper records, access to the electronic format, and a process for withdrawing consent under 15 U.S.C. §7001(c). Apply that disclosure when the signer is a consumer.
Electronic signatures may have legal effect under ESIGN and applicable state law, including UETA in 49 states, DC, Puerto Rico, and the U.S. Virgin Islands. The record still needs signer intent, attribution, consent, and reliable retention and reproduction.
If the authorization includes payment-card information, PCI DSS controls remain relevant to the handling environment. signNow is PCI DSS certified, but the hotel must still control access, storage, transmission, and downstream processing of cardholder data.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.