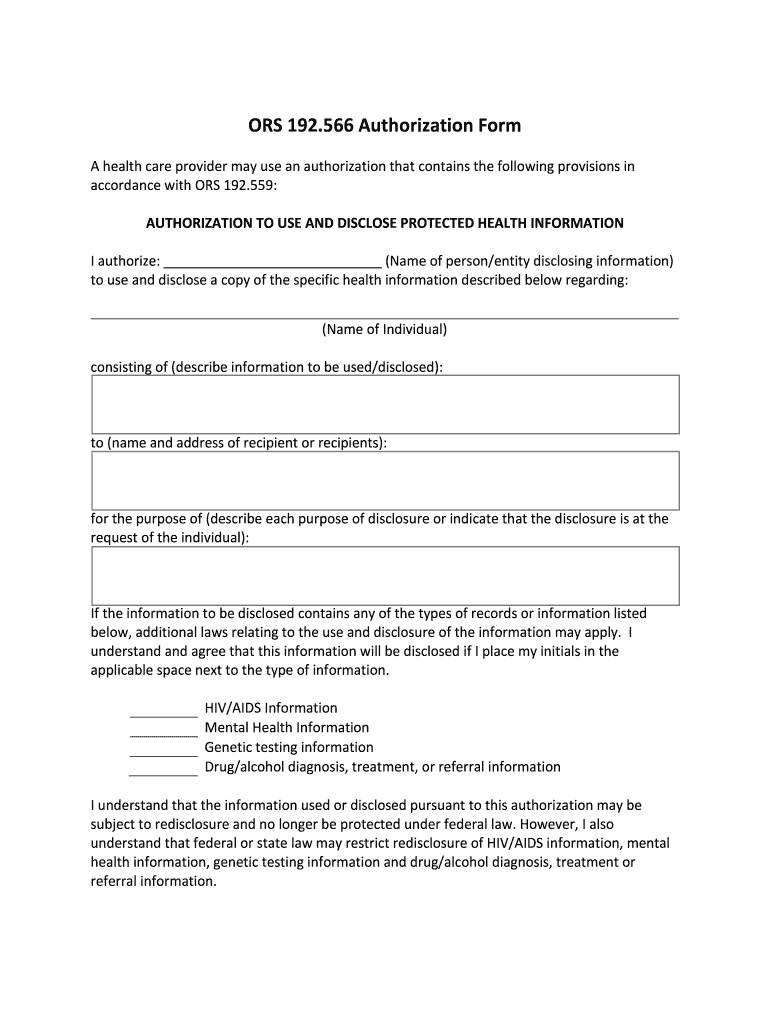
HIPAA Authorization Form Under ORS192 522
Get the Hipaa Authorization Form Under Ors192 522 0 template, fill it out, eSign it, and share it in minutes.
What this Oregon HIPAA authorization does
A HIPAA Authorization Form Under ORS192 522 gives a covered entity written permission to disclose specified protected health information to a named person or organization. The form identifies the information, recipient, purpose, and authorization period, then records the individual’s signature and date. Oregon’s reference to ORS 192.522 does not replace HIPAA’s authorization requirements. After uploading the completed form to signNow, you can place fields, send it to the signer, capture an audit trail, and retain the signed record for six years under 45 CFR 164.530(j).
Who uses this Oregon authorization
Healthcare providers
Healthcare providers and their privacy teams use the form to document a patient’s permission before releasing specified protected health information to another provider, insurer, attorney, family member, or named organization.
Patients and representatives
Patients and authorized representatives use it to identify the information, recipient, purpose, and authorization period before signing. Organizations then retain the signed form and audit evidence for disclosure review.
How this authorization workflow works
The workflow moves from document preparation to verified signing and controlled evidence retention.
Upload document: Upload the Oregon authorization into signNow. Review details: Review fields for PHI scope and recipients. Route signatures: Send the form to named signers. Archive evidence: Store the signed record and audit trail.
How to complete this form in signNow
Follow this document-specific workflow to prepare the authorization, collect signatures, and preserve evidence of completion.
Upload form:
Upload the completed Oregon authorization. Check fields:
Review detected fields and PHI scope. Add signers:
Assign patient and recipient signers. Send document:
Send the authorization for signature. Store evidence:
Download the signed PDF and audit trail.
Features that support this authorization
signNow combines form preparation, signer routing, audit evidence, HIPAA safeguards, and controlled retention for this Oregon authorization workflow.
Field detection
Upload the Oregon authorization, then review detected fields before assigning patient, recipient, date, and signature inputs. This reduces manual placement while keeping the form’s legal content under human review.
Controlled routing
Send the authorization to named signers by email or signing link, with role order configured when more than one person must review or sign the disclosure.
Audit evidence
Capture timestamps, signer actions, and document history in an audit trail that can accompany the completed authorization during privacy or compliance review.
HIPAA safeguards
Use signNow’s HIPAA-compliant service with a required business associate agreement to protect protected health information during the signing workflow.
Secure retention
Store the completed PDF and completion evidence in a controlled repository, preserving the six-year HIPAA documentation baseline under 45 CFR 164.530(j).
Records integration
Connect the workflow to Google Drive, Box, Egnyte, Microsoft 365, or another named integration to route completed authorizations into established records processes.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended workflow configuration
Configure the authorization workflow around signer identity, documented intent, protected records, and the federal HIPAA retention baseline.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with recorded intent |
| Audit trail | Enable completion history and export |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 |
Security controls for protected information
HIPAA:
TLS:
AES-256:
SOC 2 Type II:
ISO 27001:
ESIGN and UETA:
Mobile options for completing the authorization
signNow provides mobile apps for iOS and Android, supporting completion of the HIPAA Authorization Form Under ORS192 522 from supported phones and tablets. Camera-based capture can convert a paper authorization into an uploadable document, while offline signing can support work without continuous connectivity.
Mobile apps iOS and Android apps Offline mode Offline signing availability Camera capture Camera document capture
Use managed iOS or Android devices when the authorization contains protected health information. Confirm mobile-app access, screen-lock controls, remote-wipe policies, and network protections with your organization’s security team. Enterprise deployments may also require API access, SSO provisioning, and controlled retention configuration.
Processing stages for this authorization
Use these four stages to prepare, sign, complete, and preserve the HIPAA Authorization Form Under ORS192 522.
Prepare the authorization
Deliver to signers
Collect signer approval
Archive completed records
Best practices for completing the form
Accuracy matters because this authorization controls disclosure of protected health information under Oregon and federal privacy requirements.
Identify every authorized recipient
Limit the information scope
State purpose and expiration
Preserve consent and access controls
What the signNow audit trail records
The audit trail documents signer identity, document integrity, and completion evidence separately from the form’s clinical disclosure decisions.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Store evidence:
Export audit trail:
Privacy pitfalls to avoid
Leaving the recipient broad can authorize disclosure to an unintended organization or person, weakening the connection between the signer’s consent and the actual release decision. Omitting the PHI category, purpose, or expiration makes the authorization harder to interpret and may require correction before a covered entity releases records. Sending protected health information through uncontrolled downloads or shared accounts can expose the signed authorization and its attached audit evidence. Failing to document revocation or replacement can cause staff to rely on an authorization that no longer reflects the patient’s instructions.
Legal standing and practical value
A properly executed HIPAA Authorization Form Under ORS192 522 documents consent for a defined disclosure and creates reproducible evidence when retained with its audit trail. ESIGN and applicable UETA rules generally recognize electronic signatures when intent, consent, attribution, and record access are established; wills and court orders remain excluded under 15 U.S.C. §7003.

Troubleshooting this authorization workflow
Resolve form-specific issues by checking the authorization scope, signer identity, privacy safeguards, plan requirements, and retained evidence.
signNow’s HIPAA compliance requires a business associate agreement, and the workflow must still satisfy HIPAA authorization requirements. Confirm the BAA and review the form’s recipient, purpose, information scope, and expiration before sending.
The Business plan includes legally binding eSignatures, templates, and audit trails, but HIPAA support may require the applicable Site License add-on. Confirm the selected plan and BAA terms before processing protected health information.
Use signNow’s field placement tools after uploading the form, then verify each detected field manually. Auto-detection does not decide whether Oregon authorization language, recipient details, or PHI categories are legally sufficient.
A signer can receive the form through an email invitation or signing link. If identity assurance must exceed email access, configure stronger signer authentication, such as two-factor authentication or SMS OTP, before delivery.
HIPAA requires covered entities to retain required policies, procedures, and documentation for six years from creation or the last effective date under 45 CFR 164.530(j). Apply longer Oregon or organizational schedules when required.
Electronic signatures can satisfy ESIGN and applicable UETA rules when intent, consent, attribution, and record reproduction are established. Consumer-facing records also require the ESIGN disclosure and electronic-access requirements under 15 U.S.C. §7001(c).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.