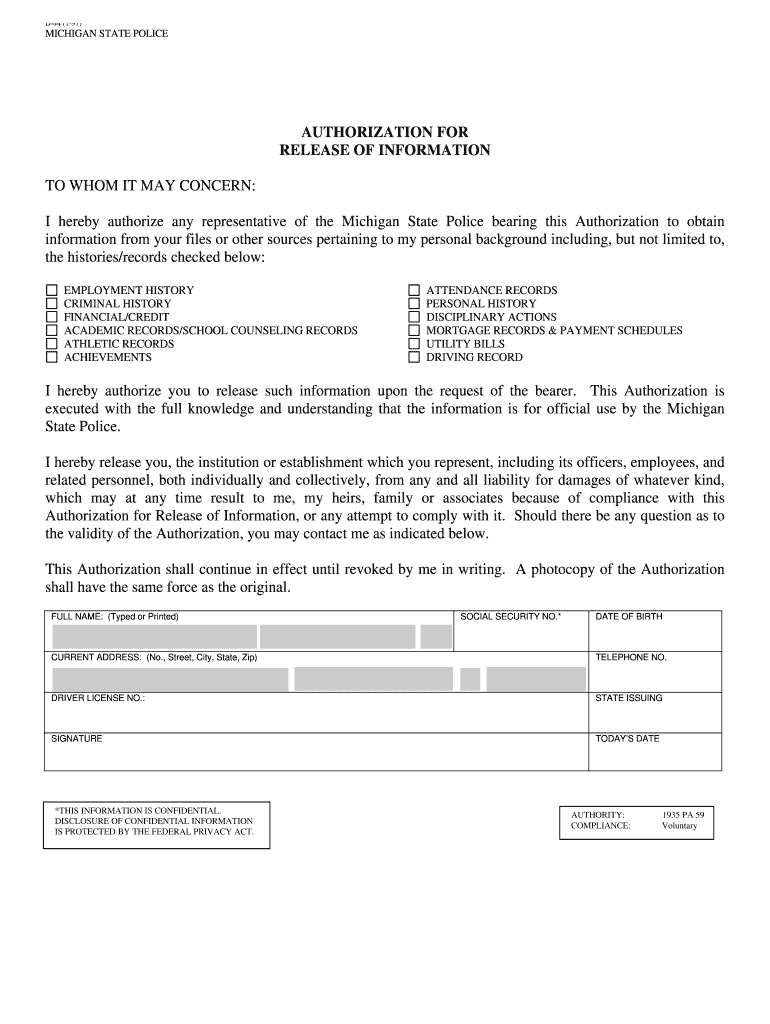
University Of Michigan Authorization To Release Patient Information
Use a University Of Michigan Authorization To Release Patient Information 0 template to make your document workflow more streamlined.
What this University of Michigan authorization does
The University of Michigan Authorization To Release Patient Information records a patient’s permission for specified health information to be disclosed to a named recipient. It identifies the person whose information is covered, the information or records that may be released, the purpose, and the signer’s authorization. In signNow, staff upload the form, review detected fields, route it to the patient or legally authorized representative, and preserve the signed PDF with an audit trail. HIPAA rules and University of Michigan policy still control whether a particular disclosure is permitted.
Who uses this authorization and why
Healthcare teams
University of Michigan health information staff use the authorization to document a patient’s permission before releasing specified medical information to a named recipient. The workflow should identify the patient, recipient, purpose, information scope, signature, and date while preserving the completed record and audit trail.
Patients and representatives
Patients and legally authorized representatives review the requested disclosure and sign when consent is appropriate. Hospitals, clinics, and authorized recipients can use the completed form to coordinate release decisions without replacing the organization’s HIPAA procedures or Michigan-specific requirements.
How this authorization workflow works
The University of Michigan authorization moves from document preparation to signed, auditable storage through a controlled signNow sequence.
Upload: Upload the University of Michigan release form to signNow. Review: Auto-detect fields and verify each disclosure detail. Route: Send the form to the authorized signer. Preserve: Store the signed authorization with its audit trail.
Complete the authorization in signNow
Use this workflow to prepare, route, sign, and preserve the University of Michigan patient information authorization.
Upload form:
Upload the University of Michigan authorization PDF to signNow. Check fields:
Review detected fields and add missing patient or recipient fields. Assign signer:
Assign the patient or representative as the signer. Send securely:
Send the authorization through the approved secure workflow. Archive record:
Store the signed form and audit trail in the designated record system.
Recommended setup for patient authorizations
Configure the authorization workflow around signer identity, HIPAA safeguards, audit evidence, and controlled access to patient information.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Electronic signature with signer intent |
| Audit trail | Capture IP, timestamps, and action history |
| Document retention | Keep six years for HIPAA records (45 CFR 164.530(j)) |
| Encryption | TLS 1.2 or 1.3 in transit, AES-256 at rest |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Privacy pitfalls in patient releases
Patient names, dates of birth, diagnoses, or recipient details can remain exposed when staff upload the wrong file or use an unrestricted sharing link. A release may omit the specific information, recipient, purpose, or expiration details needed for the University of Michigan’s disclosure process and HIPAA authorization requirements. Delegated senders can accidentally route protected health information to an unintended recipient when role permissions and signer addresses are not reviewed before sending. Paper copies, signed PDFs, and audit trails can become separated, making it difficult to prove exactly what the patient or representative authorized.
Security for patient information workflows
HIPAA protection:
Transit encryption:
Storage encryption:
Security certification:
Information security:
Regulatory alignment:
Mobile options for patient authorizations
signNow mobile apps for iOS and Android let authorized staff review and sign the University of Michigan authorization on supported phones. Camera-based capture can convert a paper copy into a document for preparation, while secure connectivity protects transmission.
iPhone app iOS 15 and later Android app Android 10 and later Document capture Camera capture available
Use managed iOS or Android devices when patient information is involved. Confirm mobile access controls, authentication settings, and organizational retention policies before routing completed authorizations. Offline signing availability and device behavior should be tested against the organization’s approved signNow configuration before clinical deployment.



Manage teams and permissions
Health information administrators can manage shared University of Michigan templates, assign sending roles, and restrict access to patient authorization records by team or department. Clinical operations teams can use delegated sending so authorized staff prepare and route the form while administrators retain control over templates, permissions, and completed records.
Retention schedules for related records
Apply the six-year HIPAA rule to covered health information records and verify University of Michigan policy before assigning a final retention schedule.
Six years: HIPAA records
Three years: tax records
Three years or later: I-9 records
Three years: FLSA payroll
Five years: OSHA injury
Risks from incorrect authorization use
Patient privacy exposure
Release dispute
HIPAA compliance failure
Electronic record exception
Legal standing of electronic consent
A completed University of Michigan authorization can provide evidence of consent when the signer’s intent, identity, electronic consent, and retained record are demonstrated. ESIGN and UETA generally recognize electronic signatures, while HIPAA procedures and applicable Michigan law still govern disclosure scope, authorization validity, and protected health information handling.

Troubleshooting patient authorization workflows
Resolve field, signer, HIPAA, retention, and electronic-signature questions before releasing University of Michigan patient information.
If signNow does not detect the University of Michigan form fields, upload the original PDF and review the generated fields manually. Add explicit text, signature, date, and recipient fields where the document requires them. A staff member should compare the prepared version against the source authorization before sending.
signNow Business includes legally binding eSignatures, audit trails, templates, and mobile apps. For protected health information, HIPAA compliance requires a business associate agreement. Confirm the organization’s plan, account configuration, and BAA status before processing this authorization, rather than relying on the plan name alone.
The authorization should identify the patient, authorized recipient, disclosure scope, purpose, and signer. If one is missing, pause the workflow and follow University of Michigan and HIPAA procedures for correction. Do not infer consent from an email reply or substitute a different release document.
signNow can use email delivery and optional SMS authentication for the signer. If the patient or representative cannot access the message, verify the address, resend through the approved workflow, or use an authorized alternative. Record the final successful signing event and avoid sending protected information through unapproved channels.
After completion, preserve the signed PDF and signNow audit trail together. HIPAA requires covered entities to retain required policies, procedures, and related records for six years under 45 CFR 164.530(j); University of Michigan policy may impose additional requirements for this authorization.
Electronic signatures generally receive legal recognition under ESIGN and UETA when intent, consent, attribution, and record retention are established. Those laws do not replace HIPAA authorization requirements or Michigan disclosure rules. Review the form’s scope and institutional policy before treating an electronic signature as sufficient.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.