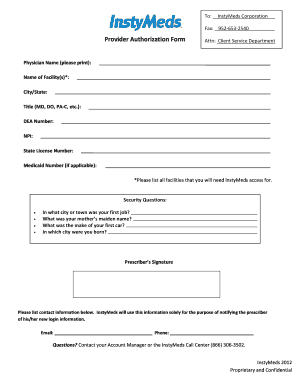
Instymeds Provider Authorization Form
Use a Instymeds Provider Authorization Form template to make your document workflow more streamlined.
What this provider authorization form does
The Instymeds Provider Authorization Form records a provider’s permission for a defined Instymeds-related activity, so the organization can document who authorized what and when. In signNow, upload the form, review automatically detected fillable fields, add provider and recipient roles, and send it for signature. The signer reviews the authorization, provides an electronic signature, and receives a completed copy. signNow stores the signed document with an audit trail and completion evidence. ESIGN and UETA generally support electronic signatures when intent, consent, attribution, and record retention requirements are satisfied.
Who benefits from this authorization workflow
The form supports individual providers, healthcare operations teams, and larger organizations that need traceable authorization records.
Solo healthcare practitioners can use the form to authorize a defined Instymeds workflow without printing, scanning, or arranging a separate signing appointment. The provider reviews the exact scope, signs electronically, and keeps the completed authorization with its audit evidence. Healthcare organizations and provider operations teams can standardize the form through reusable signNow templates. Administrators control access, route authorizations to the correct signer, and preserve completed records for internal review, HIPAA-related procedures, or contractual obligations. Enterprise medical networks can connect provider authorization workflows to systems such as Salesforce, Microsoft Dynamics 365, NetSuite, or cloud storage. Centralized teams can manage permissions while local offices send the approved form through controlled processes.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Key features for provider authorization
signNow connects form preparation, signer routing, electronic execution, and evidence preservation around the specific authorization document.
Field detection
Upload the Instymeds Provider Authorization Form and review automatically detected fields before sending, reducing manual preparation for provider names, dates, scopes, and signature locations.
Role routing
Assign provider and recipient roles directly in the document workflow so each person receives only the fields and actions required for this authorization.
Electronic signing
Send the completed form for electronic signature by email or signing link, allowing authorized providers to review and sign without exchanging paper copies.
Audit trail
Capture signer actions, timestamps, access events, and completion details in an audit trail that accompanies the signed authorization record.
Reusable templates
Use reusable templates for approved versions of the authorization form, while limiting editing rights to administrators who manage provider workflows.
Evidence export
Export the signed form and completion evidence for controlled storage, review, and retention under the organization’s applicable privacy and recordkeeping rules.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How to complete the authorization form
Use this sequence to prepare the Instymeds Provider Authorization Form, route it to the correct signer, and preserve the completed record.
Upload form:
Upload the current form. Check fields:
Review detected provider fields. Assign roles:
Assign signer and recipient roles. Send form:
Send through signNow. Archive record:
Store signed form and evidence.
How the audit trail records authorization
signNow records signer identity, document integrity, signing events, and retrievable completion evidence for this authorization form.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log actions:
Export evidence:
Recommended authorization workflow setup
Configure the authorization workflow around signer identity, document integrity, access control, and the retention rule that applies to the record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Intent-based electronic signature |
| Audit trail | Enabled with completion certificate |
| Document retention | Six years for HIPAA records |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
Privacy pitfalls in provider authorizations
Personal health or provider information may remain visible to recipients who do not need access to the authorization record. A signer may complete the document without a clear electronic-consent disclosure or confirmation of access to the electronic record. Shared links, broad folder permissions, or forwarded emails can expose the signed authorization to unauthorized viewers. Using one template for different providers can place incorrect identifiers, scopes, or authorization dates into the final document.
Risks of incomplete authorization records
Disputed authorization
Weak evidence
Consent challenge
Privacy exposure
Security for authorization records
Encryption:
Healthcare safeguards:
Service controls:
Security management:
Transport security:
Stored data:
Troubleshooting provider authorization workflows
These answers address field detection, plan selection, electronic-signature requirements, privacy safeguards, and evidence retrieval for this form.
Upload the original PDF or template again, then inspect signNow’s detected fields. Auto-detection can place fields incorrectly when labels, lines, or provider identifiers are unclear. Move, add, or relabel fields before sending the authorization for signature.
Business includes legally binding eSignatures, templates, and audit trails at $8/user/month with annual billing. Confirm the account plan and invite allowance before sending repeated authorization forms; paid subscription plans include 100 signature invites per user annually.
For a healthcare workflow, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm that the necessary BAA and organizational safeguards are in place before using the authorization with protected health information.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention requirements are met. Consumer-facing records may require an electronic-record disclosure under 15 U.S.C. §7001(c). Review the specific transaction and state law.
Business Premium is listed at $15/user/month annually and adds bulk send. If repeated provider authorizations require batch delivery, verify the recipient data and template fields before using bulk-send workflows.
Use signNow’s audit trail and completion certificate to review signer identity, timestamps, actions, and document history. Export the completed evidence with the signed form and restrict storage access according to the authorization’s data sensitivity.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.