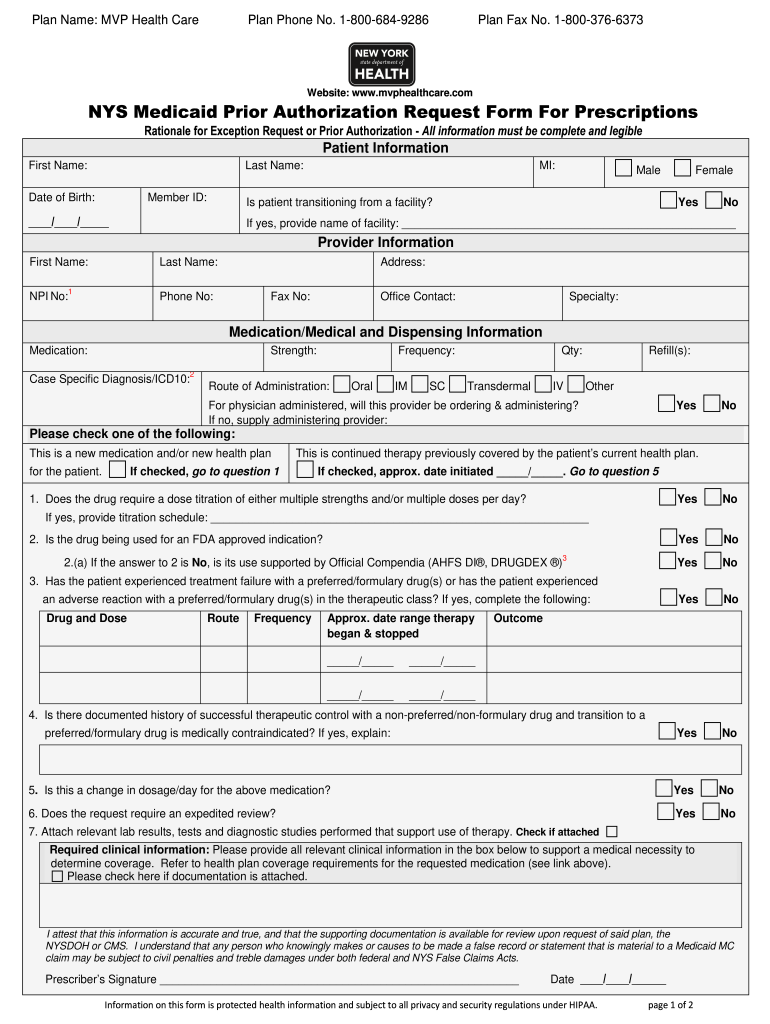
Fidelis Prior Auth Form
Get the Fidelis Prior Auth Form 0 template, fill it out, eSign it, and share it in minutes.
What the Fidelis prior authorization form does
The Fidelis Prior Auth Form is a healthcare authorization request used to obtain payer review before a specified service, treatment, medication, or procedure proceeds. Staff typically enter patient identifiers, insurance information, the ordering or treating provider, diagnosis details, requested service, clinical rationale, and supporting documentation. In signNow, upload the form, review detected fillable fields, complete the request, route it to required signers, and retain the signed PDF with its audit trail. Payer-specific submission instructions and approval requirements remain controlled by Fidelis and the applicable health plan.
Who uses the Fidelis authorization form
Healthcare practices
Healthcare practices can complete patient and insurance sections, obtain provider signatures, and organize authorization records before submitting them through the payer’s designated channel.
Provider organizations
Hospitals, specialty clinics, and utilization-review teams can coordinate clinical justification, provider approval, and supporting records for Fidelis authorization requests.
Teams that manage Fidelis authorizations
Fidelis Prior Auth Form is most useful where patient information, clinical justification, provider approval, and payer follow-up must stay coordinated.
Specialty clinics can collect provider approval and patient information for Fidelis authorization requests before sending clinical documentation through the payer’s required channel. Hospital utilization-review teams can coordinate diagnosis details, requested services, signatures, and supporting records across departments while preserving an auditable document history. Independent practices can use reusable signNow templates to prepare patient-specific requests, route them to clinicians, and retrieve completed authorization records without paper handling.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features for Fidelis prior authorization
Fidelis Prior Auth Form workflows can organize patient details, clinical justification, signatures, routing, and records in one signNow process.
Field detection
Upload the Fidelis Prior Auth Form and use detected fields to reduce manual placement work before entering patient, provider, diagnosis, and requested-service information.
Signer routing
Route the completed authorization request to the appropriate signer or reviewer by email, while keeping the requested service and supporting details in one document.
Audit trail
Capture patient and provider approvals with an audit trail that records signing activity, timestamps, and document history for later review.
Reusable templates
Use reusable Fidelis Prior Auth Form templates so staff can apply consistent patient, insurance, diagnosis, and treatment-request fields across authorization submissions.
Mobile access
Work from a desktop or mobile device when collecting signatures from patients, clinicians, or authorized representatives involved in the request.
Secure records
Store completed forms and signing records in a controlled electronic workflow, supporting retrieval when an insurer, provider, or compliance team requests documentation.
How the Fidelis form workflow works
Prepare the payer-specific request in signNow, collect required approvals, and preserve the completed authorization record.
Upload form: Upload the Fidelis form Check fields: Review detected fields Send request: Route required signers Archive record: Store signed records
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended Fidelis form workflow setup
Configure the Fidelis Prior Auth Form workflow around signer identity, patient-data protection, auditability, and the organization’s applicable retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Electronic signature with signer intent |
| Audit trail | Export with completed PDF |
| Document retention | Apply provider policy and HIPAA six-year rule |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |



Platform requirements for signing
Fidelis Prior Auth Form can be prepared in signNow through Chrome, Firefox, Safari, or Edge on Windows and macOS. signNow also provides iOS and Android apps for mobile review and signing.
Supported browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile apps iOS and Android mobile apps
Healthcare organizations should use managed Windows, macOS, iOS, or Android devices when patient information is involved. Configure account permissions, signer authentication, and storage access before distributing the Fidelis Prior Auth Form, and verify that the completed record can be retrieved for payer or compliance review.
Security for patient authorization records
Healthcare safeguards:
Transport encryption:
Stored data:
Security reporting:
Information security:
Electronic signatures:
Privacy pitfalls in authorization workflows
Patient identifiers, insurance numbers, and clinical details may be exposed when completed forms are emailed without controlled access or encrypted storage. A missing electronic-consent record can weaken evidence that a patient or provider agreed to use electronic records under ESIGN’s consumer-disclosure requirements. Overbroad team permissions can allow unauthorized staff to view, download, or forward Fidelis authorization records containing protected health information. Copying diagnosis or treatment details into the wrong patient’s form can create a privacy incident and require correction before payer submission.
Record-keeping practices for Fidelis forms
Retain the signed request, audit evidence, submission record, and payer response as one controlled authorization file.
Export the signed form and audit trail
Apply the six-year HIPAA rule
Limit identifiers and access
Preserve payer responses with forms
What the Fidelis audit trail records
The audit trail preserves evidence of who interacted with the authorization request, when actions occurred, and which signed record was completed.
Authenticate signer:
Capture timestamp:
Track document history:
Preserve integrity:
Link signer activity:
Export audit trail:
Risks of incomplete authorization requests
Missing clinical details
Unclear treatment rationale
Incomplete signer record
Incorrect patient identifiers
Fidelis prior authorization troubleshooting
Use these answers to resolve field, signer, compliance, audit-trail, plan, and payer-submission questions for Fidelis Prior Auth Form workflows.
Upload the original Fidelis Prior Auth Form as a PDF, then inspect signNow’s detected fields before sending. If fields are absent or misplaced, add and label patient, provider, diagnosis, requested-service, and signature fields manually. Confirm the final document preserves all payer-required sections.
The signNow Business plan includes templates and audit trails but does not include bulk send. Business Premium adds bulk send at $15/user/month when billed annually. Use bulk send only when each authorization request is independently reviewed and contains the correct patient-specific information.
A HIPAA workflow requires a Business Associate Agreement with signNow and appropriate access controls. The product is listed as HIPAA compliant with a BAA required. Confirm that the payer, provider organization, and internal privacy policies permit electronic handling of the submitted health information.
Use signNow’s signer authentication options, including SMS codes where configured, when patient or provider identity requires more than an email link. Record the authorization purpose and obtain required electronic consent before signing under ESIGN and applicable state law.
signNow records timestamps, document history, and signing activity in an audit trail. Export the completed PDF and audit information together, then retain them according to the provider’s policy, payer requirements, and applicable health-record rules rather than assuming signNow sets the retention period.
A signed Fidelis Prior Auth Form documents authorization activity but does not replace Fidelis submission, payer approval, medical-necessity review, or an authorization number. After signing, follow the applicable payer channel and verify the request status separately.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.