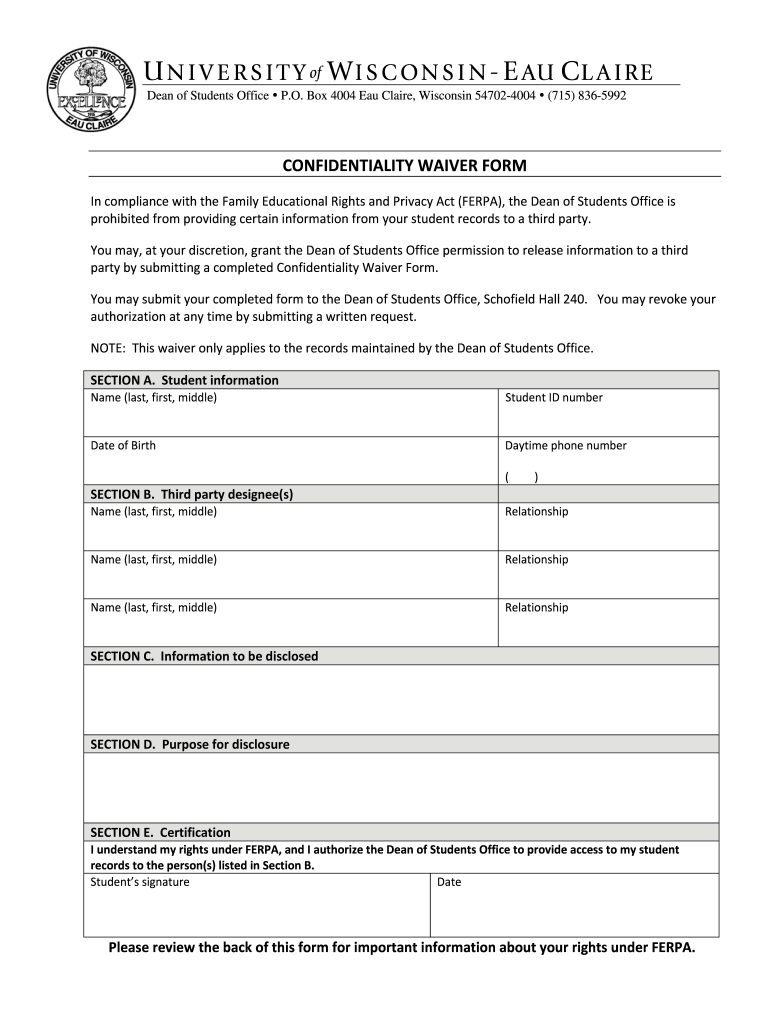
Patient Confidentiality Form
Create a custom Patient Confidentiality Form 0 that meets your industry’s specifications.
What a Patient Confidentiality Form does
A Patient Confidentiality Form records a patient’s authorization to protect and control specified health information disclosures. It identifies the patient, the permitted recipient or organization, the information covered, the purpose, authorization limits, signature, and date. With signNow, a healthcare team uploads the form, reviews detected fillable fields, assigns patient and provider fields, sends it for signature, and stores the completed document with an audit trail. HIPAA-covered records require retention for six years from creation or the last effective date under 45 CFR §164.530(j).
Who uses this confidentiality form
Healthcare clinics
A clinic uses the Patient Confidentiality Form to document a patient’s authorization before releasing specified records to another provider, insurer, caregiver, or representative. Staff should identify the permitted recipient, purpose, information scope, expiration terms, and patient signature before disclosure.
Specialty practices
A behavioral-health practice or fertility center can route confidentiality authorizations to patients remotely, then retain the signed form and audit trail with the relevant chart. HIPAA compliance requires a BAA with signNow when the platform handles protected health information.
How to complete this form online
Use this workflow to prepare, route, sign, and preserve a Patient Confidentiality Form without losing its authorization details.
Upload form:
Upload the Patient Confidentiality Form PDF. Check fields:
Review auto-detected authorization and signature fields. Assign roles:
Assign patient and provider signing roles. Send securely:
Send the form through signNow. Archive record:
Store the signed PDF and audit trail.
Recommended confidentiality form setup
Configure the Patient Confidentiality Form around verified patient identity, limited disclosure scope, protected storage, and documented access.
| Setting | Recommendation |
|---|---|
| Authentication and provisioning | Use SMS verification with role-based team access |
| Signature type | Use typed or drawn patient signature |
| Audit trail | Retain completion certificate with signed PDF |
| Document retention | Six years under HIPAA 45 CFR 164.530(j) |
| Encryption | Use TLS 1.2 or 1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
A signNow audit trail adds evidence around the patient’s authorization, signature event, document integrity, and later record retrieval.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Log activity:
Export audit trail:
Security for patient confidentiality forms
Data in transit:
Stored data:
HIPAA safeguards:
Service controls:
Security management:
Signer authentication:
Mobile options for confidentiality forms
Patient Confidentiality Form workflows can run through signNow mobile apps on iOS and Android, with TLS 1.2 or 1.3 protecting data in transit. Users can review documents, capture signatures, and use camera-based document capture from supported mobile devices.
iOS app iOS 15 and later Android app Android 9 and later Mobile signing Camera capture and offline signing
Healthcare organizations should manage iOS and Android devices through approved security policies, especially when forms contain protected health information. Confirm offline-signing procedures, synchronize completed records securely, limit local storage, and configure access controls before deploying mobile completion across clinical or administrative teams.
Privacy pitfalls in confidentiality forms
Including diagnoses, medications, or unrelated clinical notes exposes more protected health information than the Patient Confidentiality Form requires for its stated disclosure purpose. A missing patient signature, date, or authorization scope can leave the disclosure permission incomplete and difficult to defend during an audit or dispute. Sending a completed form to an incorrect email address can disclose protected health information to an unauthorized recipient before access is revoked. Granting every staff member template or download access can defeat minimum-necessary controls and create unnecessary copies of signed patient records.
Record-keeping practices for confidentiality forms
Protect the signed form, audit evidence, and patient information throughout its retention period with documented controls.
Apply the six-year HIPAA retention rule
Export the signed record and audit trail
Archive patient records with restricted access
Record each retention decision
Retention periods for signed records
Apply the retention period tied to the record’s actual content and regulatory category, not merely its signature date.
Six years for HIPAA records
Three years for tax records
Six years for major understatement
Three years for payroll records
Five years for injury records
Risks and document exclusions
Excess information
Invalid authorization
PHI exposure
No ESIGN coverage
Patient Confidentiality Form troubleshooting
Resolve field, authentication, HIPAA, and retention questions before releasing protected health information.
Upload the original Patient Confidentiality Form as a clear PDF, then review signNow’s detected fields before sending. Add missing authorization, recipient, purpose, expiration, signature, and date fields manually so the completed record captures the required disclosure scope.
Use signNow’s Business Premium plan when a clinic must send the same confidentiality authorization to multiple patients. Business Premium includes bulk send, while the Business plan provides templates and audit trails without that bulk-send feature.
A HIPAA-covered workflow requires a business associate agreement with signNow. The platform identifies HIPAA compliance as requiring a BAA; do not treat encryption or an audit trail alone as a substitute for the agreement.
Use signNow authentication appropriate to the disclosure risk, such as SMS verification or stronger authentication where configured. Confirm the signer’s identity, preserve the audit trail, and verify that the patient consented to electronic records under ESIGN requirements.
If a signer cannot access the form, verify the email address, resend the invitation, or generate a controlled signing link. Do not forward a completed form through an unapproved channel because it may expose protected health information.
After completion, download the signed PDF and audit trail, then store both with the patient record. Apply the six-year HIPAA period under 45 CFR §164.530(j), unless a longer applicable state or organizational rule controls.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.