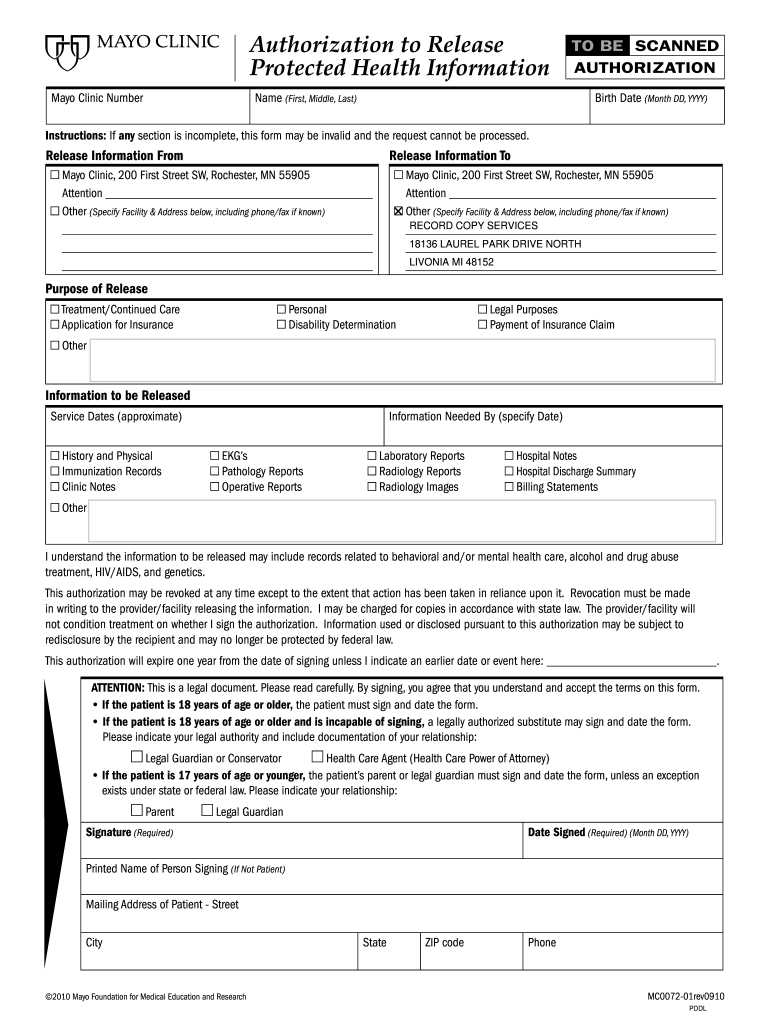
Authorization To Release Protected Health Information MC0072 01 Authorization Release Protected Health Information Authoriz
Use a Authorization To Release Protected Health Information MC0072 01 Authorization Release Protected Health Information Authoriz template to make your document workflow more streamlined.
What this authorization form does
This form gives a patient or authorized personal representative a documented way to permit a healthcare provider to release specified protected health information to named recipients. It identifies the information covered, the purpose of disclosure, the recipient, expiration terms, and required signatures. Under HIPAA, authorization language must describe the information, recipient, purpose, and expiration or event. signNow can accept the uploaded MC0072 authorization, detect fillable fields, route it for signatures, and preserve the completed record with an audit trail.
Who uses this health-information authorization
Healthcare providers
Healthcare providers use this authorization to document a patient’s permission to disclose specified protected health information. Staff can identify the recipient, requested records, purpose, expiration terms, and required signatures before sending the completed form through a controlled workflow.
Patients and representatives
Patients, personal representatives, and authorized recipients use the form to define exactly which protected health information may be released. A completed copy helps the provider verify consent before disclosing records to another person, organization, insurer, or care participant.
Features that support MC0072 workflows
signNow combines field preparation, signer routing, audit evidence, and protected-information controls for this healthcare authorization workflow.
Field detection
Upload MC0072 and let signNow detect fillable areas, reducing manual placement work before entering patient, recipient, purpose, and expiration information.
Signer routing
Assign signature fields to the patient, representative, provider, or other required parties so each signer receives only the actions assigned to them.
Reusable templates
Use templates for recurring authorization requests while preserving the specific disclosure scope and recipient information required for each patient.
Audit trail
Capture timestamps, IP information, action history, and completion evidence that can accompany the signed authorization during records review.
HIPAA controls
Protect the workflow with HIPAA compliance when a Business Associate Agreement is required and configured for the organization’s use.
Mobile signing
Complete and review the authorization from desktop or mobile apps, supporting staff and patients who cannot meet in person.
How the MC0072 workflow works
MC0072 moves from field preparation to controlled signing and documented retention in four practical stages.
Upload: Upload the MC0072 authorization. Prepare: Auto-detect and review fillable fields. Route: Assign fields to each signer. Retain: Store the completed authorization and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How signNow records this authorization
The signNow audit trail records identity, timing, document integrity, and retrieval details for this health-information authorization.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper sealing:
Event logging:
Audit export:
Recommended authorization workflow setup
Configure the authorization workflow around signer identity, consent evidence, protected information, and documented retention requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Capture timestamps, IP, and action history |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 encryption |



Privacy pitfalls in disclosure workflows
Including diagnoses, treatments, or identifiers beyond the requested disclosure increases exposure if the completed authorization is shared incorrectly. Failing to identify each recipient can leave staff uncertain whether a particular person or organization may receive protected health information. Using an unchecked or incomplete consent field can weaken evidence that the patient approved the specified disclosure. Giving every employee access to the signed authorization can exceed the role-based access needed for processing.
Risks of incomplete authorization
Overbroad disclosure
Incomplete execution
Recipient ambiguity
Privacy exposure
Security for protected health information
HIPAA protection:
Transit encryption:
Stored encryption:
Security controls:
Security certification:
Signature compliance:
Best practices for completing MC0072
A careful MC0072 process protects disclosure scope, signer evidence, and the patient’s record throughout completion and retention.
Review every disclosure element
Restrict access to records
Retain the complete record
Confirm the HIPAA agreement
Processing this authorization from start to finish
Use a controlled sequence so MC0072 is complete, reviewable, and stored with evidence of consent.
Prepare the form
Deliver to signers
Complete signatures
Archive the record
Troubleshooting MC0072 authorization workflows
These answers address specific completion, signing, privacy, retention, and signNow configuration questions for MC0072.
Yes, signNow supports HIPAA-compliant workflows when the required Business Associate Agreement is in place. Confirm that the account configuration, access controls, recipients, and retention process match your organization’s HIPAA obligations before sending MC0072 containing protected health information.
Check that the authorization identifies the information to disclose, recipient, purpose, and expiration terms. HIPAA requires these elements for a valid authorization. Correct the document before sending; an audit trail cannot cure missing or ambiguous consent language.
The Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month when billed annually. Business Premium adds bulk send, while Enterprise adds advanced signer authentication and conditional fields.
Use signNow’s signer authentication options, including SMS-based verification where configured, when the recipient or provider requires stronger identity evidence. Record the signer’s identity and maintain the completed authorization and audit trail together for later disclosure review.
The audit trail records signing timestamps, IP information, action history, and completion evidence. Export it with the signed MC0072 authorization when your records policy requires proof of who signed, what was signed, and when each action occurred.
HIPAA’s administrative-record retention rule requires documentation to be retained for six years from creation or the last effective date, whichever is later, under 45 CFR 164.530(j). State law or another healthcare rule may require a longer period.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.