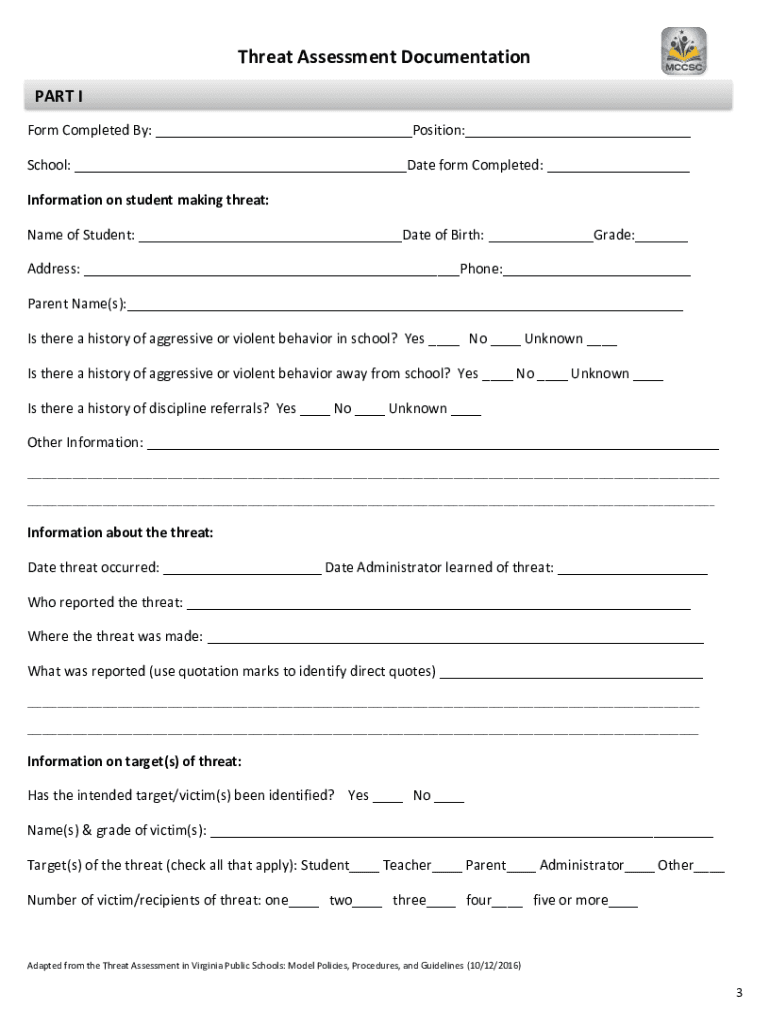
Mccsc Threat Assessment Form
Use a Mccsc Threat Assessment template to make your document workflow more streamlined.
What the Mccsc Threat Assessment Form records
The Mccsc Threat Assessment Form is a structured record for documenting and reviewing a reported threat or safety concern through an organization’s authorized assessment process. It can capture the information reviewers need to evaluate the report, document relevant observations, identify follow-up actions, and obtain required approvals. Because the form’s issuing organization and exact fields are not identified in the available source material, users should follow their local instructions for completion, escalation, and retention. signNow can upload the form, detect fillable fields, route it to designated recipients, capture signatures, and preserve an audit trail.
Features for completing the Mccsc Threat Assessment Form
The Mccsc Threat Assessment Form combines structured documentation, controlled review, electronic signatures, and an auditable record for authorized teams.
Structured record
Capture the concern, observed behavior, context, and follow-up information in one structured record, helping reviewers work from the same documented facts.
Clear responses
Complete the Mccsc Threat Assessment Form electronically so required responses remain legible, organized, and available for authorized review without rekeying handwritten notes.
Controlled routing
Route the completed form to designated reviewers or signers through signNow, reducing email attachments and preserving a documented handoff for the assessment process.
Review history
Use signer authentication and an audit trail to connect each signature event with timestamps, actions, and document history for later internal review.
Secure records
Store the completed assessment with its signing evidence, supporting consistent record handling when a school, district, or organization reviews the matter later.
Mobile access
Access the form from a desktop or mobile device when authorized staff need to document or review an assessment away from a central office.
Who uses the Mccsc Threat Assessment Form
School-based threat assessment team members use the Mccsc Threat Assessment Form to organize reported concerns, document observed facts, record review decisions, and route the completed assessment for required signatures or approvals. District administrators and authorized student-support personnel use the form to standardize handoffs between schools, preserve assessment documentation, and review whether follow-up actions were recorded without relying on scattered email messages or handwritten pages.
Ways to send and sign the assessment
- Use the signNow web app when a school or district office prepares the Mccsc Threat Assessment Form, places fields, and coordinates review from a managed desktop browser.
- Use the signNow mobile app when authorized staff need to review or sign the assessment from an iOS or Android device while away from the office.
- Use kiosk mode when a controlled workstation supports an in-person signing station and the organization has configured the appropriate signNow Business Premium workflow.
- Use a shareable signing link when approved recipients need access without a separate email attachment, while administrators retain control over the intended document and signing route.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How to complete the assessment online
Follow the document-specific workflow from upload through field review, signing, and audit-trail storage.
Upload form:
Upload the official Mccsc Threat Assessment Form file. Check fields:
Review detected fields and add missing fields. Assign roles:
Assign responses, signatures, and recipients. Send workflow:
Send the assessment through signNow. Complete review:
Review and sign the assigned sections. Archive record:
Store the signed form with its audit trail.
Privacy and disclosure pitfalls to avoid
Including unnecessary student or employee details in the Mccsc Threat Assessment Form can expose sensitive information beyond the authorized assessment team. Skipping electronic-consent language or signer authentication can make it harder to demonstrate who approved the completed assessment and when the approval occurred. Sending the form through unrestricted email attachments can create uncontrolled copies and weaken access management for sensitive threat-assessment information. Using shared accounts or broad folder permissions can prevent administrators from reliably attributing edits, signatures, and downloads to the responsible individual.
Best practices for assessment records
Use a controlled workflow that protects sensitive information while keeping the Mccsc Threat Assessment Form complete, attributable, and retrievable.
Validate fields before distribution
Restrict access to authorized reviewers
Preserve the complete record
Complete a final quality review
Platform requirements for the Mccsc Threat Assessment Form
The Mccsc Threat Assessment Form can be prepared through a supported browser on Windows or macOS, or accessed through signNow mobile apps on iOS and Android. Use an up-to-date browser and an internet connection for document delivery, authentication, and audit-trail synchronization.
Browser support Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile systems iOS and Android mobile access
Organizations should use managed Windows, macOS, iOS, or Android devices when the assessment contains sensitive student, employee, or community information. Administrators should also confirm signNow access permissions, authentication requirements, API or SSO configuration, and local retention policies before distributing the completed form.
Signer authentication and document security
Two-factor authentication:
SMS verification:
Identity verification:
PKI signatures:
X.509 certificates:
Audit evidence:



Recommended workflow setup
Configure the Mccsc Threat Assessment Form around controlled access, attributable approvals, complete audit evidence, and the organization’s records policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion history and timestamps |
| Document retention | Follow district and state records policy |
| Encryption | Use TLS and AES-256 protection |
Troubleshooting the Mccsc Threat Assessment Form
Use these answers to resolve specific upload, access, authentication, compliance, and plan questions involving the Mccsc Threat Assessment Form.
The Mccsc Threat Assessment Form is not fillable after upload. Upload the original PDF or document file, then review signNow’s detected fields before sending. If fields are missing, add them manually and assign each field to the correct participant. Do not assume an unassigned blank is an intentional response area.
The assessment needs more than basic signing controls. The Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month when billed annually. Business Premium adds bulk send and kiosk mode at $15 per user per month annually.
The form contains sensitive student or health information. signNow states that HIPAA compliance requires a business associate agreement, while access controls and authentication should follow the organization’s policy. Confirm the applicable school, state, and federal requirements before processing protected information.
A reviewer cannot open the signing request. Confirm the recipient email address, resend the invitation, or provide an approved signNow signing link. If the organization uses stronger authentication, verify that the recipient can complete the configured SMS OTP or identity-verification step.
The signed assessment needs evidentiary support. Keep the completed document with its signNow audit trail, including signing events and timestamps. ESIGN and applicable state electronic-transactions law focus on intent, consent, attribution, and the ability to retain and reproduce the record.
The organization needs many assessments sent individually. Business Premium includes bulk send, while the Business plan does not list bulk send in the supplied plan details. Confirm recipient permissions and local privacy policy before using a bulk workflow for sensitive assessments.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.