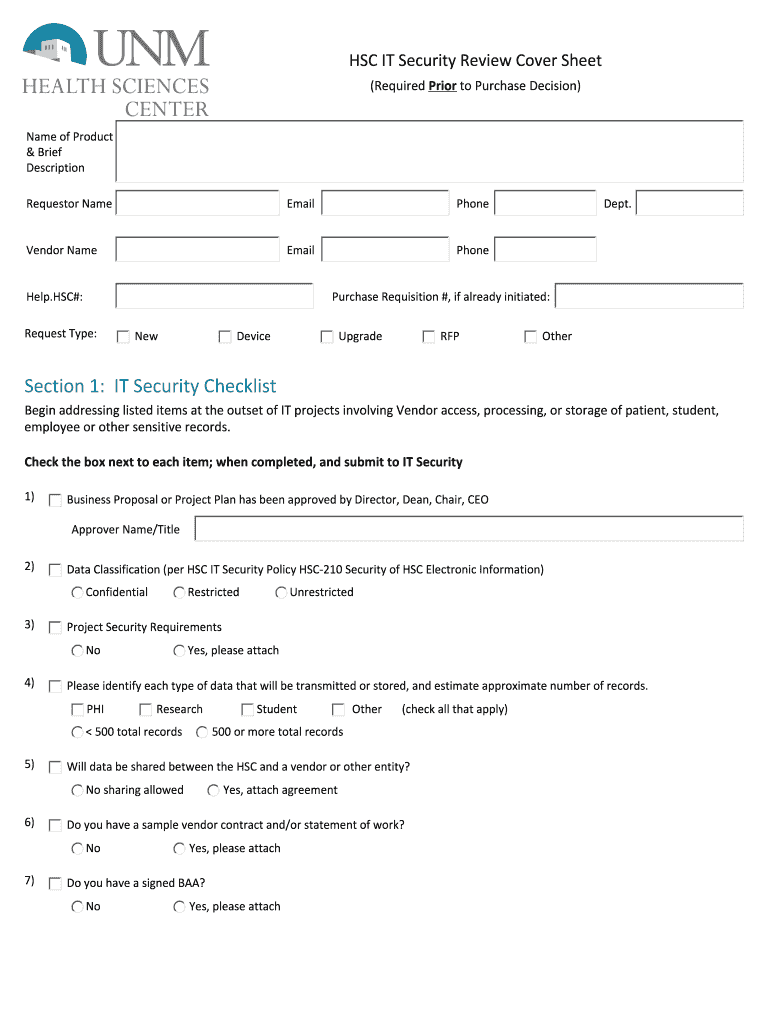
Section 1 It Security Checklist Form
Use a Section 1 IT Security Checklist 0 template to make your document workflow more streamlined.
What this security checklist form does
Section 1 It Security Checklist Form records the first section of an organization’s information-security review, including assigned controls, responses, approvals, and supporting evidence. With signNow, upload the form, let the platform identify fillable fields, assign each field to the responsible reviewer, and send the document for completion and e-signature. The resulting record combines the completed responses with an audit trail showing signer actions and timestamps. Because the form’s exact issuing authority and retention rule are not provided, apply the organization’s approved security policy and applicable industry requirements.
Who uses this security checklist
Security teams
IT security teams use the checklist to document control reviews, assign evidence requests, and retain approvals for internal governance. Security managers can route specific sections to infrastructure, identity, compliance, or risk owners while maintaining one auditable record for the review cycle.
Compliance teams
Compliance and operations teams use the checklist to coordinate responses across departments. A signNow template can preserve recurring field assignments, capture signatures from accountable reviewers, and store the completed form with its audit trail for later assessment.
Business types that use this checklist
The form fits organizations that need accountable reviewers, documented approvals, and a retrievable record of Section 1 security controls.
Solo security consultants can use the Section 1 IT Security Checklist Form to collect client responses, request approvals, and return a signed assessment record without coordinating paper copies across organizations. Mid-sized compliance teams can reuse a signNow template, route individual control sections to accountable reviewers, and preserve the completed checklist and audit trail for governance or customer assurance reviews. Enterprise security departments can connect checklist completion with systems such as Microsoft 365, NetSuite, Box, or Google Drive while administrators manage access, templates, and evidence retention across business units.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features that support checklist completion
Section 1 IT Security Checklist Form workflows benefit from structured fields, assigned reviewers, audit evidence, and controlled storage through signNow.
Field detection
Upload the Section 1 IT Security Checklist Form and let signNow identify fillable areas, reducing manual field placement before review and signature routing.
Role routing
Assign checklist responsibilities to named recipients, then send the required fields in sequence so each reviewer completes the correct security control section.
Structured completion
Capture signatures, initials, dates, and required responses in one controlled document, preserving the completed Section 1 checklist for internal review.
Reusable templates
Use reusable templates for recurring Section 1 IT Security Checklist Form reviews, while keeping field assignments consistent across departments and reporting cycles.
Audit evidence
Generate an audit trail showing signer identity, timestamps, actions, and document history, giving security teams evidence of how the checklist was completed.
System connections
Connect completed checklists with supported systems such as Microsoft 365, Google Drive, Box, or NetSuite for organized downstream record handling.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the security checklist workflow works
signNow turns the Section 1 IT Security Checklist Form into a routed digital workflow from upload through signed record storage.
Upload form: Upload the Section 1 IT Security Checklist Form Detect fields: Auto-detect fillable fields for review Route checklist: Assign security reviewers and send Complete record: Collect signatures and store audit trail
What the checklist audit trail records
The audit trail separates technical evidence from document setup, showing who acted on the Section 1 IT Security Checklist Form and when.
Authenticate signer:
Capture timestamp:
Record document:
Seal history:
Log actions:
Export trail:
Recommended checklist workflow settings
Configure the Section 1 workflow around accountable reviewers, reproducible evidence, and the organization’s documented security controls.
| Security setting | Recommendation |
|---|---|
| Authentication method | Email invitation with stronger verification when required |
| Signature type | Typed or drawn electronic signature with intent |
| Audit trail | Retain signer actions, timestamps, and document history |
| Document retention | Follow the organization’s approved security records policy |
| Encryption | TLS 1.2/1.3 in transit and AES-256 at rest |
Security controls for this checklist
Data encryption:
Security certification:
Information security:
Privacy compliance:
Healthcare compliance:
Encryption standards:
Platform requirements for checklist access
Complete the Section 1 IT Security Checklist Form in Chrome, Firefox, Safari, or Edge on Windows and macOS. signNow also provides mobile apps for iOS and Android, with data protected in transit using TLS 1.2/1.3.
Browser support Chrome, Firefox, Safari, and Edge Operating systems Windows, macOS, iOS, and Android Connection security TLS 1.2/1.3 required for transport
Organizations should review managed-device policies before enabling checklist access. For connected workflows, confirm API, SSO, and storage permissions with the security administrator. Retain exported audit evidence according to the organization’s documented records policy and any applicable industry requirement.



Best practices for completing the form
Accurate field ownership, controlled templates, preserved audit evidence, and risk-based authentication make Section 1 checklist records easier to review and defend.
Assign every field to an owner
Validate the reusable checklist template
Preserve the record and audit trail
Match authentication to document sensitivity
Challenges when completing the checklist
Reviewers may complete the wrong Section 1 control when field ownership and signing order are not assigned before sending. Uncontrolled copies can separate checklist responses from the signed record, making later audit-trail retrieval and evidence review more difficult. Shared credentials weaken attribution because the audit trail may not clearly connect each Section 1 response with its responsible reviewer. Incomplete security evidence can leave required checklist fields unanswered even when the document appears to be fully signed.
Troubleshooting checklist workflows
Use these answers to resolve specific routing, authentication, audit-trail, compliance, and plan questions for Section 1 IT Security Checklist Form.
signNow’s Business plan includes templates and audit trails for routing the checklist. Review recipient email addresses, required fields, and signing order before sending. If recurring distribution requires bulk send, Business Premium adds that capability; confirm the selected plan before creating the workflow.
A signer can usually access the document through the email invitation without creating an account. If stronger attribution is required, configure an available authentication method, such as SMS-based verification where supported. Document the chosen control in your Section 1 review procedure.
The Section 1 checklist can be routed through signNow’s audit-trail workflow, which records timestamps, actions, and document history. The Business plan includes audit trails; authorized administrators should retrieve the completed evidence and store it under the organization’s retention policy.
HIPAA applies when the checklist workflow contains protected health information, not merely because it concerns security. signNow lists HIPAA compliance with a BAA required. Confirm that the organization has the required BAA and has configured access controls before processing PHI.
Business Premium includes bulk send, while Enterprise adds advanced signer authentication, formula fields, and conditional fields. Choose the plan based on the actual Section 1 routing design rather than assuming every plan provides the same controls.
Electronic signatures for U.S. business records generally rely on signer intent, consent, attribution, and record retention under ESIGN and applicable UETA rules. Keep the completed checklist and audit trail reproducible, and check whether a separate organizational policy requires additional approval.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.