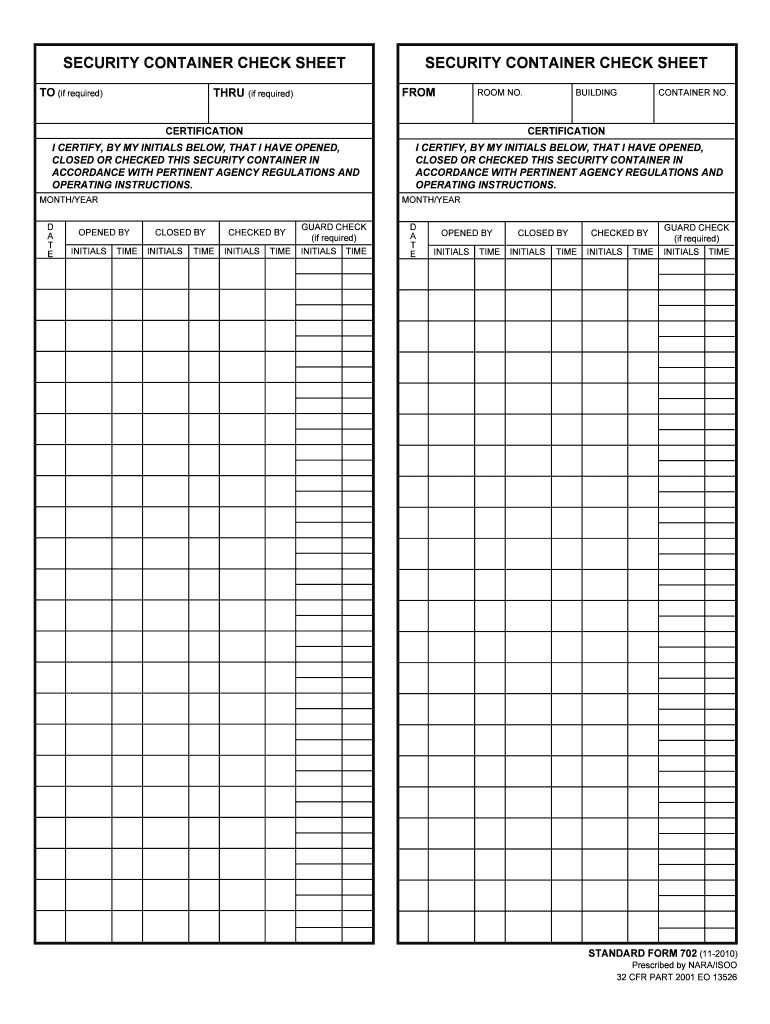
SF702 Security Container Check Sheet Toif Form
Use a Sf702 pdf SECURITY CONTAINER CHECK SHEET TOif template to make your document workflow more streamlined.
What the SF702 check sheet records
The SF702 Security Container Check Sheet Toif Form is a controlled record for documenting security-container checks and related review activity. It is completed by entering the information required by the organization’s SF702 procedure, assigning responsible personnel, reviewing the record, and preserving the final version. With signNow, a sender uploads the SF702, auto-detects or places fillable fields, routes it to assigned signers, and stores the completed document with an audit trail. The form’s exact agency instructions and retention schedule should govern any field-specific decision.
Who benefits from structured SF702 workflows
The SF702 is most useful where security-container checks must be assigned, reviewed, and preserved as an accountable organizational record.
Federal facility teams use the SF702 to document recurring security-container checks, assign review responsibility, and preserve evidence that each required inspection was completed under the facility’s approved procedure. Contractors supporting controlled environments use reusable SF702 templates to collect authorized checks, route records for review, and keep completed documents available for contract or compliance audits. Enterprise security administrators coordinate multiple locations by controlling signNow access, delegating sending, and retaining consistent SF702 records without allowing every employee to modify the underlying template.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Key features for the SF702 check sheet
signNow combines document preparation, controlled routing, electronic signatures, and audit evidence for teams handling the SF702 Security Container Check Sheet Toif Form.
Document preparation
Upload the SF702 Security Container Check Sheet Toif Form and preserve its original layout while preparing fields for completion, review, and electronic signing in one controlled workspace.
Reusable templates
Reusable templates help security personnel apply the same SF702 completion sequence across recurring inspections without recreating fields or instructions for every container check.
Signer routing
Signer routing sends the completed SF702 to the assigned reviewer, reducing handoffs and keeping responsibility visible throughout the approval process.
Audit trail
Audit trails record timestamps, signer actions, and document history, giving administrators a clearer record of how this SF702 moved from preparation to completion.
Mobile access
Mobile apps let authorized personnel review or sign the SF702 away from a desk, supporting inspections conducted at facilities, offices, or controlled locations.
Record retrieval
Completed documents remain organized with their signing evidence, making it easier to retrieve the SF702 and demonstrate document history during an internal review.
Recommended SF702 workflow setup
Configure the SF702 workflow around controlled access, traceable review, protected storage, and the organization’s applicable records policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Enable completion certificate and action history |
| Document retention | Follow agency and records policy |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How to complete the SF702 online
Use signNow to prepare the SF702, assign responsibility, collect signatures, and preserve the completed document with its audit evidence.
Upload form:
Upload the completed SF702 source document. Prepare fields:
Review detected fields and add missing inputs. Route document:
Assign reviewers or signers in order. Store evidence:
Download the completed record and audit trail.
What the SF702 audit trail captures
An audit trail separates the approved SF702 record from an unverified copy by preserving signer activity, timing, document history, and retrieval evidence.
Authenticate signer:
Timestamp action:
Hash document:
Seal record:
Protect history:
Export trail:
Security controls for SF702 records
Transit encryption:
Stored encryption:
Security certification:
Management standard:
U.S. eSign compliance:
Privacy controls:
Risks of incomplete SF702 records
Signer identity
Record history
Document integrity
Inspection evidence
SF702 retention periods and authorities
The SF702 itself has no retention period supplied here. Match the record to its actual use, then apply the controlling federal, agency, or state schedule rather than importing another form’s deadline.
Three years from filing
Six years from creation
Later of two dates
Six years for records
Agency schedule controls
Best practices for SF702 records
Treat the SF702 as a controlled security record: preserve its approved structure, capture signing evidence, apply the correct retention authority, and restrict access after completion.
Preserve the approved SF702 layout
Export the audit evidence with each record
Apply the controlling retention schedule
Archive the final SF702 securely



Key performance indicators that demonstrate SignNow's proven track record.
SF702 completion and troubleshooting
These answers address preparation, signer controls, legal evidence, retention, and corrections for the SF702 Security Container Check Sheet Toif Form.
Upload the original SF702 as a PDF or supported document, then use signNow’s field-detection workflow to identify fillable areas. Review every detected field manually because the platform cannot determine which checks your agency procedure requires or whether a field belongs to the approved SF702 version.
The signNow Business plan includes templates, audit trails, mobile apps, and legally binding eSignatures at $8 per user per month when billed annually. If the SF702 process needs bulk send, Business Premium is listed at $15 per user per month annually.
An SF702 signature can be supported by signNow’s audit trail, which records signing actions, timestamps, and document history. ESIGN and UETA provide the U.S. legal framework, but agency rules may impose additional authentication or in-person requirements.
Use signNow’s SMS OTP or another configured authentication method when the SF702 procedure requires stronger signer attribution. Advanced signer authentication is available in Enterprise, while the required control should be selected from the agency’s security policy.
If a completed SF702 contains protected health information, the workflow must address HIPAA requirements and signNow’s HIPAA compliance requires a business associate agreement. Retain the record for six years from creation or its last effective date under 45 CFR §164.530(j).
Do not treat the signNow completion certificate as permission to change the approved form. If an SF702 entry is wrong, follow the organization’s correction procedure, preserve the original evidence, and create a controlled replacement record rather than silently editing the signed PDF.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.