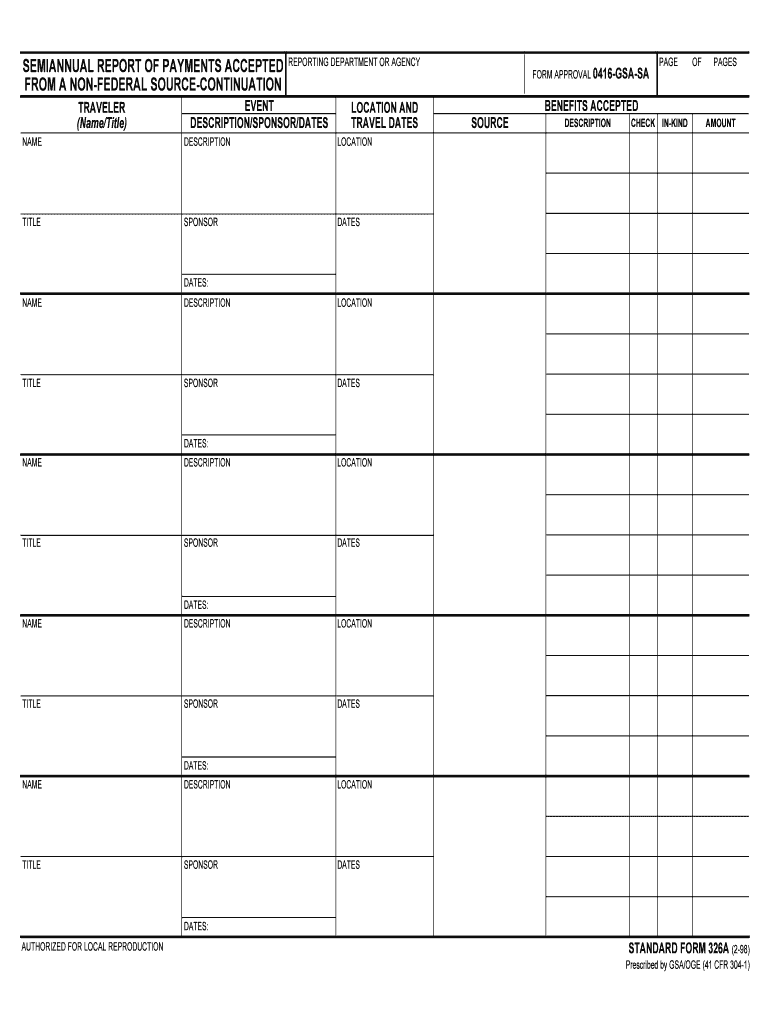
Semiannual Report Of Payments Accepted From A Non Gsa Form
Use a Semiannual Report Of Payments Accepted From A Non GSA template to make your document workflow more streamlined.
What this payment report records
The Semiannual Report Of Payments Accepted From A Non Gsa Form is a record for documenting payments accepted outside a GSA process during a six-month reporting period. In practice, the preparer enters the covered payment details, identifies the responsible parties, obtains required review or signatures, and preserves the completed report. signNow can support the document workflow by uploading the form, detecting fillable fields, routing it to authorized signers, recording each signing event, and storing the finished PDF with its audit trail. Confirm the form’s governing agency instructions before filing or submission.
Who uses this payment report
Government contractors
Government contractors and finance teams use this report to document payments accepted outside GSA channels, route required approvals, and preserve signed records for internal review. signNow helps assign fields, collect signatures, and retain an audit trail tied to each completed report.
Finance departments
Accounts-payable departments and authorized recipients use the report to confirm semiannual payment activity, resolve missing information, and share a completed copy with reviewers. A controlled signNow workflow keeps the form version, signer actions, and completion record together.
How this payment report workflow works
The signNow workflow moves this report from an uploaded document to a reviewable signed record without changing the underlying payment information.
Upload report: Upload the Semiannual Report Of Payments Accepted From A Non Gsa Form. Prepare fields: Review detected fields and place missing signer fields. Route report: Send the report to authorized recipients for review. Complete record: Collect signatures and preserve the completed audit trail.
Recommended setup for payment reports
Configure the report workflow around verified signer identity, traceable approvals, protected storage, and the organization’s approved retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP addresses, and actions |
| Document retention | Retain completed records under agency policy |
| Encryption | Use TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the audit trail records each report
The audit trail records technical evidence around signing the payment report, from signer authentication through retrieval of the completed record.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Link evidence:
Export trail:
Features for completing this report
signNow organizes the specific report workflow around field preparation, authorized review, electronic signatures, and preserved completion evidence.
Document upload
Upload the exact Semiannual Report Of Payments Accepted From A Non Gsa Form and keep its original layout while preparing the signing workflow.
Field detection
Auto-detect fillable areas, then review each field before adding missing payment, approval, date, or signature fields.
Signer routing
Route the report to named recipients in the required order, reducing uncertainty about who must review or sign each section.
Electronic signing
Collect typed or drawn electronic signatures while preserving intent, signer attribution, timestamps, and action history for the completed report.
Audit evidence
Export the signed PDF with its audit trail so accounting or authorized reviewers can connect the report to its completion evidence.
Controlled templates
Use templates and role-based access to keep recurring semiannual reports consistent without allowing unauthorized users to change the workflow.
Security controls for this payment report
Transport encryption:
Stored encryption:
Security certification:
Security management:
Health data safeguards:
Signature compliance:
Record-keeping practices for this report
Accurate source data, preserved audit evidence, and controlled access make a completed payment report easier to review and defend.
Retain the report with its audit evidence
Reconcile payment details before signature
Export the signed record and audit trail
Secure access to sensitive payment information
Challenges when preparing this report
Payment totals may not reconcile with source ledgers when accepted payments are entered from multiple offices or reporting systems. Missing signer roles, dates, or approval fields can delay completion and leave the semiannual report difficult to validate. Using an outdated report template can place accepted-payment details in the wrong fields or omit required review information. Separating the signed report from its audit trail makes later agency, accounting, or internal review harder to complete.
Legal value of the completed report
A completed Semiannual Report Of Payments Accepted From A Non Gsa Form can provide organized evidence of the reported payment activity when signer intent, attribution, consent, and record preservation are established. ESIGN and UETA generally recognize qualifying electronic signatures, but filing rules and agency acceptance should be confirmed for the applicable transaction.



Questions about completing this report
Use these answers to resolve field, signing, retention, and compliance questions before sending the payment report for approval.
On the Business plan, upload the original report and inspect every detected field before sending. Auto-detection assists placement but does not verify payment amounts, reporting periods, or agency-specific requirements. Compare the prepared document with the source form before routing it for signatures.
signNow Business includes legally binding eSignatures, templates, and audit trails. For a report involving protected health information, HIPAA compliance requires a BAA. Confirm the account configuration and organizational controls before placing PHI in this document workflow.
Electronic signatures generally receive legal recognition under ESIGN and UETA when intent, consent, attribution, and record retention are established. Those statutes do not confirm that a specific agency accepts this report electronically, so verify the governing filing instructions.
Business Premium includes bulk send, which can help distribute recurring report instances. The Business plan does not include that listed feature. Do not use bulk send to bypass report-specific review; each completed report still needs accurate payment data and authorized approval.
Use signNow’s audit trail and completion certificate to preserve signer actions, timestamps, and related evidence. Export the signed report and audit trail together, then store them under the organization’s approved records policy.
If the report includes consumer-facing electronic records, ESIGN’s consumer-consent requirements may apply, including access to the electronic format and procedures for withdrawing consent under 15 U.S.C. §7001(c). Obtain the required disclosure before requesting a signature.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.