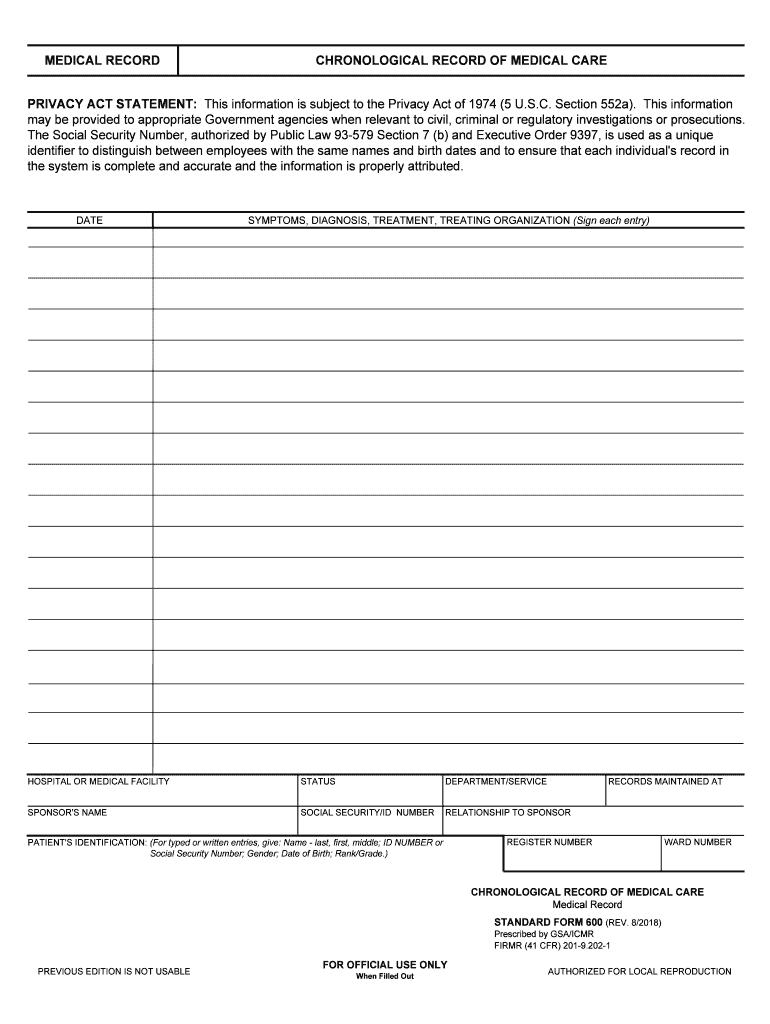
Medical Record Privacy Act Statement This Gsa Form
Use a MEDICAL RECORD PRIVACY ACT STATEMENT This GSA template to make your document workflow more streamlined.
What this medical privacy statement does
The Medical Record Privacy Act Statement This Gsa Form documents how a patient’s medical information may be handled, disclosed, or acknowledged by the responsible healthcare organization. It is completed by entering the patient and authorized representative details, identifying the privacy purpose or disclosure, reviewing any stated limits, and signing the record. When used with signNow, a sender uploads the statement, reviews detected fields, assigns signers, sends it electronically, and retains the completed PDF with its audit trail. HIPAA documentation requirements under 45 CFR §164.530(j) and applicable state law still govern the organization’s records process.
How this medical statement works
The signNow workflow converts the Medical Record Privacy Act Statement This Gsa Form into an assigned, auditable signing process for healthcare records.
Upload form: Upload the completed GSA statement PDF. Check fields: Review detected fields and add missing fields. Assign signers: Assign patient and representative roles. Complete record: Send, sign, and retain the completed record.
Complete the medical privacy statement
Use this sequence to prepare the statement, assign the correct healthcare participants, collect signatures, and preserve the completion record.
Upload form:
Upload the GSA statement PDF. Detect fields:
Let signNow detect fillable fields. Assign roles:
Assign patient and representative fields. Send statement:
Send the statement for signature. Archive record:
Store the signed copy and audit trail.
Recommended medical statement setup
Configure the statement workflow around authorized access, protected health information, audit evidence, and the HIPAA six-year documentation rule.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS verification for authorized representatives |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture IP, timestamps, and action history |
| Encryption and retention | AES-256 at rest; retain six years under HIPAA |
| User provisioning | Assign named senders and least-privilege access |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for medical privacy records
HIPAA protection:
SOC 2 certification:
ISO certification:
Stored encryption:
Transit encryption:
Audit evidence:
Use medical privacy forms on mobile devices
Complete the Medical Record Privacy Act Statement This Gsa Form through signNow on iOS 15 or later and Android 10 or later. The mobile apps support document capture and signing while TLS protects data in transit.
iPhone app iOS 15 and later with the signNow mobile app Android app Android 10 and later with the signNow app Camera capture Capture paper statements using the device camera
Organizations handling protected health information should manage iOS and Android devices through approved controls, restrict local document access, and confirm the required signNow plan and BAA before sending patient-related statements. Offline work should follow the organization’s approved synchronization and retention procedures.



Organizations that use this statement
This form is most useful when healthcare teams must document patient privacy decisions consistently across staff, locations, and authorized representatives.
Solo physicians use the statement to document a patient’s privacy acknowledgment or disclosure authorization without requiring an office-based paper exchange. A signNow template can standardize patient, representative, purpose, and signature fields while preserving the completed record and audit trail. Community clinics use the statement for patient-facing privacy workflows across locations. Assigned staff can send the correct version, collect signatures from patients or authorized representatives, and route completed records into approved storage while maintaining access controls for protected health information. Hospital enterprise teams use the statement across departments when privacy acknowledgments or disclosures require consistent routing. Central administrators can manage templates, signer roles, authentication, retention, and audit evidence for large-scale clinical operations.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
What the audit trail records
The audit trail records evidence around this statement’s signing event rather than replacing the statement’s privacy language or clinical authorization requirements.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper sealing:
Completion certificate:
Audit export:
Privacy challenges to address
Sending the statement to the wrong recipient can disclose protected health information beyond the patient’s stated authorization or intended purpose. Leaving representative, purpose, or disclosure-limit fields blank can make the signed statement incomplete for the healthcare organization’s privacy process. Storing the signed statement separately from its audit trail can weaken the organization’s ability to demonstrate who signed and when. Using unrestricted shared links can expose a medical privacy statement to an unintended signer or unauthorized viewer.
Best practices for retaining statements
Retain the signed statement, audit evidence, and access records together while applying the rule that fits the healthcare organization’s documented obligations.
Apply the HIPAA six-year rule
Preserve audit evidence securely
Validate every required field
Document the approved workflow
Troubleshoot medical privacy statement signing
Resolve field, signer-authentication, HIPAA, and plan questions before sending this medical privacy statement for signature.
If the statement contains protected health information, use a signNow plan with HIPAA compliance and execute the required BAA. HIPAA compliance does not replace your privacy, access-control, minimum-necessary, and retention policies. Review recipients before sending and limit each signer’s access to the required fields.
The signNow Business plan includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, SOC 2, and GDPR support. HIPAA compliance requires the appropriate arrangement, including a BAA, so confirm plan eligibility before processing protected health information.
Upload the statement again if field detection misses labels, then place signature, date, and acknowledgment fields manually. Check that the patient or authorized representative receives only the intended document and that every required field is assigned to the correct signer.
Use SMS authentication when email-only identification is insufficient, or choose advanced signer authentication where available under the selected plan. Record the authentication method in your internal procedure and verify that the signer is authorized to disclose or receive the medical information.
A signed statement can be supported by intent, consent, attribution, and retained reproducible records under ESIGN, 15 U.S.C. chapter 96, and applicable UETA law. Keep the completed document and audit trail together, and check state-specific medical-record requirements before relying on it.
The signNow Business Premium plan adds bulk send and kiosk mode, while Enterprise adds advanced signer authentication. Business includes audit trails and templates. Select the plan based on whether the organization sends individualized statements, collects signatures onsite, or requires stronger authentication controls.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.