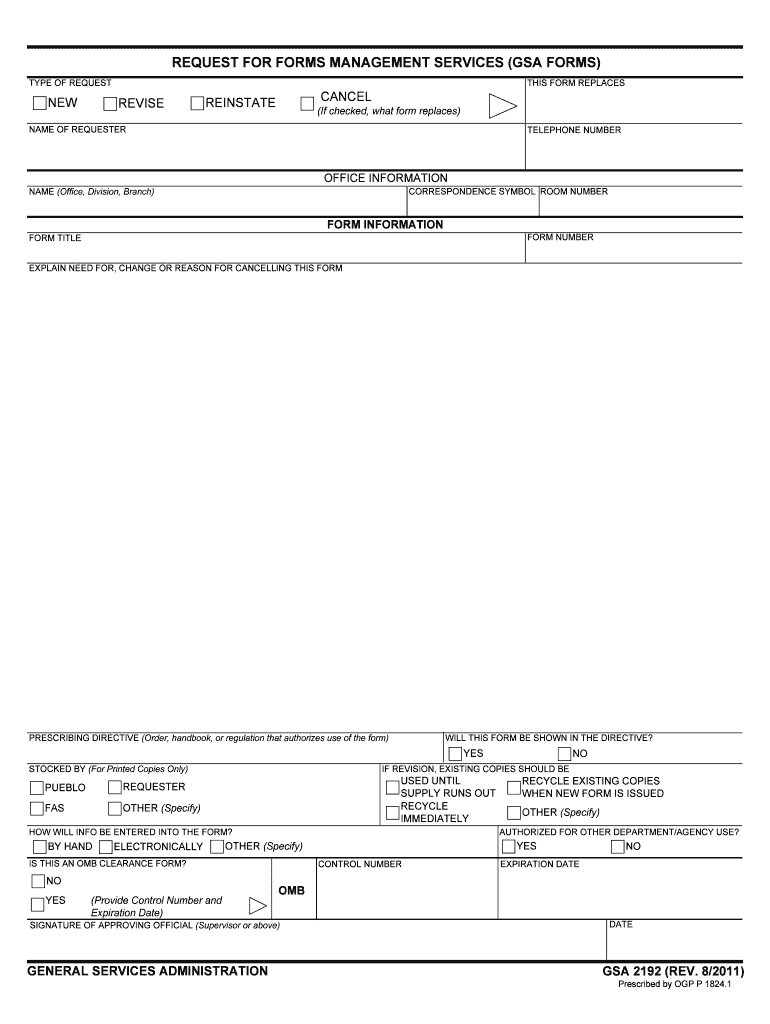
Gsa 2192 Request For Forms Management Services Gsa
Use a GSA 2192 Request For Forms Management Services GSA template to make your document workflow more streamlined.
What the Gsa 2192 is and how it works
The Gsa 2192 Request For Forms Management Services Gsa is an administrative request used to document a need for forms-management services and route that request for review and approval. Its exact fields, attachments, and approval requirements depend on the issuing GSA process and the current form version, so users should work from the applicable source document. With signNow, a sender uploads the form, places or confirms fillable fields, assigns recipients, sends the request, collects signatures, and stores the completed document with its audit trail.
Key features for the Gsa 2192
signNow combines field preparation, routed approvals, electronic signatures, and audit evidence for teams processing the Gsa 2192 Request For Forms Management Services Gsa.
Form preparation
Upload the Gsa 2192 as a PDF, identify fillable areas, and place assigned fields without recreating the government request in another format.
Role-based routing
Route service details and approval fields to designated participants in sequence, reducing manual forwarding and preserving the intended review order.
Electronic signing
Collect signatures, initials, dates, and acknowledgments electronically while retaining evidence of the actions associated with the completed request.
Audit trail
Keep the signed Gsa 2192 connected to its completion record, timestamps, and action history for later administrative review.
Reusable template
Use reusable templates when the same Gsa 2192 workflow is repeated, while preserving controlled field placement and recipient assignments.
Record storage
Connect completed documents to systems such as Google Drive, Box, or Microsoft 365 for organized records access after approval.
Recommended Gsa 2192 workflow setup
Configure the Gsa 2192 workflow around identifiable signers, documented approvals, protected records, and the applicable agency retention schedule.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with two-factor authentication |
| Signature type | Electronic signature with signer intent |
| Audit trail | Enable completion evidence and action history |
| Document retention | Apply the agency records schedule |
| Encryption | Use TLS 1.2/1.3 and AES-256 protection |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the Gsa 2192 audit trail works
After signing, signNow records identity, timing, document integrity, and retrieval evidence so the Gsa 2192 can be reviewed as a complete transaction.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log actions:
Export evidence:



Security for the Gsa 2192 workflow
Data in transit:
Data at rest:
Independent controls:
Information security:
Protected information:
Electronic signatures:
Challenges when completing the Gsa 2192
Identifying every required field before routing the Gsa 2192 can prevent incomplete requests and repeated exchanges with the reviewing office. Assigning the wrong signer or approval sequence can delay authorization for forms-management services and weaken the document’s process record. Using inconsistent service descriptions, quantities, or supporting attachments can make the request difficult to evaluate and reconcile. Storing the completed request without its audit trail can make later verification of signer identity, timing, and document integrity more difficult.
Best practices for the Gsa 2192
Accurate field assignment, controlled routing, and complete record retention help preserve the Gsa 2192’s administrative history from preparation through approval.
Validate the form before routing
Assign every field explicitly
Preserve the approval sequence
Archive the record and audit trail
Platform requirements for the Gsa 2192
The Gsa 2192 workflow can be prepared and signed through signNow using supported desktop browsers and mobile applications. A current internet connection, a readable source file, and access to the assigned email or authentication method are required for routing and signing.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows and macOS desktops Mobile apps iOS and Android apps
Organizations handling sensitive government or business records should manage devices, access permissions, and storage destinations centrally. Before deployment, administrators should confirm that the selected signNow plan supports required authentication, integrations, retention procedures, and any agency-specific controls applicable to the Gsa 2192.
Key performance indicators that demonstrate SignNow's proven track record.
Gsa 2192 troubleshooting questions
Use the form’s issuing instructions first, then check field assignment, signer identity, audit evidence, and retention controls in the signNow workflow.
Upload the original Gsa 2192 PDF again and inspect whether text fields are flattened or image-only. signNow can place fields manually when automatic field detection cannot identify writable areas. Confirm each field’s recipient assignment before sending the request.
The sender should verify the recipient email, resend the invitation, and check spam filtering. If stronger attribution is needed, use available authentication controls such as two-factor authentication. The audit trail should record the delivery and signing events after the recipient completes the form.
The Business plan includes legally binding eSignatures, templates, mobile apps, audit trails, ISO 27001, SOC 2, and GDPR support. Business Premium adds bulk send, while Enterprise adds advanced signer authentication and additional fields.
Electronic signing generally requires demonstrated intent, consent, attribution, and a retained reproducible record under ESIGN and applicable UETA rules. For consumer-facing records, review the ESIGN disclosure requirements in 15 U.S.C. §7001(c) before routing the Gsa 2192.
Use signNow’s audit trail and completion evidence, then export the completed Gsa 2192 with its transaction history. Store both under the applicable agency or organizational records schedule; no universal Gsa 2192 retention period is established in the supplied authorities.
If the request contains protected health information, HIPAA compliance requires a business associate agreement where applicable. signNow identifies HIPAA compliance as requiring a BAA. Confirm that the Gsa 2192 workflow actually involves PHI before applying healthcare-specific controls.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.