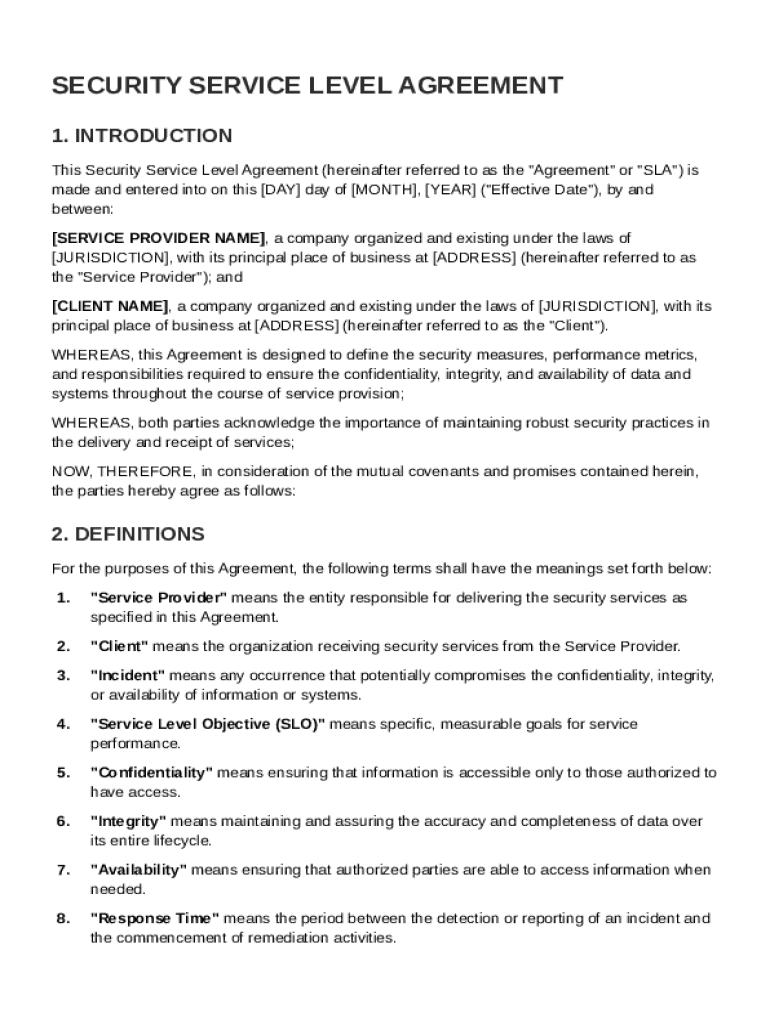
Security Service Level Agreement Form
Use a Security Service Level Agreement Template template to make your document workflow more streamlined.
What the Security Service Level Agreement Form does
The Security Service Level Agreement Form records how a service provider and customer will protect systems, information, access, incidents, and related responsibilities. It is completed by identifying the parties, covered services, security controls, contacts, review obligations, and authorized signers. In signNow, upload the form, let the editor detect fillable areas, assign fields, send it to reviewers and signers, and retain the completed document with its audit trail. ESIGN and UETA can support electronic execution when intent, consent, attribution, and accessible records are established.
Key features for security agreements
The Security Service Level Agreement Form combines defined security commitments, assigned approvals, electronic signatures, and an auditable record for business operations.
Reusable template
Upload the Security Service Level Agreement Form once, then place required fields consistently for every signer and renewal cycle.
Remote signing
Collect signatures remotely while preserving the agreement’s parties, obligations, service terms, and approval history in one controlled workflow.
Role-based fields
Assign fields to named participants so security representatives, vendors, and customers complete only their designated sections.
Signing visibility
Use reminders and status tracking to identify unsigned agreements before service access, onboarding, or renewal decisions are delayed.
Document records
Store the completed agreement with its certificate of completion and audit trail for later contract administration or review.
Connected workflows
Connect signed agreements to business systems so authorized teams can locate the current security commitment without duplicate data entry.
Manage users and permissions
Security administrators create shared templates for recurring vendor agreements, define required fields, and control who may send or edit the Security Service Level Agreement Form. Centralized permissions reduce unauthorized changes before signature and support consistent review across departments. Procurement and account teams use delegated sending to route an approved agreement without changing its security language. Administrators can maintain the source template while authorized staff manage recipient details, reminders, and completion tracking for individual vendors.
How the agreement workflow works
Follow a controlled sequence from the blank agreement to a signed, retrievable security record.
Upload form: Upload the agreement and let signNow detect fillable areas. Assign fields: Assign security, review, and signature fields to participants. Send document: Send the prepared agreement through email or a signing link. Complete record: Collect signatures and store the completed record with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the audit trail records signing
The audit trail separates signer activity from the agreement’s security terms, creating a traceable record of authentication, timestamps, document integrity, and retrieval.
Authenticate signer:
Capture timestamps:
Hash document:
Seal document:
Build audit trail:
Export evidence:
Recommended agreement workflow setup
Configure the Security Service Level Agreement Form around accountable signers, traceable approval activity, protected records, and the organization’s retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email delivery with SMS verification |
| Signature type | Electronic signature with signer intent |
| Audit trail | Retain certificate and action history |
| Document retention | Follow contract and industry policy |
| Encryption | TLS 1.2/1.3 and AES-256 |
Security and data protection
Transport encryption:
Stored encryption:
Security certification:
Information security:
Electronic signatures:
Healthcare safeguards:
Platform requirements for signing
Use the Security Service Level Agreement Form in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android, allowing authorized participants to review and sign from supported devices.
Desktop systems Windows and macOS Mobile apps iOS and Android Supported browsers Chrome, Firefox, Safari, Edge
Organizations should manage devices, browser updates, access permissions, and identity controls according to internal policy. Teams requiring API access, SSO provisioning, advanced signer authentication, or regulated workflows should confirm the relevant signNow plan and configuration before deployment.



Best practices for security agreements
Use precise obligations, accountable routing, controlled records, and documented revisions to keep each Security Service Level Agreement Form useful after signature.
Define every security obligation clearly
Assign fields to accountable participants
Preserve the complete record
Control revisions after signature
Privacy challenges in security agreements
Publishing system names, credentials, or network diagrams inside the agreement can expose sensitive security information beyond the people who need it for review. A missing signer-consent record can weaken evidence that each party intended to execute the Security Service Level Agreement Form electronically under ESIGN. Overbroad access permissions may let staff view vendor security commitments or incident contacts without a documented business need or approved role. Changing an executed agreement without a new signature can create conflicting versions and make it difficult to establish which security obligations govern.
Security agreement use cases
Organizations use this form to record security expectations before vendor onboarding, system access, renewals, or regulated data processing.
Technology services
A technology services team uses the Security Service Level Agreement Form to document vendor controls before granting access to customer systems.
- Security commitments reviewed before onboarding
The team sends the agreement to the vendor’s authorized representative, records each approval, and stores the signed document with its audit trail. This creates a single reference for security obligations, escalation contacts, and review history without relying on email attachments or manually assembled evidence.
Healthcare operations
A healthcare organization uses the Security Service Level Agreement Form when a service provider may handle systems connected to protected information.
- Security terms linked to vendor review
The organization can route the agreement to procurement, security, and the provider for sequential review and signatures. If protected health information is involved, the workflow should be paired with the organization’s HIPAA assessment and any required business associate agreement rather than treated as a substitute.
Security agreement troubleshooting
These answers address signing, authentication, compliance, plan, and recordkeeping questions for the Security Service Level Agreement Form.
On the Business plan, prepare the Security Service Level Agreement Form as a template and assign fields before sending. If the document requires repeated individualized sends, Business Premium adds bulk send; confirm the plan’s annual signature-invite allowance and any overage terms before rollout.
signNow supports audit trails and is listed as ESIGN and UETA compliant. Legal effect still depends on intent, consent, attribution, and record retention under 15 U.S.C. §§ 7001 and 7006 and applicable state law.
If the agreement contains protected health information, signNow identifies HIPAA compliance as requiring a BAA. Obtain the required BAA and configure organizational safeguards; the form alone does not make a vendor relationship HIPAA compliant.
Business includes audit trails, templates, and mobile apps. Business Premium adds bulk send, kiosk mode, request payments, and quick invite links. Enterprise adds formula fields, conditional fields, and advanced signer authentication for more complex routing.
Use signNow’s supported authentication options, such as email delivery or SMS codes, when the agreement requires stronger signer attribution. Advanced signer authentication is listed with Enterprise; select the method required by your internal security policy.
The completed document should remain paired with its audit trail and certificate of completion. Export or retain both according to the organization’s contract, litigation-hold, privacy, and industry-record policies; ESIGN requires records to remain accessible and reproducible.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.