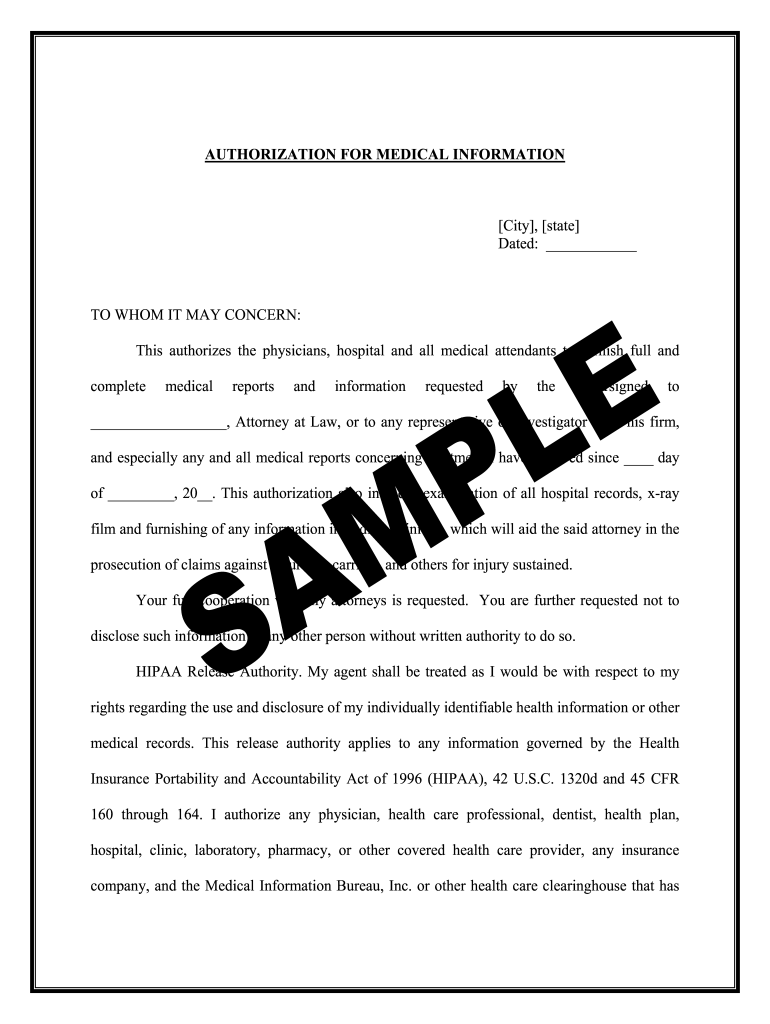
Medical Records Request & Authorization Phoenix Children's Hospital Form
Use a Medical Records Request & Authorization Phoenix Children's Hospital 0 template to make your document workflow more streamlined.
What this medical records form does
The Medical Records Request & Authorization Phoenix Children's Hospital Form records a patient's permission for Phoenix Children's Hospital to disclose specified medical information to an identified recipient. The requester completes patient details, describes the records or dates covered, names the recipient, states the purpose, and sets authorization terms before signing. Hospital staff review the authorization and release only permitted information. signNow can upload the form, detect fillable fields, route it for signature, capture timestamps and signer activity, and store the completed record with an audit trail. HIPAA requires covered entities to retain documentation for six years under 45 CFR 164.530(j).
How the authorization workflow works
Complete the hospital authorization in signNow by moving from document preparation to controlled signing and auditable record storage.
Upload form: Upload the Phoenix Children's Hospital authorization PDF. Detect fields: Auto-detect fields for patient and recipient details. Send signer: Send the authorization to the required signer. Archive record: Store the signed form and audit trail.
Steps to complete the hospital form
Follow these steps to prepare, sign, and retain the Medical Records Request & Authorization Phoenix Children's Hospital Form in signNow.
Upload form:
Upload the hospital authorization PDF. Review fields:
Check patient and recipient fields. Send request:
Send to the authorized signer. Store evidence:
Save the signed form and audit trail.
Ways to complete and sign the authorization
- Use the signNow web app when records staff prepare the Phoenix Children's Hospital authorization on a Windows or macOS workstation and need full field visibility.
- Use the signNow mobile app on iOS or Android when an authorized signer must review and sign the medical records authorization away from a workstation.
- Use kiosk mode for supervised, in-person completion only when hospital policy permits and staff can verify the patient's identity before signing.
- Use a shareable signing link when the hospital has approved controlled link distribution and the recipient can be authenticated before opening the authorization.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended authorization workflow setup
Configure the Medical Records Request & Authorization Phoenix Children's Hospital Form around signer identity, audit evidence, protected health information, and documented retention obligations.
| Setting | Recommendation |
|---|---|
| Authentication method | Email plus SMS OTP for external signers |
| Signature type | Electronic signature with explicit signing intent |
| Audit trail | Capture IP, timestamps, actions, and completion certificate |
| Document retention | Retain six years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2 or 1.3 and AES-256 encryption |
Security for medical record authorizations
HIPAA protection:
Transport encryption:
Stored encryption:
SOC 2 Type II:
ISO 27001:
Electronic signatures:
Privacy and disclosure pitfalls
Sending the authorization to the wrong recipient can disclose protected health information beyond the patient’s stated purpose. An incomplete patient identifier or missing signature can prevent the hospital from validating the authorization before release. Broad record descriptions may authorize more information than intended, increasing privacy exposure during fulfillment. Unrestricted staff access to completed authorizations can expose patient data outside the release-of-information team.
Processing the authorization
The processing sequence depends on accurate form preparation, signer response, hospital review, and secure archival rather than a fixed statutory turnaround period.
Prepare document
Deliver to signer
Complete signature
Archive authorization
Record-keeping practices for authorizations
Preserve the signed authorization, audit evidence, and disclosure context together so Phoenix Children's Hospital can demonstrate what the patient authorized and when.
Verify every disclosure field
Export audit evidence
Restrict protected health information
Apply the controlling period
Platform requirements for medical authorizations
Use Chrome, Firefox, Safari, or Edge on Windows or macOS, or access the signNow mobile app on iOS and Android devices. TLS 1.2 or 1.3 protects data in transit.
Browser support Chrome, Firefox, Safari, and Edge on Windows or macOS. Mobile devices iOS and Android devices support mobile document access. Connection security TLS 1.2 or 1.3 protects browser connections.
Healthcare teams should use managed Windows, macOS, iOS, or Android devices, restrict access to authorized staff, and confirm that signed authorizations remain available for the applicable HIPAA record-retention period. A HIPAA workflow requires a business associate agreement with signNow.



Healthcare authorization use cases
Healthcare teams can apply a structured signNow workflow to patient authorizations while preserving the form's specific disclosure instructions and review requirements.
Healthcare records
A healthcare records team preparing a Phoenix Children's Hospital authorization can upload the document, identify its patient and recipient fields, and route it for signature without rekeying the form.
- Patient authorization routed electronically
- Signed copy retained with audit evidence
The workflow keeps the authorization, signer identity evidence, timestamps, and completed document together. It also gives staff a repeatable process for checking whether the named recipient and requested records match the patient's instructions before disclosure. signNow's HIPAA compliance requires a business associate agreement and does not replace the hospital's authorization review.
Fertility care
Fertility Centers of Illinois uses signNow for healthcare workflows, providing a grounded example of a medical organization using electronic signatures and API-connected processes.
- Healthcare signatures collected online
- API workflows support operational processing
The customer story demonstrates that a healthcare organization can connect signing to operational processes, but it does not establish Phoenix Children's Hospital's specific authorization policy. Teams should preserve the original form language, verify every requested record category, and follow the hospital's release-of-information procedures.
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting medical record authorizations
Resolve field, identity, retention, and compliance questions before releasing records under this Phoenix Children's Hospital authorization.
Upload the original Phoenix Children's Hospital PDF again and confirm that each patient, recipient, purpose, and signature field is assigned to the correct signer. signNow's field detection can accelerate preparation, but staff must compare the detected fields with the source form before sending.
Use signNow's SMS OTP or another configured authentication method, then resend the invitation if the signer cannot complete verification. Authentication supports attribution, but the hospital must still confirm the signer's legal authority to authorize disclosure.
A Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps. For a healthcare workflow involving protected health information, signNow states that HIPAA compliance requires a business associate agreement, regardless of the selected plan.
The completed authorization can be stored with its audit trail, but the hospital remains responsible for applying its records policy and HIPAA's six-year documentation rule under 45 CFR 164.530(j). Do not delete the authorization merely because the signature request is complete.
Electronic signatures can satisfy ESIGN and UETA requirements when intent, consent, attribution, and record reproduction are established. Consumer-facing healthcare records also require the disclosures and access procedures described in 15 U.S.C. §7001(c).
Use signNow's audit trail and completion certificate to review signer actions, timestamps, and IP information. Those records help establish how the authorization was executed, but they do not cure an incorrect recipient, overbroad record description, or missing patient authority.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.