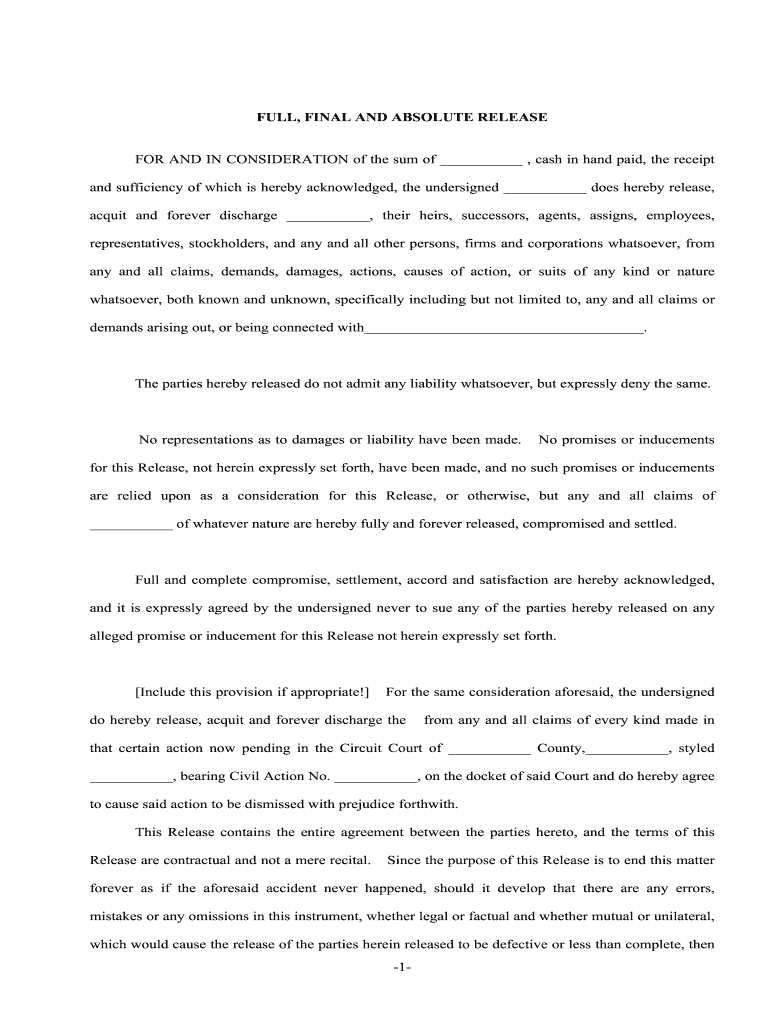
Absolute Release With Covenants Legal Forms
Use a Absolute Release With Covenants Legal Forms template to make your document workflow more streamlined.
What an absolute release form does
An Absolute Release With Covenants Legal Forms document records a party’s unconditional release of specified claims together with promises or covenants that remain binding under the agreement. The form normally identifies the parties, released claims, consideration, effective date, governing law, and execution requirements. With signNow, the approved document can be uploaded, its fields reviewed, and signature requests assigned to each party. Electronic execution may be recognized under the federal ESIGN Act and applicable state law, including UETA, but state notarization, witness, filing, and excluded-document rules still require legal review.
Legal standing of the release
A signed release may be admissible when the record shows signer intent, electronic consent, attribution, and reliable retention and reproduction. The ESIGN Act, 15 U.S.C. ch. 96, and UETA generally support electronic records, but wills, certain court orders, family-law decrees, and other statutory exceptions remain outside ordinary electronic-signature treatment.

Documents and audiences
Legal teams
Release and settlement agreements
Business teams
Vendor, tenant, and service-provider releases
Business users of release forms
The form fits organizations that need documented claim releases, continuing covenants, and reproducible execution evidence.
Solo attorneys use reusable release templates to prepare settlement documents, assign client and counterparty signatures, and preserve the completed instrument with an audit trail for the matter file. Property-management companies use releases after tenant or vendor disputes, routing exact covenant language to authorized parties and retaining signed records alongside the related agreement and payment documentation. Enterprise legal operations teams use controlled templates, delegated sending, and audit-trail exports to process releases across departments while maintaining consistent signer roles and review procedures.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the release workflow works
The workflow moves from the approved release document to verified signatures and an exportable record of completion.
Upload: Upload the approved release PDF Review fields: Review detected covenant and signature fields Send: Send to each releasor in order Archive: Store the signed release and audit trail
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Steps to complete the release
Prepare the exact release language first, then use signNow to place fields, route signatures, and preserve execution evidence.
Upload:
Upload the approved release PDF Check fields:
Review and correct detected fields Assign signers:
Assign each releasor’s signature fields Complete:
Send, monitor, and download the completed record
Features for absolute release forms
signNow connects the release’s approved terms, assigned signers, execution evidence, and final archival record in one documented workflow.
Field detection
Upload the completed release and let signNow identify likely text, date, initials, and signature fields. Correct the placement before sending so every covenant acknowledgment and party execution point is explicit.
Signer routing
Assign each releasor’s fields by name and email, then set the signing order when one party must execute before another. This keeps the release’s execution sequence visible and controlled.
Audit trail
Capture intent, consent, timestamps, IP details, and signing events in the audit trail. The resulting record helps connect each signature to the exact release version presented for execution.
Reusable templates
Use reusable templates for recurring releases while preserving the approved covenant language. Templates reduce re-entry of party names, dates, and signature roles without changing the underlying legal terms.
Mobile signing
Complete a release from a desktop browser or signNow mobile app when parties are working away from the office. Mobile access supports timely execution without converting the document into an informal email attachment.
Record export
Export the signed PDF and completion evidence for controlled storage. Keeping the executed release and audit trail together supports later review of the parties, terms, dates, and signing sequence.
Security for signed releases
Transport encryption:
Stored data:
Security reporting:
Information security:
Electronic signatures:
Health information:



Record-keeping practices for releases
Retain the signed release with its audit evidence, approval history, and supporting records under a documented schedule.
Set a documented retention period
Export the audit trail promptly
Use secure archival storage
Preserve approval and version evidence
Retention schedule for release records
Choose the record class that actually applies to the release and confirm any longer state, contractual, or industry-specific requirement.
Three years for tax records
Six years for understatement
Six years for HIPAA records
Six years for broker records
Thirty years for exposure records
Risks in release execution
Unclear consideration
Misidentified releasor
ESIGN exception
Weak audit record
Privacy pitfalls in release forms
Including unnecessary Social Security numbers, account details, or medical information can expand disclosure risk when the release only needs party and claim identification. Failing to capture electronic consent and paper-record disclosures can weaken the evidence supporting a consumer-facing release under 15 U.S.C. §7001(c). Assigning signature fields to the wrong releasor can undermine attribution, especially when multiple parties share similar names or email addresses. Allowing broad administrator access can expose settlement terms, covenant language, and personal data beyond the staff members handling the matter.
Inside the release audit trail
The audit trail documents technical and signer events surrounding the Absolute Release With Covenants Legal Forms execution.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log activity:
Export evidence:
Troubleshooting release workflows
Resolve field, identity, consent, and legal-scope issues before treating an Absolute Release With Covenants Legal Forms record as complete.
Upload the final Absolute Release With Covenants Legal Forms PDF again, then review signNow’s detected fields before sending. If fields are misplaced, use the editor to correct names, dates, covenant acknowledgments, and signature locations manually.
Business includes templates, audit trails, and legally binding eSignatures at $8/user/month with annual billing. The plan includes 100 signature invites per user annually; overage fees may apply when that allowance is exceeded.
Use signNow’s SMS authentication or another available signer-authentication control when identity risk warrants it. Authentication strengthens attribution, while ESIGN and UETA still require intent, consent, and a reproducible signed record.
For consumer-facing releases, provide the ESIGN Act disclosure, explain the right to receive paper records, confirm electronic access, and explain consent withdrawal procedures under 15 U.S.C. §7001(c). Store evidence of that consent with the completed release.
signNow provides audit trails and document history, while SOC 2 Type II, ISO 27001, AES-256, and TLS describe platform controls. Determine separately whether the release contains PHI; HIPAA workflows require a BAA.
If the release is intended as a will, codicil, testamentary trust, family-law decree, or court filing, do not rely on ordinary electronic signing. ESIGN excludes those categories, and state-law execution or filing requirements may control.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.